Ravi Sir's Cyber Security Cards › Revision Cards
How Defenders Detect Scanning
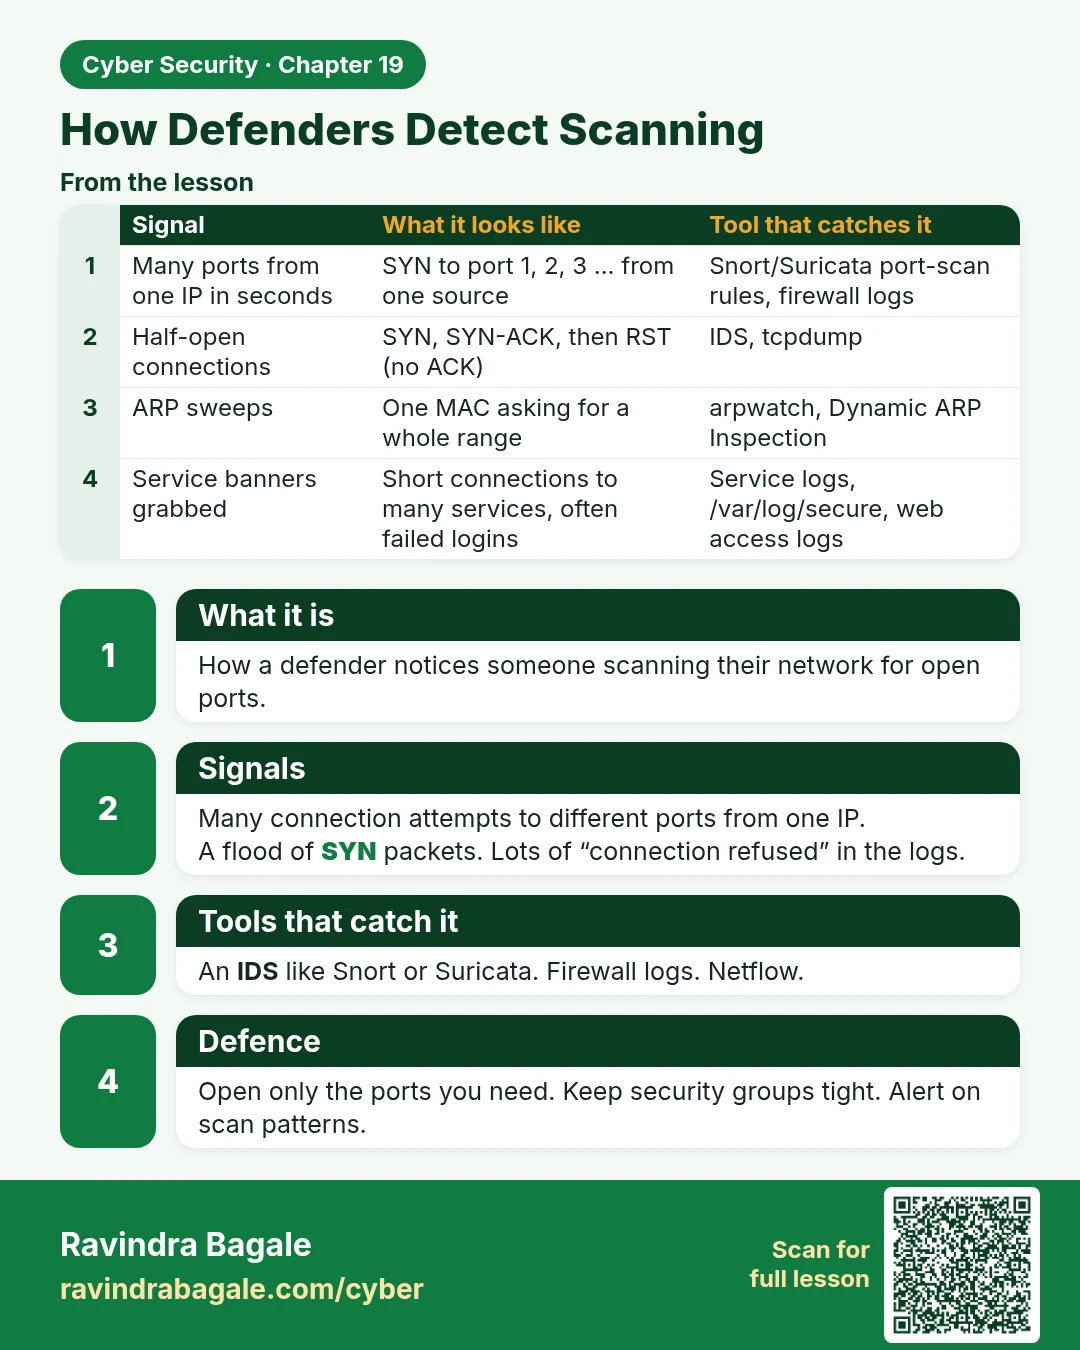
How Defenders Detect Scanning How a defender notices someone scanning their network for open ports. Many connection attempts to different ports from one IP. A flood of SYN packets. Lots of “connection refused” in the logs. An IDS like Snort or Suricata. Firewall logs. Netflow. Open only the ports yo
Read card text
What this card says
What it is
How a defender notices someone scanning their network for open ports.
Signals
Many connection attempts to different ports from one IP.
A flood of SYN packets. Lots of “connection refused” in the logs.
Tools that catch it
An IDS like Snort or Suricata. Firewall logs. Netflow.
Defence
Open only the ports you need. Keep security groups tight. Alert on scan patterns.
| Signal | What it looks like | Tool that catches it |
|---|---|---|
| Many ports from one IP in seconds | SYN to port 1, 2, 3 ... from one source | Snort/Suricata port-scan rules, firewall logs |
| Half-open connections | SYN, SYN-ACK, then RST (no ACK) | IDS, tcpdump |
| ARP sweeps | One MAC asking for a whole range | arpwatch, Dynamic ARP Inspection |
| Service banners grabbed | Short connections to many services, often failed logins | Service logs, /var/log/secure, web access logs |
| Cloud-side | Rejected traffic to your instances | AWS VPC Flow Logs, GuardDuty port-probe findings |
Learn more in the lesson: 19.10 How Defenders Detect Scanning