Ravi Sir's Cyber Security Cards › Revision Cards
From S3, RDS and IAM to Cloud Misconfigurations
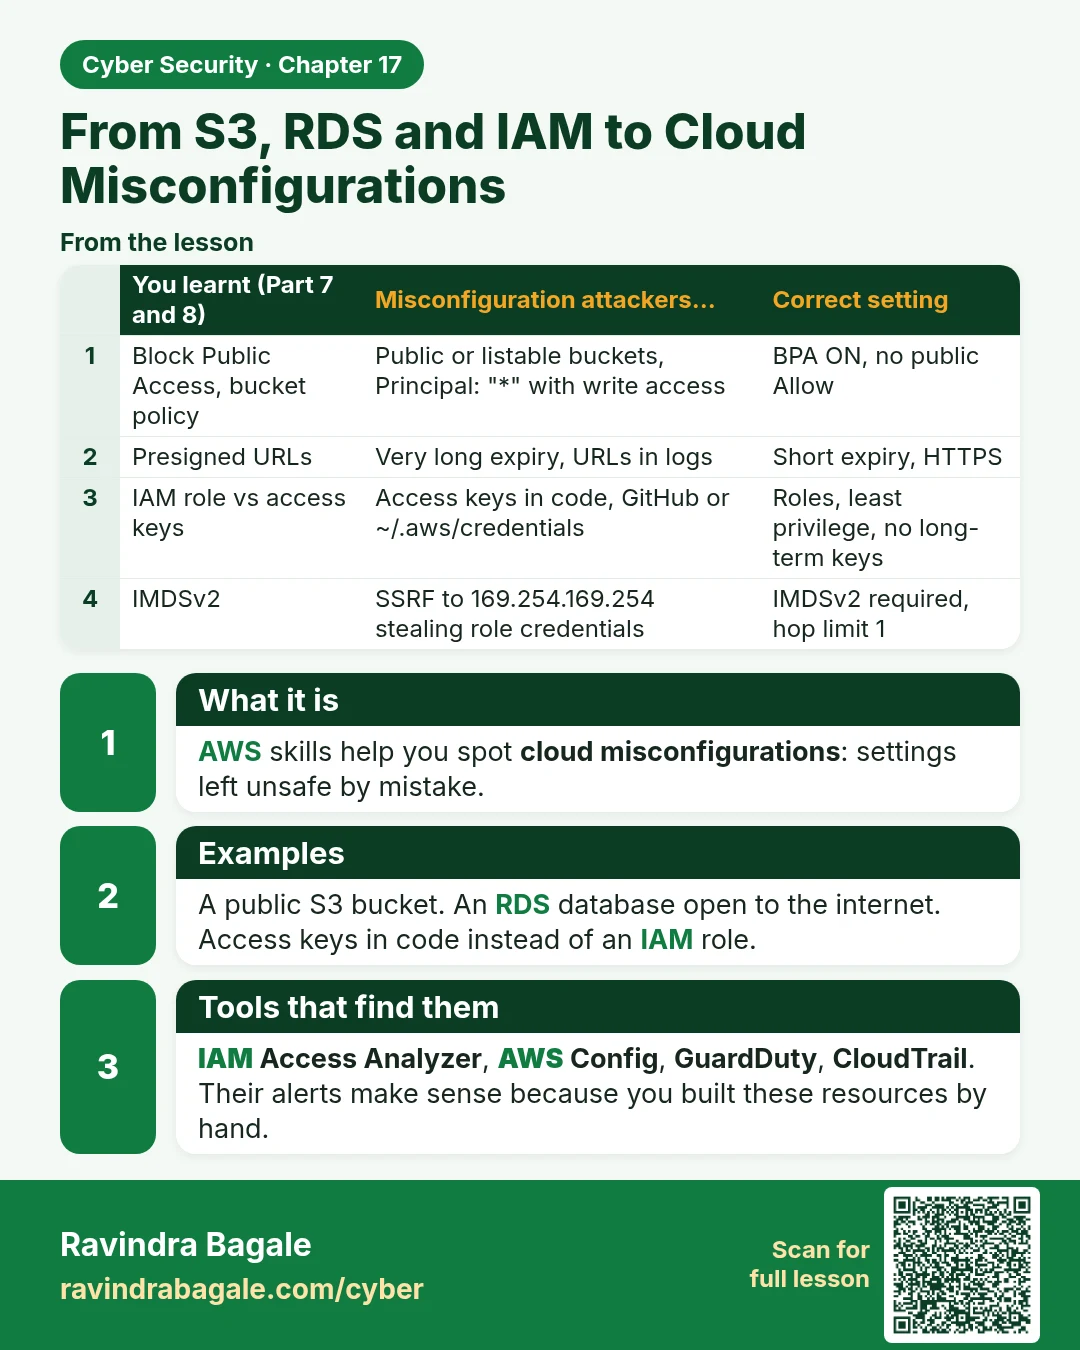
From S3, RDS and IAM to Cloud Misconfigurations AWS skills help you spot cloud misconfigurations : settings left unsafe by mistake. A public S3 bucket. An RDS database open to the internet. Access keys in code instead of an IAM role. IAM Access Analyzer , AWS Config , GuardDuty , CloudTrail . Their
Read card text
What this card says
What it is
AWS skills help you spot cloud misconfigurations: settings left unsafe by mistake.
Examples
A public S3 bucket. An RDS database open to the internet. Access keys in code instead of an IAM role.
Tools that find them
IAM Access Analyzer, AWS Config, GuardDuty, CloudTrail.
Their alerts make sense because you built these resources by hand.
| You learnt (Part 7 and 8) | Misconfiguration attackers… | Correct setting |
|---|---|---|
| Block Public Access, bucket policy | Public or listable buckets, Principal: "*" with write access | BPA ON, no public Allow |
| Presigned URLs | Very long expiry, URLs in logs | Short expiry, HTTPS |
| IAM role vs access keys | Access keys in code, GitHub or ~/.aws/credentials | Roles, least privilege, no long-term keys |
| IMDSv2 | SSRF to 169.254.169.254 stealing role credentials | IMDSv2 required, hop limit 1 |
| RDS public access, db-sg | Database reachable on 3306 from the internet | Private RDS, SG-to-SG rule |
Learn more in the lesson: 17.6 From S3, RDS and IAM to Cloud Misconfigurations