Ravi Sir's Cyber Security Cards › Revision Cards
From Networking to Nmap and Wireshark
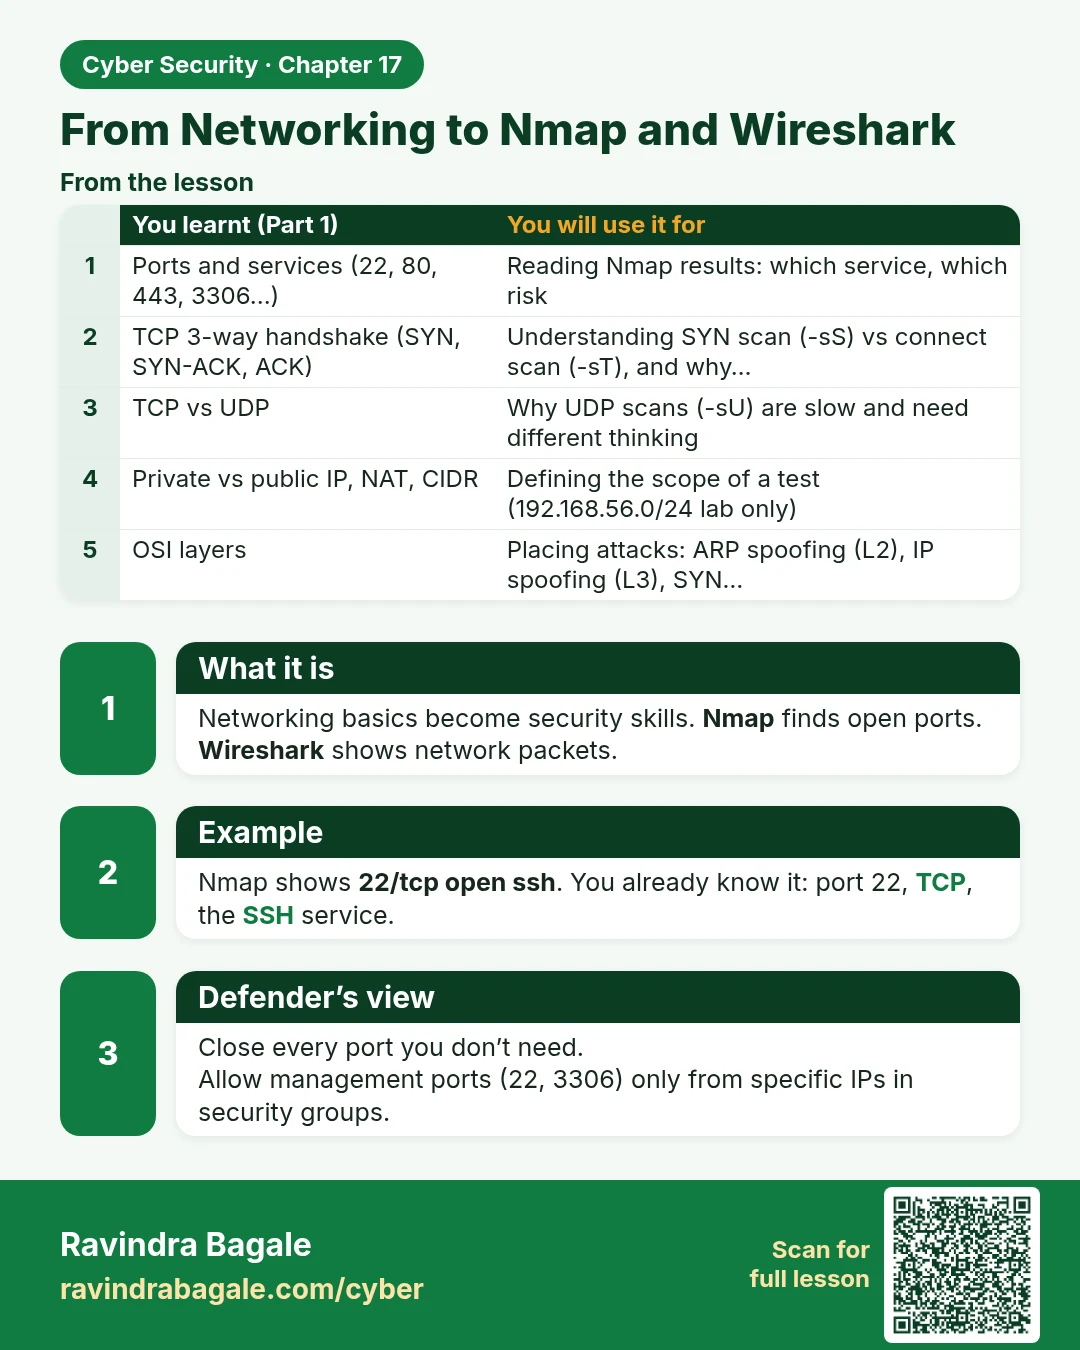
From Networking to Nmap and Wireshark Networking basics become security skills. Nmap finds open ports. Wireshark shows network packets. Nmap shows 22/tcp open ssh . You already know it: port 22, TCP, the SSH service. Close every port you don’t need. Allow management ports (22, 3306) only from specif
Read card text
What this card says
What it is
Networking basics become security skills. Nmap finds open ports. Wireshark shows network packets.
Example
Nmap shows 22/tcp open ssh. You already know it: port 22, TCP, the SSH service.
Defender’s view
Close every port you don’t need.
Allow management ports (22, 3306) only from specific IPs in security groups.
| You learnt (Part 1) | You will use it for |
|---|---|
| Ports and services (22, 80, 443, 3306...) | Reading Nmap results: which service, which risk |
| TCP 3-way handshake (SYN, SYN-ACK, ACK) | Understanding SYN scan (-sS) vs connect scan (-sT), and why… |
| TCP vs UDP | Why UDP scans (-sU) are slow and need different thinking |
| Private vs public IP, NAT, CIDR | Defining the scope of a test (192.168.56.0/24 lab only) |
| OSI layers | Placing attacks: ARP spoofing (L2), IP spoofing (L3), SYN… |
Learn more in the lesson: 17.2 From Networking to Nmap and Wireshark