Ravi Sir's Cyber Security Cards › Revision Cards
From MySQL to SQL Injection
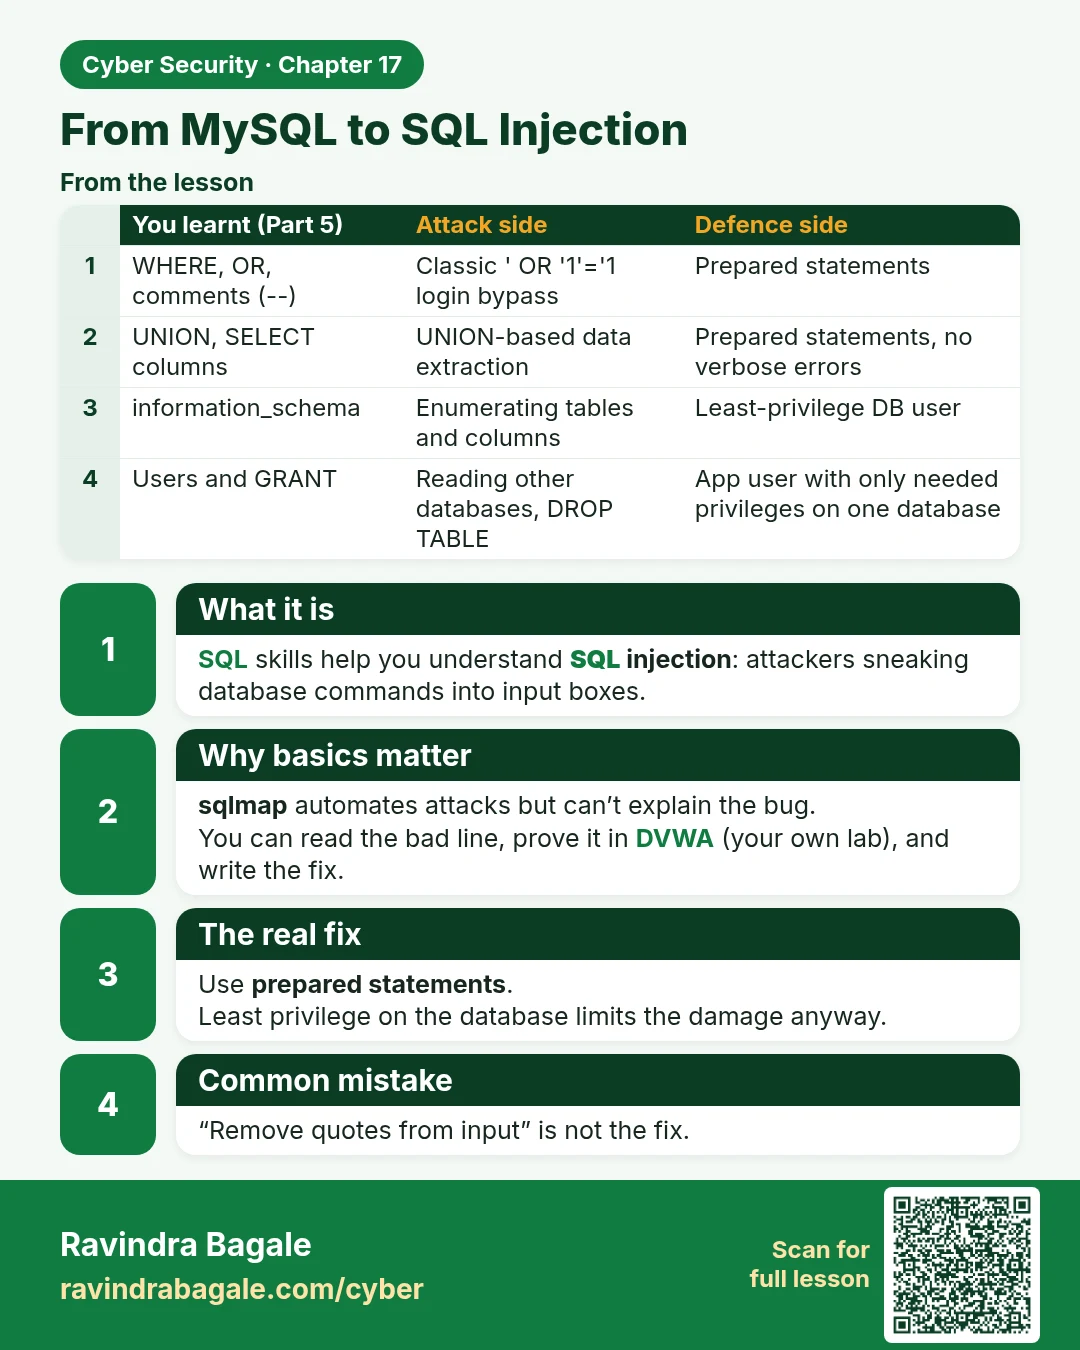
From MySQL to SQL Injection SQL skills help you understand SQL injection : attackers sneaking database commands into input boxes. sqlmap automates attacks but can’t explain the bug. You can read the bad line, prove it in DVWA (your own lab), and write the fix. Use prepared statements . Least privile
Read card text
What this card says
What it is
SQL skills help you understand SQL injection: attackers sneaking database commands into input boxes.
Why basics matter
sqlmap automates attacks but can’t explain the bug.
You can read the bad line, prove it in DVWA (your own lab), and write the fix.
The real fix
Use prepared statements.
Least privilege on the database limits the damage anyway.
Common mistake
“Remove quotes from input” is not the fix.
| You learnt (Part 5) | Attack side | Defence side |
|---|---|---|
| WHERE, OR, comments (--) | Classic ' OR '1'='1 login bypass | Prepared statements |
| UNION, SELECT columns | UNION-based data extraction | Prepared statements, no verbose errors |
| information_schema | Enumerating tables and columns | Least-privilege DB user |
| Users and GRANT | Reading other databases, DROP TABLE | App user with only needed privileges on one database |
| Safe update mode, backups | Destructive injected queries | Backups, monitoring, WAF as an extra layer |
Learn more in the lesson: 17.5 From MySQL to SQL Injection