Ravi Sir's Cyber Security Cards › Revision Cards
From Linux and SSH to Brute Force, Privilege Escalation and Hardening
From Linux and SSH to Brute Force, Privilege Escalation and Hardening Linux skills turn into attack and defence skills: brute force (password guessing), privilege escalation (normal user → root) and hardening . Tools like linPEAS only list possible weaknesses. You need to understand Linux permission
Read card text
What this card says
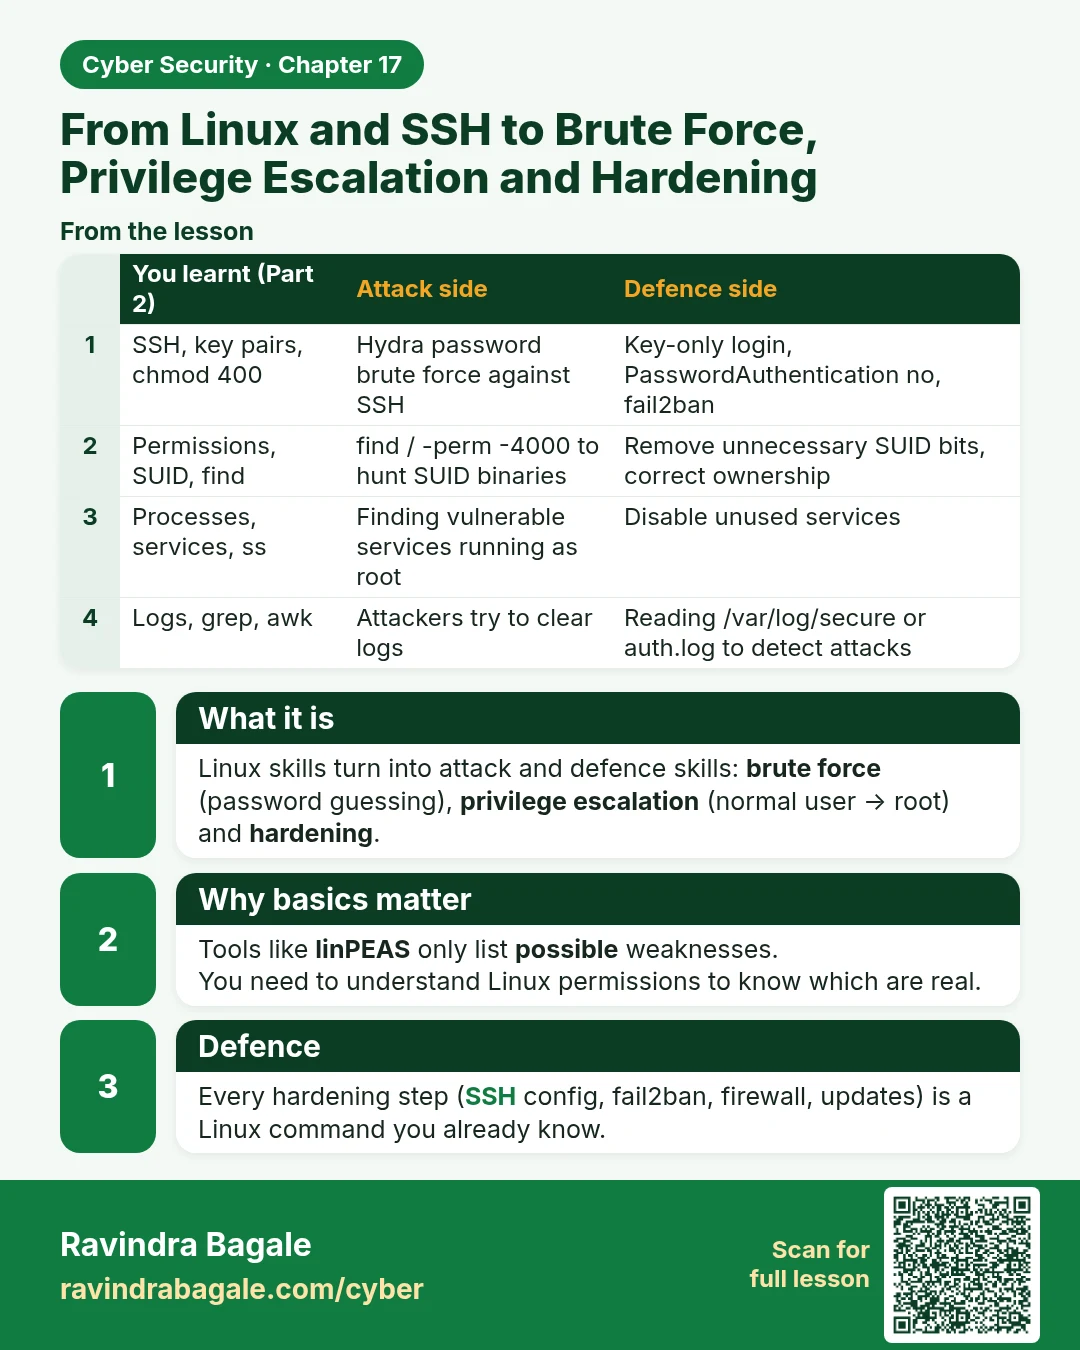
What it is
Linux skills turn into attack and defence skills: brute force (password guessing), privilege escalation (normal user → root) and hardening.
Why basics matter
Tools like linPEAS only list possible weaknesses.
You need to understand Linux permissions to know which are real.
Defence
Every hardening step (SSH config, fail2ban, firewall, updates) is a Linux command you already know.
| You learnt (Part 2) | Attack side | Defence side |
|---|---|---|
| SSH, key pairs, chmod 400 | Hydra password brute force against SSH | Key-only login, PasswordAuthentication no, fail2ban |
| Permissions, SUID, find | find / -perm -4000 to hunt SUID binaries | Remove unnecessary SUID bits, correct ownership |
| Processes, services, ss | Finding vulnerable services running as root | Disable unused services |
| Logs, grep, awk | Attackers try to clear logs | Reading /var/log/secure or auth.log to detect attacks |
| cron | Persistence through cron jobs | Auditing crontabs |
Learn more in the lesson: 17.3 From Linux and SSH to Brute Force, Privilege Escalation and Hardening