Ravi Sir's Cyber Security Cards › Revision Cards
From HTTP and Web Servers to Burp Suite, Nikto and Misconfigurations
From HTTP and Web Servers to Burp Suite, Nikto and Misconfigurations Web server skills turn into web testing skills. Burp Suite catches web requests. Nikto scans for weak settings. curl -I https://yoursite already shows if versions leak and if security headers exist. No special tool needed. You set
Read card text
What this card says
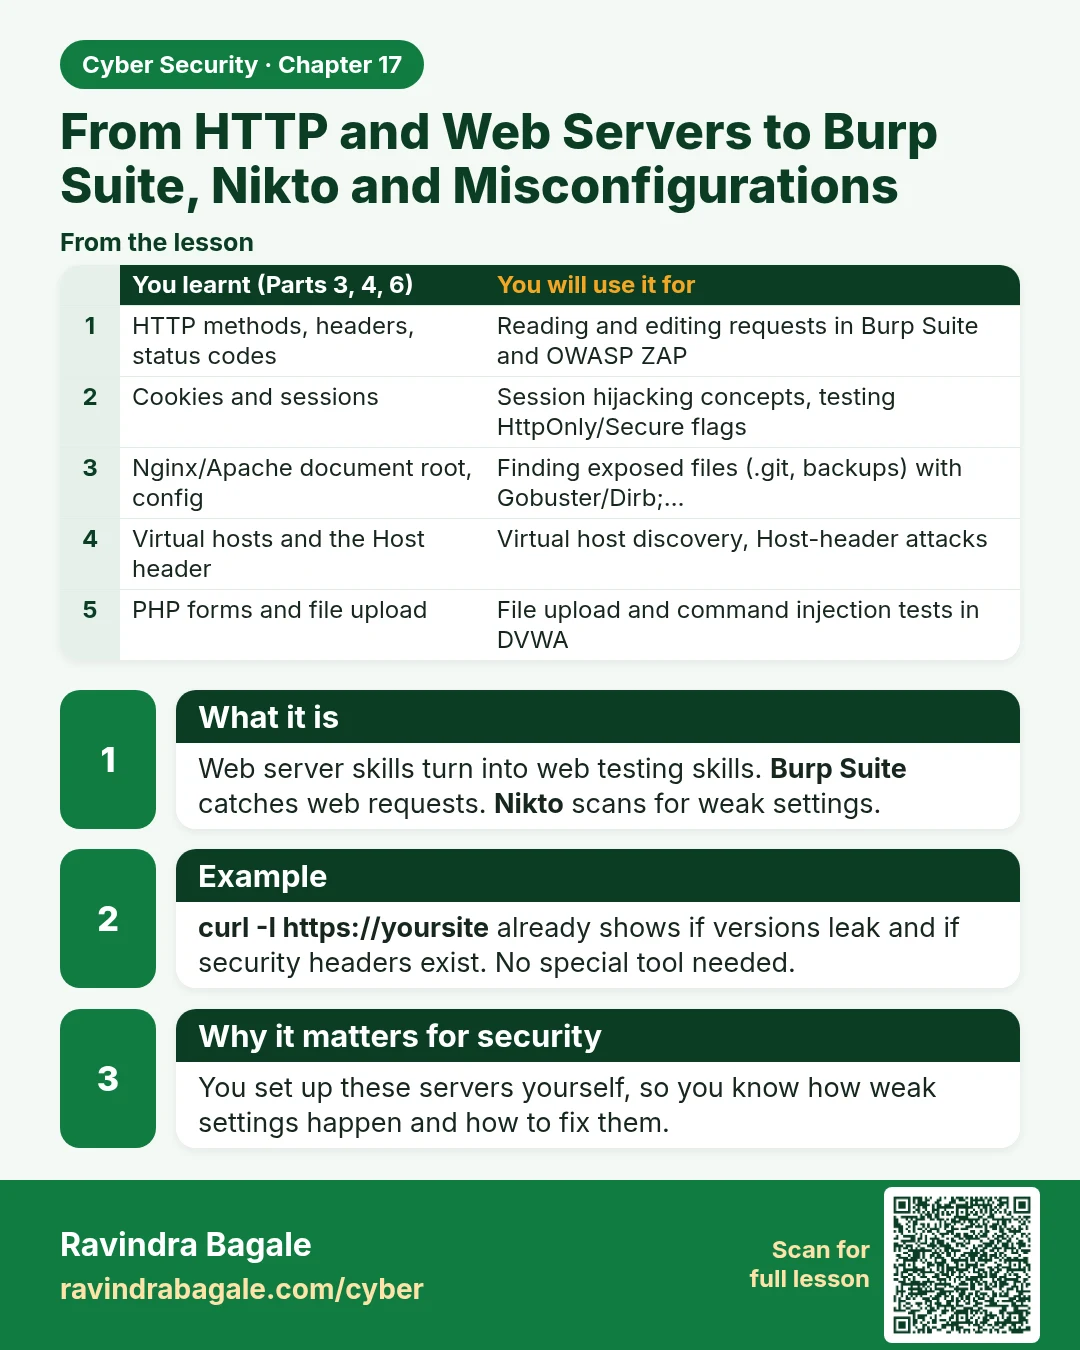
What it is
Web server skills turn into web testing skills. Burp Suite catches web requests. Nikto scans for weak settings.
Example
curl -I https://yoursite already shows if versions leak and if security headers exist. No special tool needed.
Why it matters for security
You set up these servers yourself, so you know how weak settings happen and how to fix them.
| You learnt (Parts 3, 4, 6) | You will use it for |
|---|---|
| HTTP methods, headers, status codes | Reading and editing requests in Burp Suite and OWASP ZAP |
| Cookies and sessions | Session hijacking concepts, testing HttpOnly/Secure flags |
| Nginx/Apache document root, config | Finding exposed files (.git, backups) with Gobuster/Dirb;… |
| Virtual hosts and the Host header | Virtual host discovery, Host-header attacks |
| PHP forms and file upload | File upload and command injection tests in DVWA |
Learn more in the lesson: 17.4 From HTTP and Web Servers to Burp Suite, Nikto and Misconfigurations