Ravi Sir's Cyber Security Cards › Revision Cards
Encryption, Logging, IAM Roles and the S3 Security Checklist
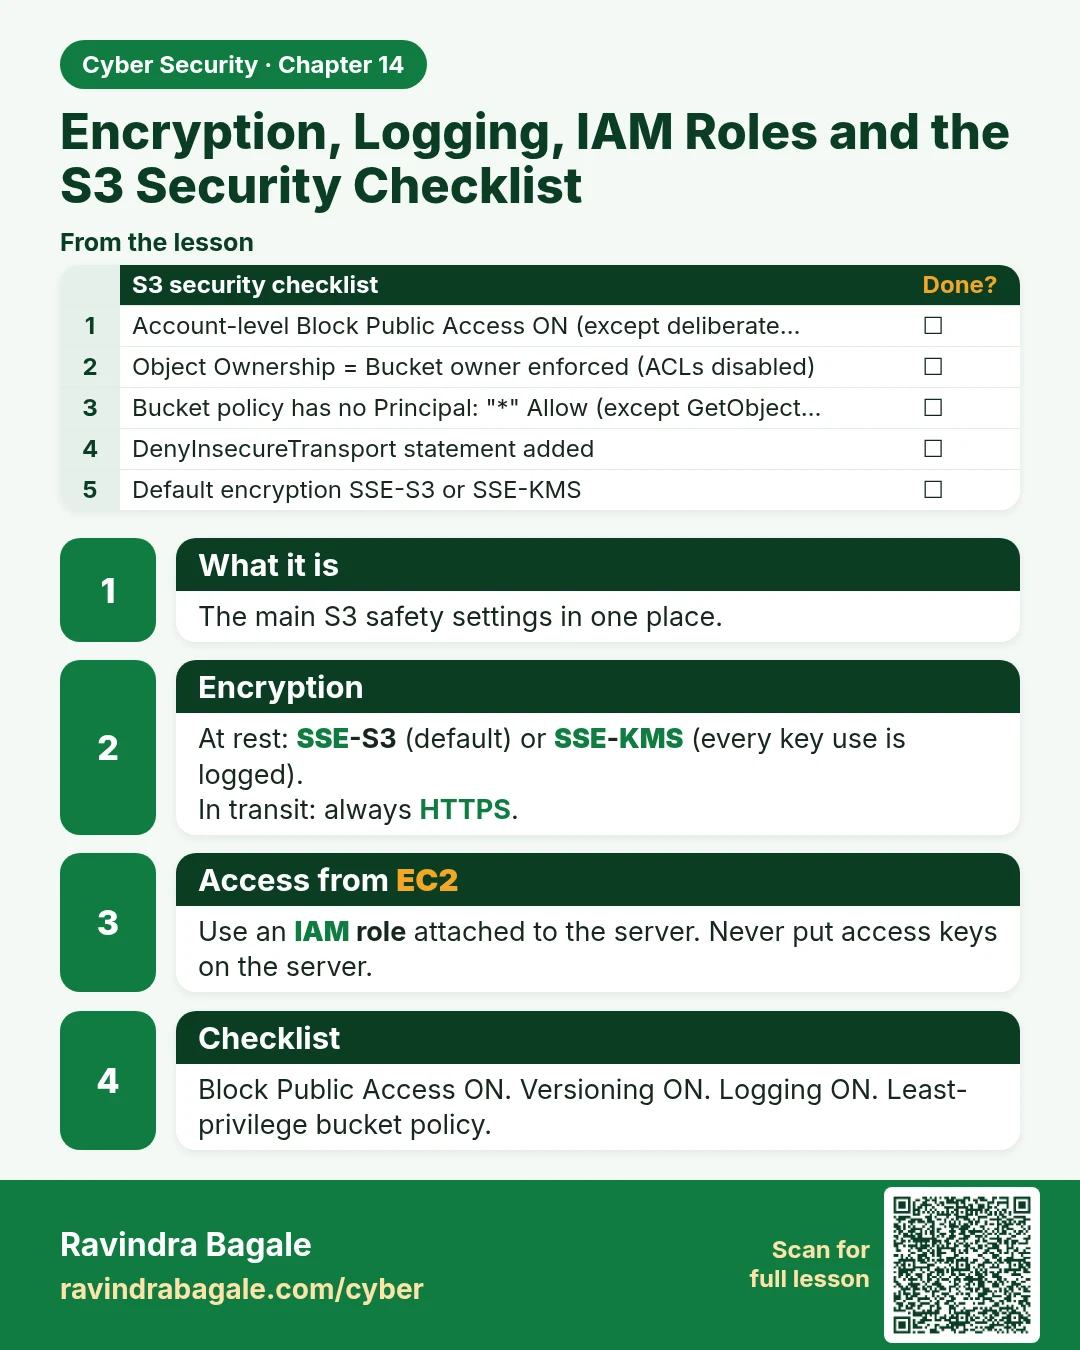
Encryption, Logging, IAM Roles and the S3 Security Checklist The main S3 safety settings in one place. At rest: SSE-S3 (default) or SSE-KMS (every key use is logged). In transit: always HTTPS. Use an IAM role attached to the server. Never put access keys on the server. Block Public Access ON. Versio
Read card text
What this card says
What it is
The main S3 safety settings in one place.
Encryption
At rest: SSE-S3 (default) or SSE-KMS (every key use is logged).
In transit: always HTTPS.
Access from EC2
Use an IAM role attached to the server. Never put access keys on the server.
Checklist
Block Public Access ON. Versioning ON. Logging ON. Least-privilege bucket policy.
| S3 security checklist | Done? |
|---|---|
| Account-level Block Public Access ON (except deliberate… | ☐ |
| Object Ownership = Bucket owner enforced (ACLs disabled) | ☐ |
| Bucket policy has no Principal: "*" Allow (except GetObject… | ☐ |
| DenyInsecureTransport statement added | ☐ |
| Default encryption SSE-S3 or SSE-KMS | ☐ |
Learn more in the lesson: 14.7 Encryption, Logging, IAM Roles and the S3 Security Checklist