Ravi Sir's Cyber Security Cards › Revision Cards
EC2 Metadata, SSRF and a Leaked-Key Incident Checklist
EC2 Metadata, SSRF and a Leaked-Key Incident Checklist The EC2 metadata service at 169.254.169.254 gives an instance its role’s temporary keys. SSRF can abuse it. A buggy app is tricked into fetching the metadata URL, so the attacker gets the role’s keys. Set IMDSv2 required on every instance. If ke
Read card text
What this card says
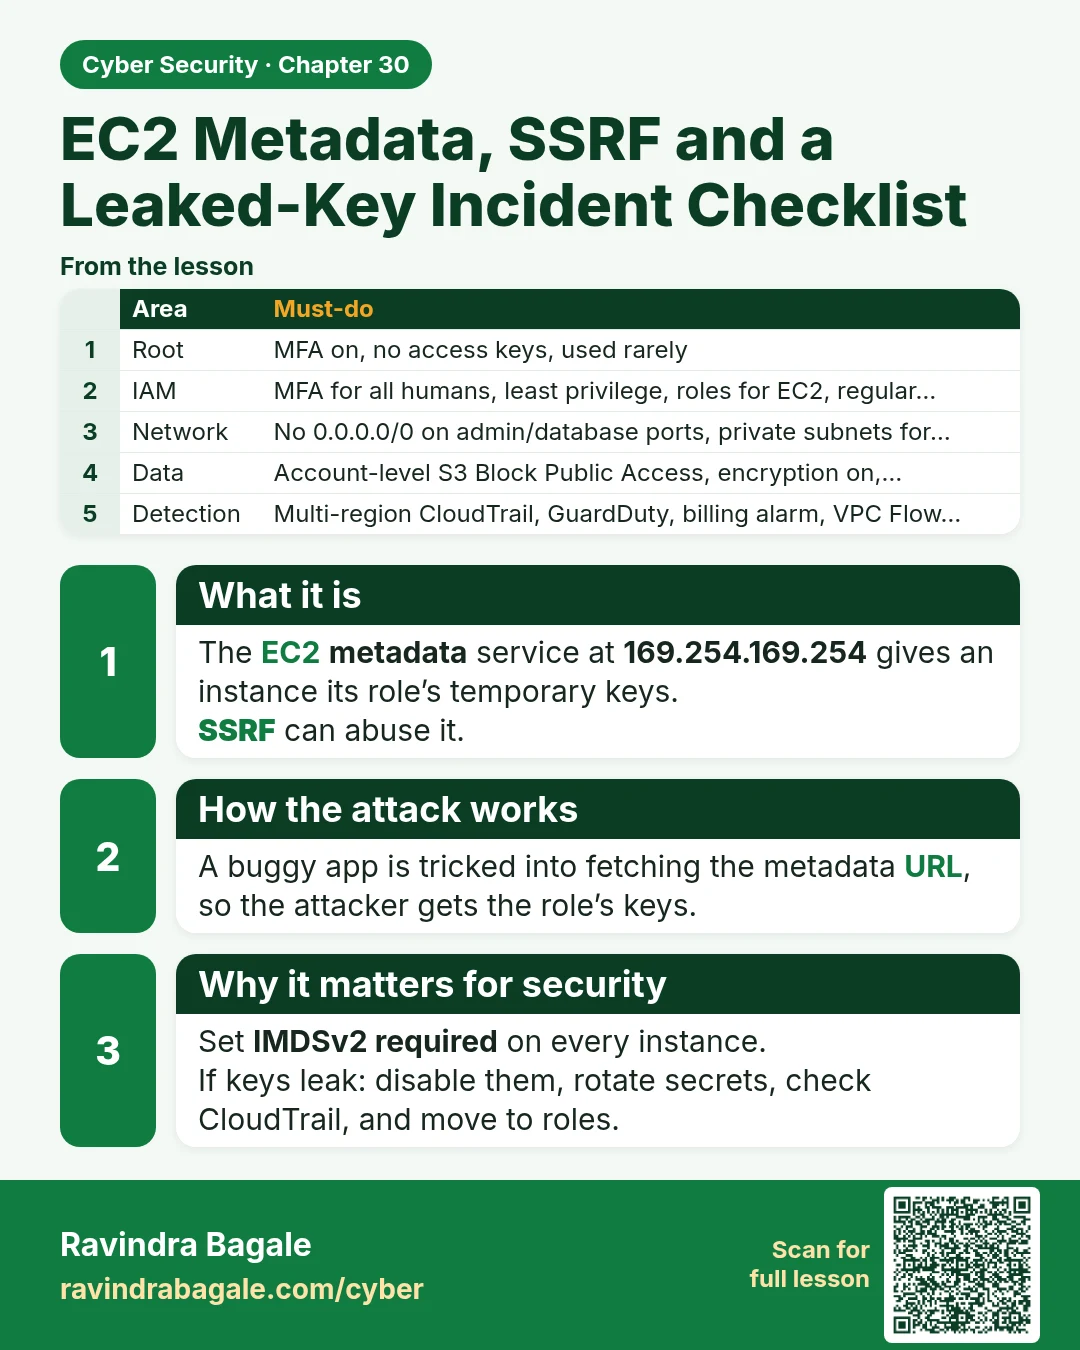
What it is
The EC2 metadata service at 169.254.169.254 gives an instance its role’s temporary keys.
SSRF can abuse it.
How the attack works
A buggy app is tricked into fetching the metadata URL, so the attacker gets the role’s keys.
Why it matters for security
Set IMDSv2 required on every instance.
If keys leak: disable them, rotate secrets, check CloudTrail, and move to roles.
| Area | Must-do |
|---|---|
| Root | MFA on, no access keys, used rarely |
| IAM | MFA for all humans, least privilege, roles for EC2, regular… |
| Network | No 0.0.0.0/0 on admin/database ports, private subnets for… |
| Data | Account-level S3 Block Public Access, encryption on,… |
| Detection | Multi-region CloudTrail, GuardDuty, billing alarm, VPC Flow… |
Learn more in the lesson: 30.6 EC2 Metadata, SSRF and a Leaked-Key Incident Checklist