Ravi Sir's Cyber Security Cards › Revision Cards
Domains, S3, RDS and Project Checklist
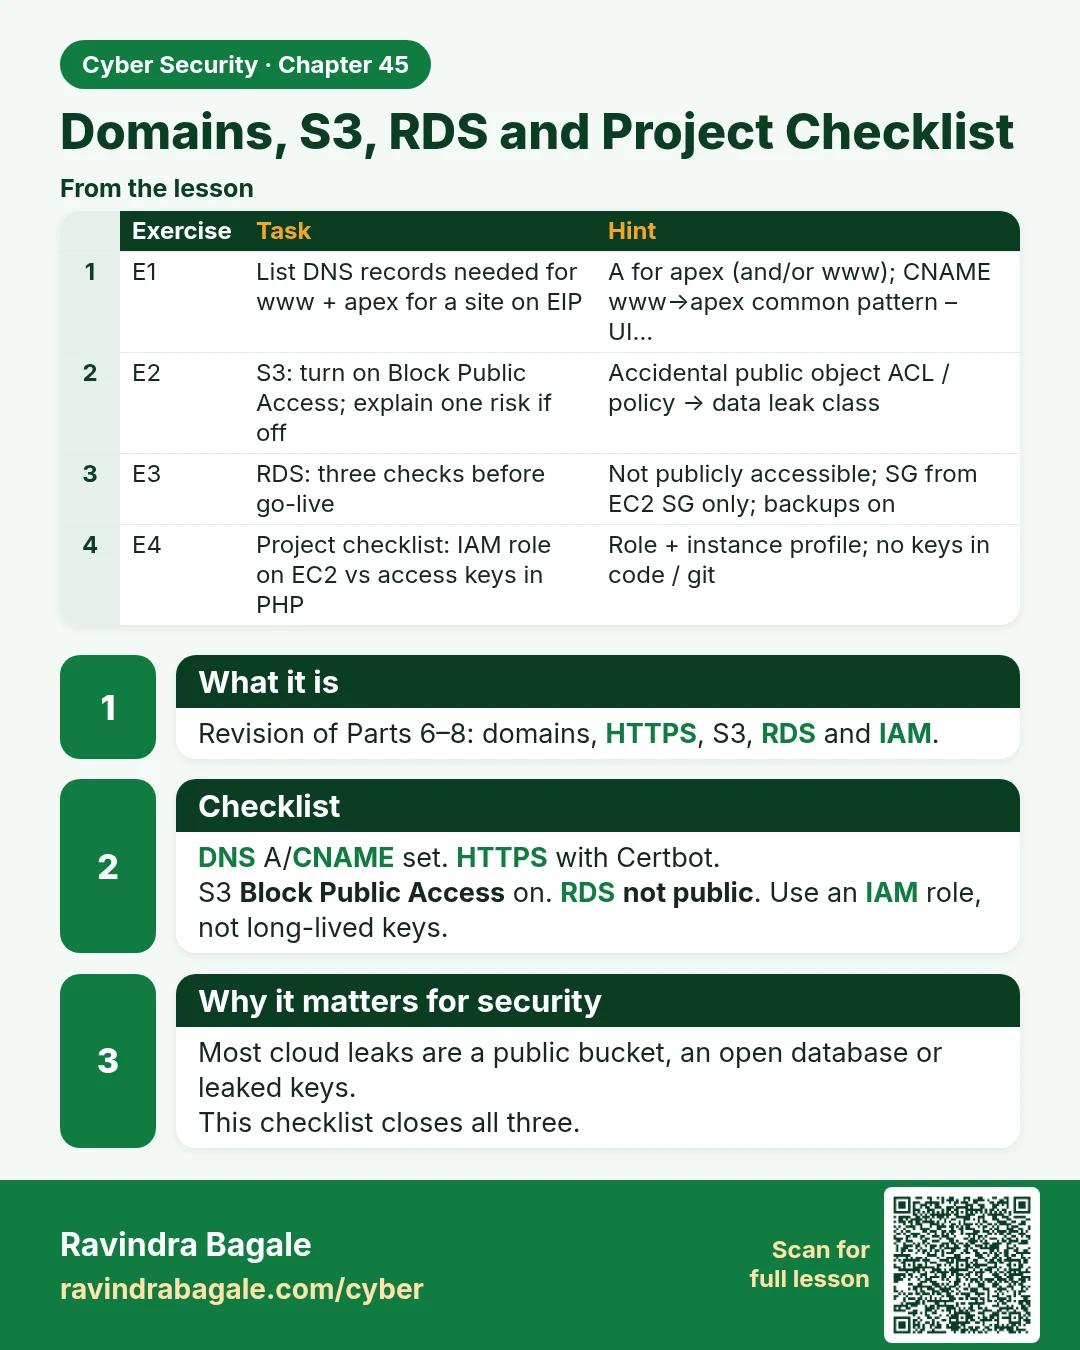
Domains, S3, RDS and Project Checklist Revision of Parts 6–8: domains, HTTPS, S3, RDS and IAM. DNS A/CNAME set. HTTPS with Certbot. S3 Block Public Access on. RDS not public . Use an IAM role, not long-lived keys. Most cloud leaks are a public bucket, an open database or leaked keys. This checklist
Read card text
What this card says
What it is
Revision of Parts 6–8: domains, HTTPS, S3, RDS and IAM.
Checklist
DNS A/CNAME set. HTTPS with Certbot.
S3 Block Public Access on. RDS not public. Use an IAM role, not long-lived keys.
Why it matters for security
Most cloud leaks are a public bucket, an open database or leaked keys.
This checklist closes all three.
| Exercise | Task | Hint |
|---|---|---|
| E1 | List DNS records needed for www + apex for a site on EIP | A for apex (and/or www); CNAME www→apex common pattern – UI… |
| E2 | S3: turn on Block Public Access; explain one risk if off | Accidental public object ACL / policy → data leak class |
| E3 | RDS: three checks before go-live | Not publicly accessible; SG from EC2 SG only; backups on |
| E4 | Project checklist: IAM role on EC2 vs access keys in PHP | Role + instance profile; no keys in code / git |
| E5 | Presigned URL idea in two lines (reels project) | Temporary access to private object; expiry matters |
Learn more in the lesson: 45.5 Domains, S3, RDS and Project Checklist