Ravi Sir's Cyber Security Cards › Revision Cards
Detection – Logs, Concurrent Sessions, SIEM Signals
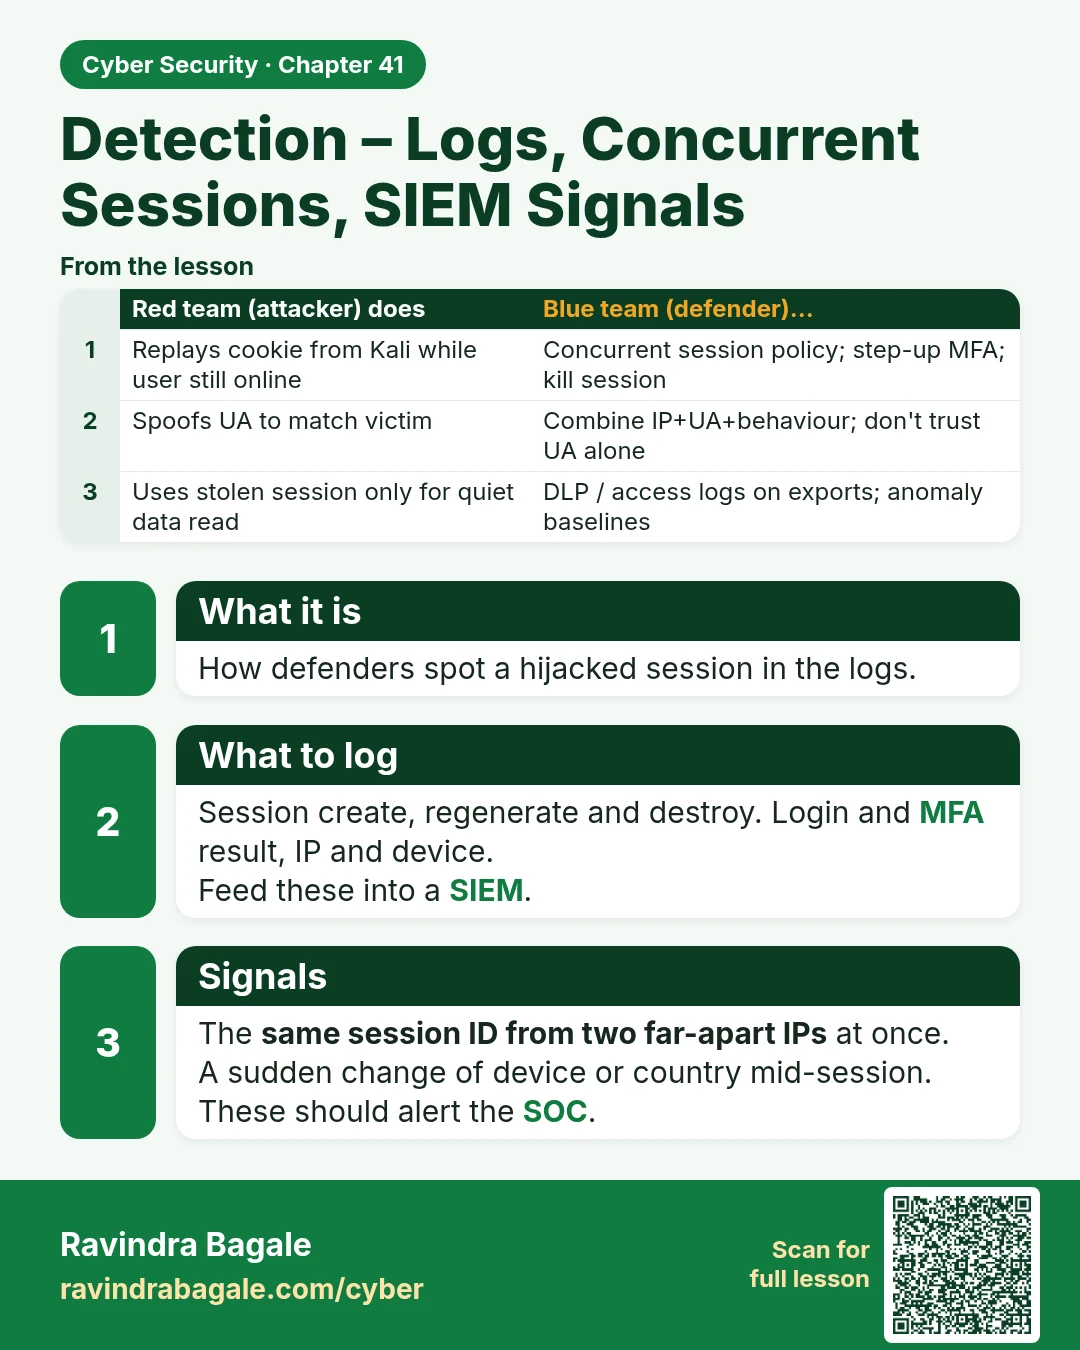
Detection – Logs, Concurrent Sessions, SIEM Signals How defenders spot a hijacked session in the logs. Session create, regenerate and destroy. Login and MFA result, IP and device. Feed these into a SIEM. The same session ID from two far-apart IPs at once. A sudden change of device or country mid-ses
Read card text
What this card says
What it is
How defenders spot a hijacked session in the logs.
What to log
Session create, regenerate and destroy. Login and MFA result, IP and device.
Feed these into a SIEM.
Signals
The same session ID from two far-apart IPs at once.
A sudden change of device or country mid-session. These should alert the SOC.
| Red team (attacker) does | Blue team (defender)… |
|---|---|
| Replays cookie from Kali while user still online | Concurrent session policy; step-up MFA; kill session |
| Spoofs UA to match victim | Combine IP+UA+behaviour; don't trust UA alone |
| Uses stolen session only for quiet data read | DLP / access logs on exports; anomaly baselines |
Learn more in the lesson: 41.7 Detection – Logs, Concurrent Sessions, SIEM Signals