Ravi Sir's Cyber Security Cards › Revision Cards
Deployment: Nginx, PHP Settings and Going Live
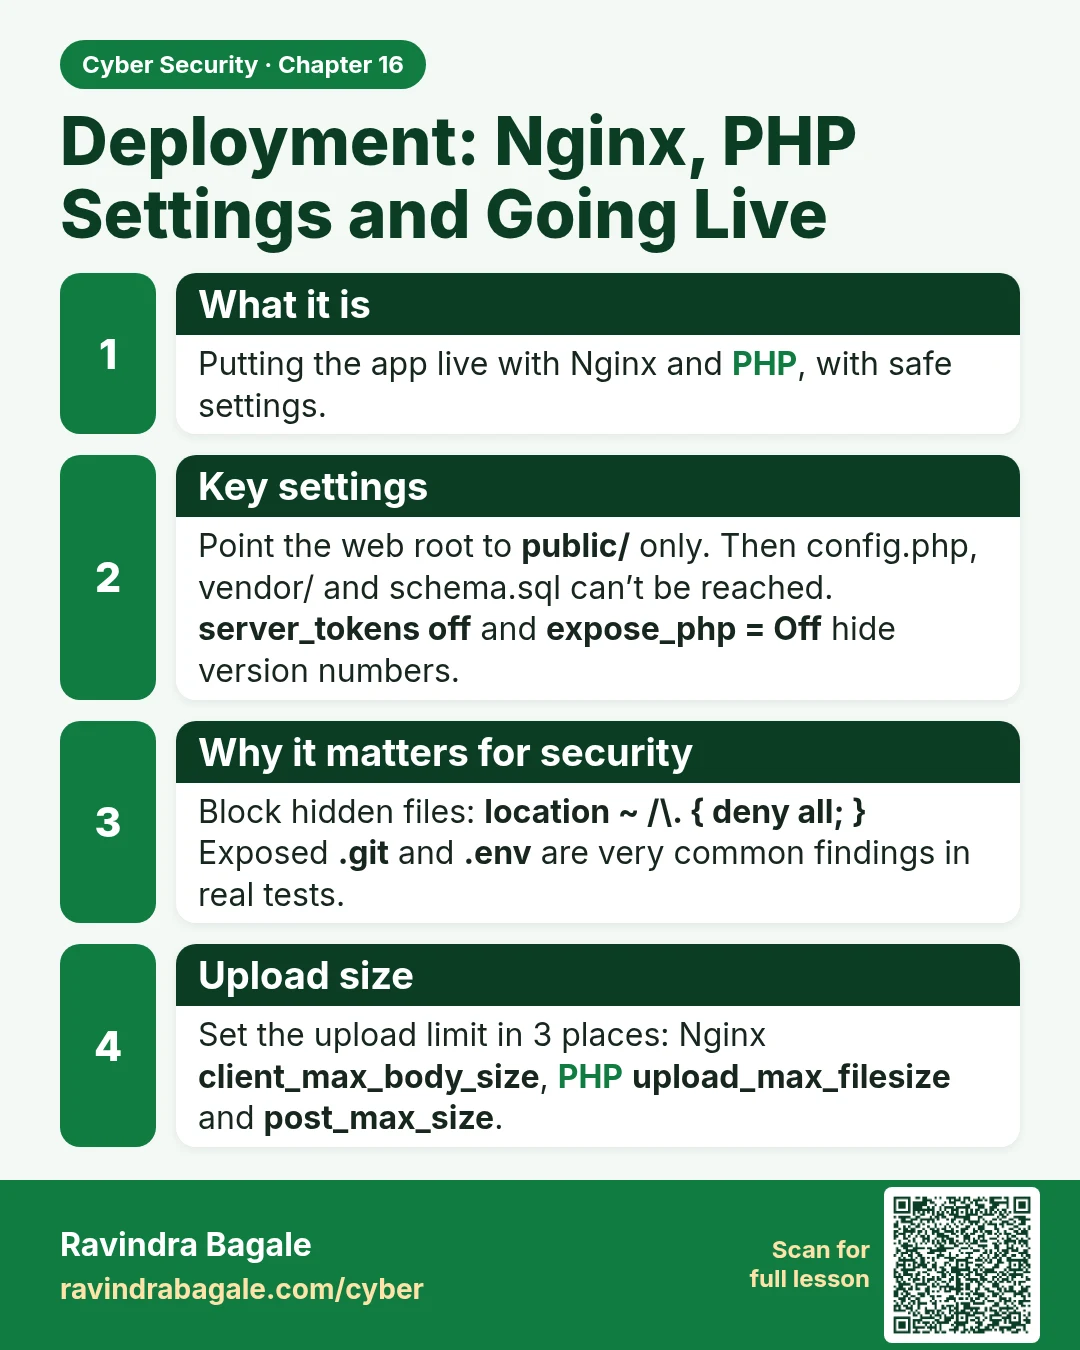
Deployment: Nginx, PHP Settings and Going Live Putting the app live with Nginx and PHP, with safe settings. Point the web root to public/ only. Then config.php, vendor/ and schema.sql can’t be reached. server_tokens off and expose_php = Off hide version numbers. Block hidden files: location ~ /\. {
Read card text
What this card says
What it is
Putting the app live with Nginx and PHP, with safe settings.
Key settings
Point the web root to public/ only. Then config.php, vendor/ and schema.sql can’t be reached.
server_tokens off and expose_php = Off hide version numbers.
Why it matters for security
Block hidden files: location ~ /\. { deny all; }
Exposed .git and .env are very common findings in real tests.
Upload size
Set the upload limit in 3 places: Nginx client_max_body_size, PHP upload_max_filesize and post_max_size.
Learn more in the lesson: 16.10 Deployment: Nginx, PHP Settings and Going Live