Ravi Sir's Cyber Security Cards › Revision Cards
Defending Against Privilege Escalation
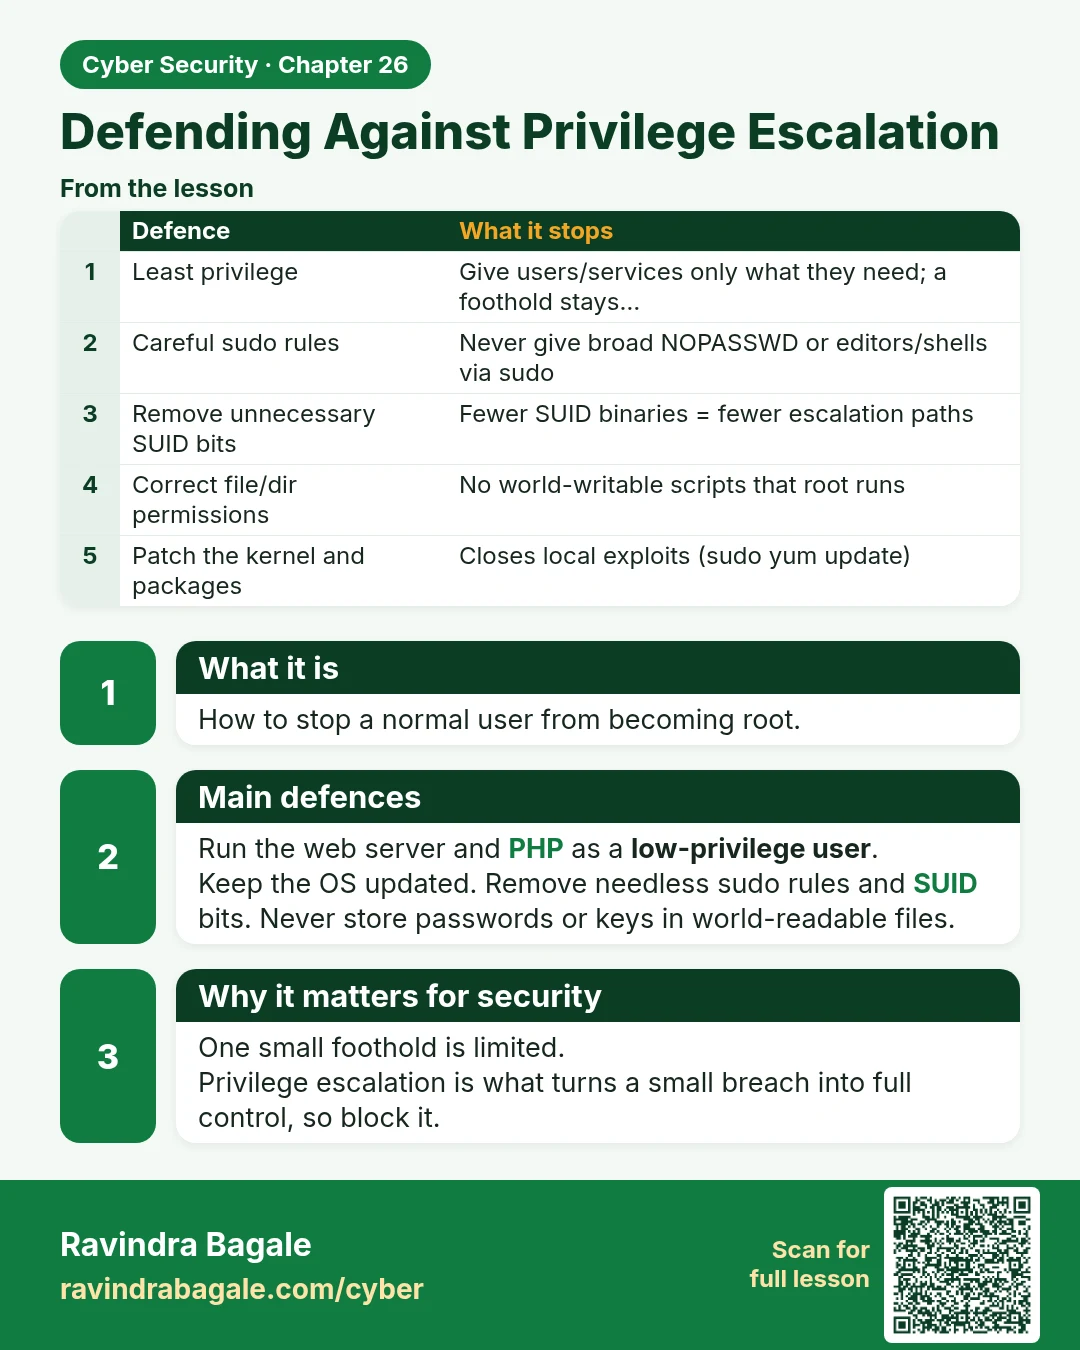
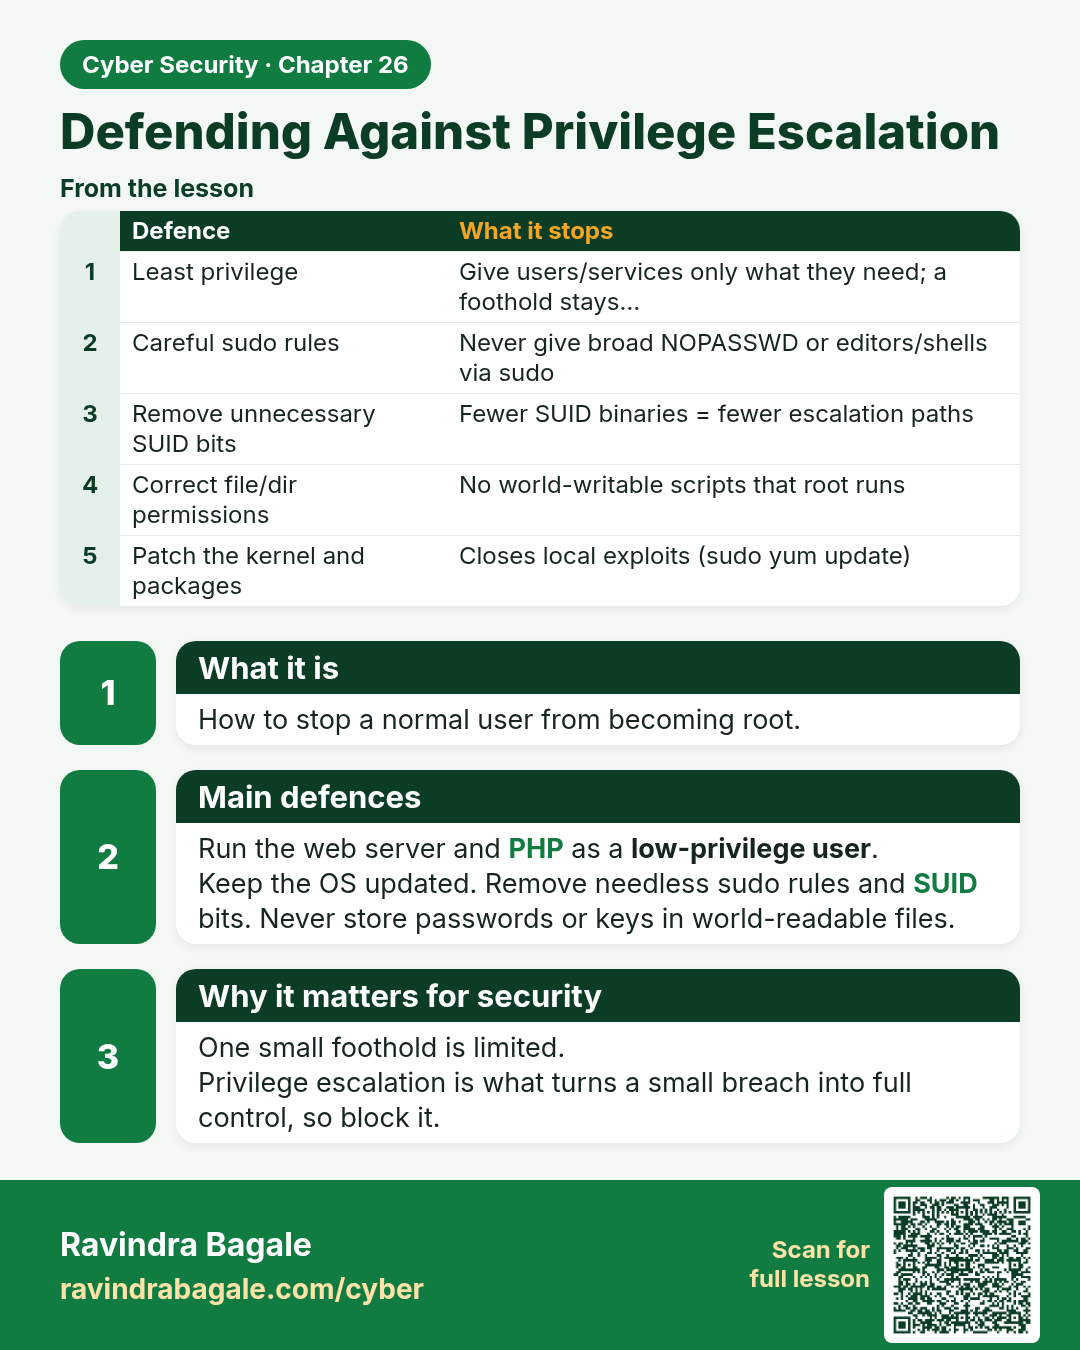
Defending Against Privilege Escalation How to stop a normal user from becoming root. Run the web server and PHP as a low-privilege user . Keep the OS updated. Remove needless sudo rules and SUID bits. Never store passwords or keys in world-readable files. One small foothold is limited. Privilege esc
Read card text
What this card says
What it is
How to stop a normal user from becoming root.
Main defences
Run the web server and PHP as a low-privilege user.
Keep the OS updated. Remove needless sudo rules and SUID bits. Never store passwords or keys in world-readable files.
Why it matters for security
One small foothold is limited.
Privilege escalation is what turns a small breach into full control, so block it.
| Defence | What it stops |
|---|---|
| Least privilege | Give users/services only what they need; a foothold stays… |
| Careful sudo rules | Never give broad NOPASSWD or editors/shells via sudo |
| Remove unnecessary SUID bits | Fewer SUID binaries = fewer escalation paths |
| Correct file/dir permissions | No world-writable scripts that root runs |
| Patch the kernel and packages | Closes local exploits (sudo yum update) |
Learn more in the lesson: 26.6 Defending Against Privilege Escalation