Ravi Sir's Cyber Security Cards › Revision Cards
Defence Hardening Checklist
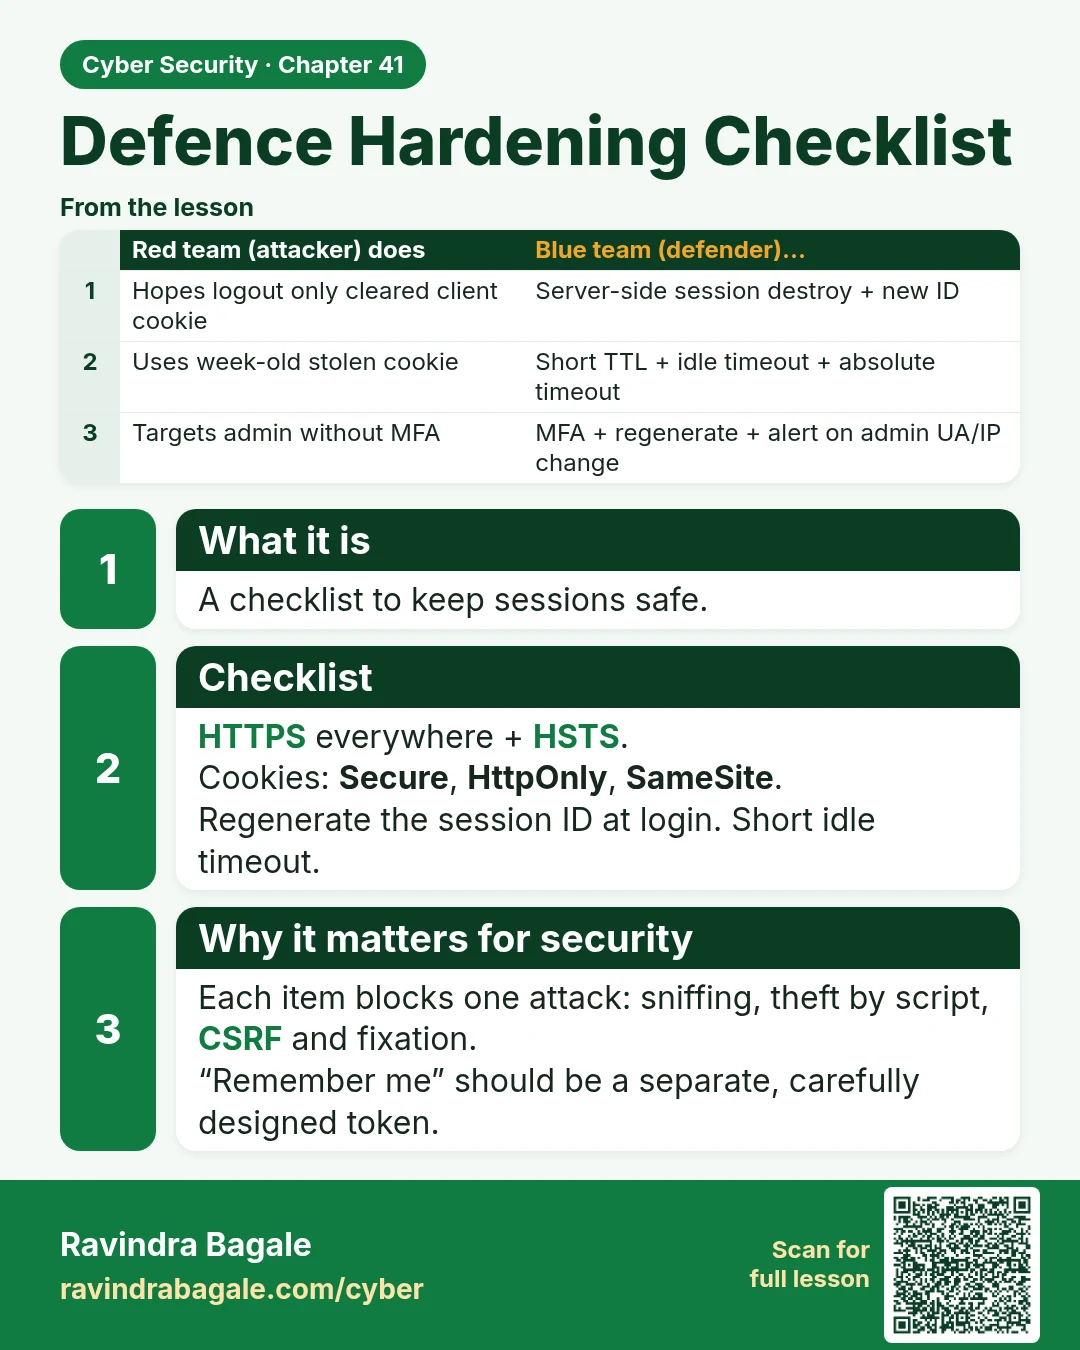
Defence Hardening Checklist A checklist to keep sessions safe. HTTPS everywhere + HSTS. Cookies: Secure , HttpOnly , SameSite . Regenerate the session ID at login. Short idle timeout. Each item blocks one attack: sniffing, theft by script, CSRF and fixation. “Remember me” should be a separate, caref
Read card text
What this card says
What it is
A checklist to keep sessions safe.
Checklist
HTTPS everywhere + HSTS.
Cookies: Secure, HttpOnly, SameSite.
Regenerate the session ID at login. Short idle timeout.
Why it matters for security
Each item blocks one attack: sniffing, theft by script, CSRF and fixation.
“Remember me” should be a separate, carefully designed token.
| Red team (attacker) does | Blue team (defender)… |
|---|---|
| Hopes logout only cleared client cookie | Server-side session destroy + new ID |
| Uses week-old stolen cookie | Short TTL + idle timeout + absolute timeout |
| Targets admin without MFA | MFA + regenerate + alert on admin UA/IP change |
Learn more in the lesson: 41.8 Defence Hardening Checklist