Ravi Sir's Cyber Security Cards › Revision Cards
Defence Checklist – Raja-Rani Traders Style AD
Defence Checklist – Raja-Rani Traders Style AD A hardening checklist for a small-company Active Directory. Example: 1 DC, 2 file servers, 25 PCs. Strong, unique admin passwords and LAPS . SMB signing on. Patch the DC. Few Domain Admins. Watch for Kerberoasting and odd logins. An attacker who gets on
Read card text
What this card says
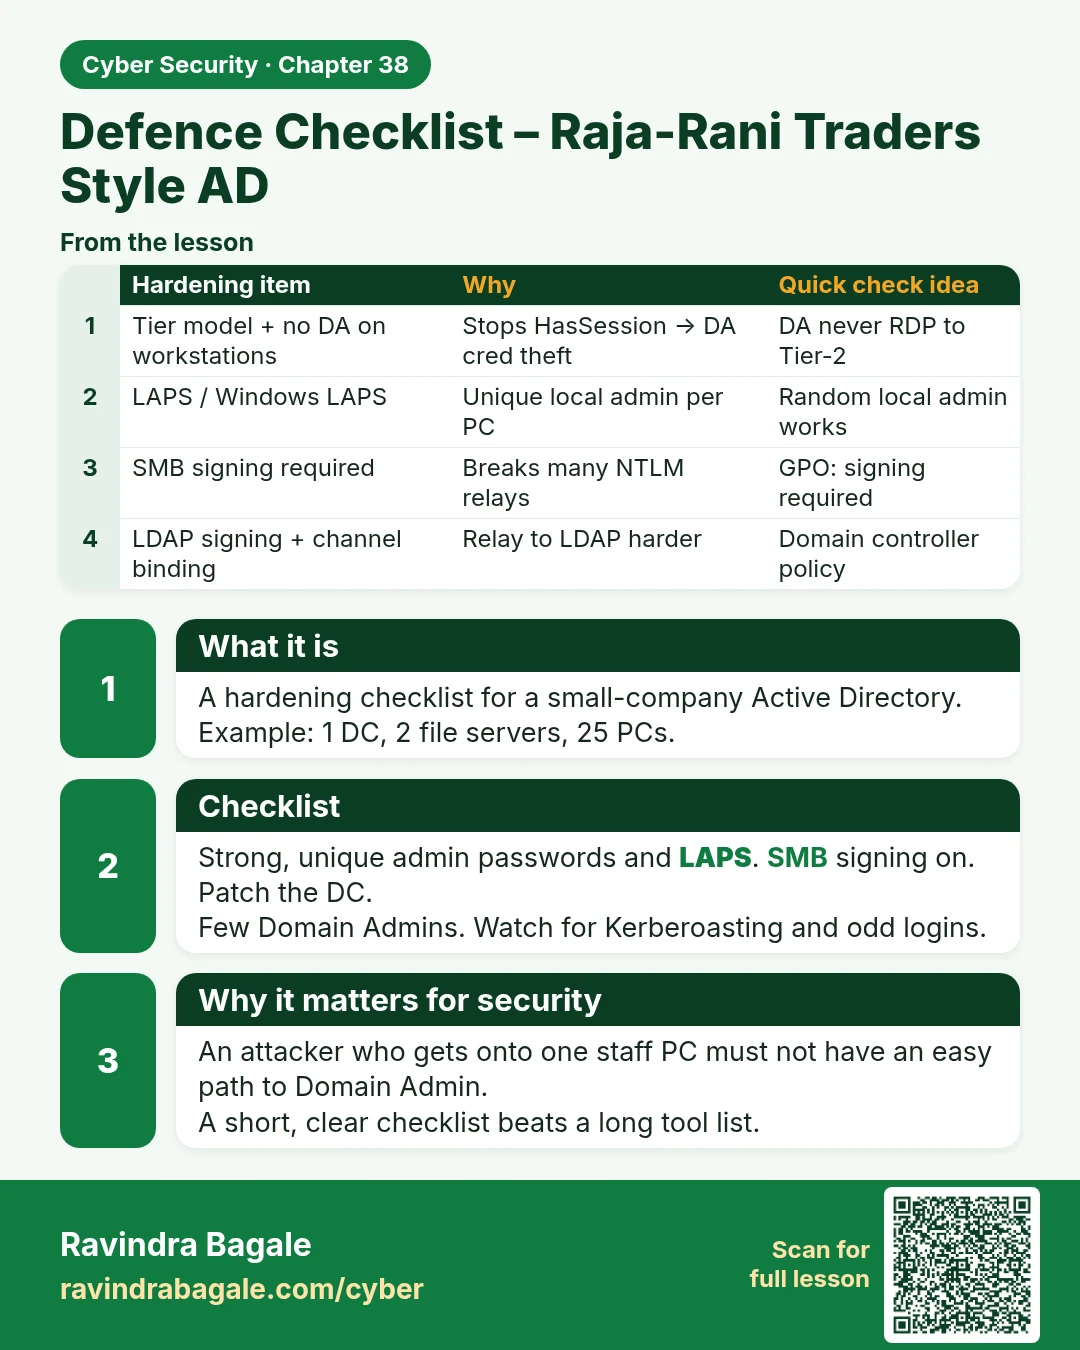
What it is
A hardening checklist for a small-company Active Directory.
Example: 1 DC, 2 file servers, 25 PCs.
Checklist
Strong, unique admin passwords and LAPS. SMB signing on. Patch the DC.
Few Domain Admins. Watch for Kerberoasting and odd logins.
Why it matters for security
An attacker who gets onto one staff PC must not have an easy path to Domain Admin.
A short, clear checklist beats a long tool list.
| Hardening item | Why | Quick check idea |
|---|---|---|
| Tier model + no DA on workstations | Stops HasSession → DA cred theft | DA never RDP to Tier-2 |
| LAPS / Windows LAPS | Unique local admin per PC | Random local admin works |
| SMB signing required | Breaks many NTLM relays | GPO: signing required |
| LDAP signing + channel binding | Relay to LDAP harder | Domain controller policy |
| Kerberos pre-auth on all users | Stops AS-REP roast | Find DONT_REQ_PREAUTH = 0 |
Learn more in the lesson: 38.8 Defence Checklist – Raja-Rani Traders Style AD