Ravi Sir's Cyber Security Cards › Revision Cards
Defence Checklist for These Tools
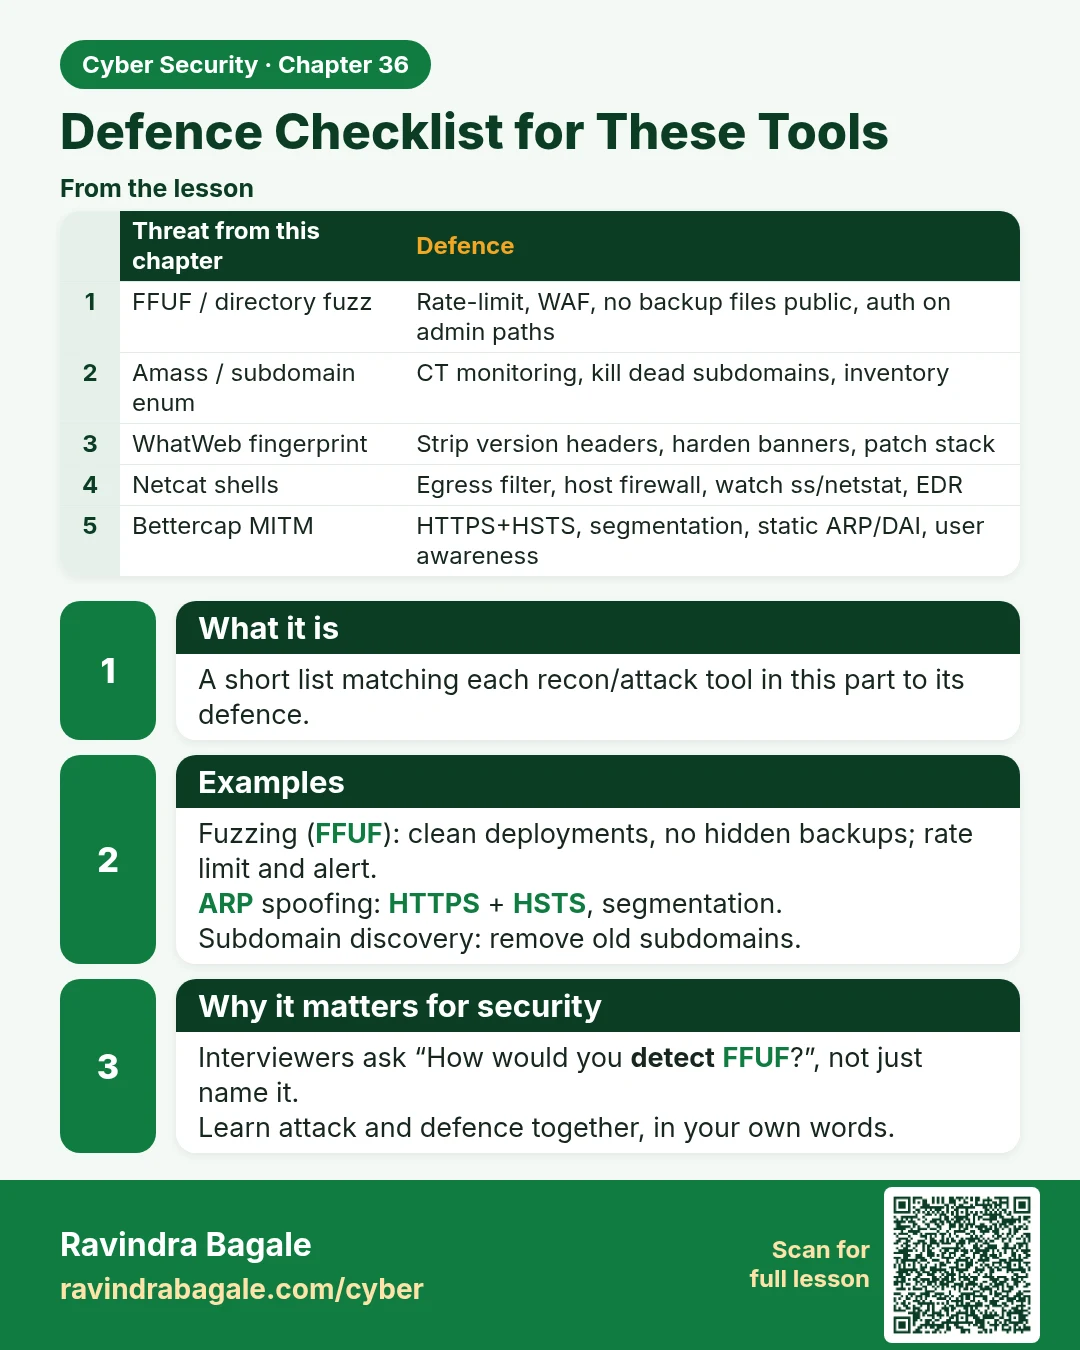
Defence Checklist for These Tools A short list matching each recon/attack tool in this part to its defence. Fuzzing (FFUF): clean deployments, no hidden backups; rate limit and alert. ARP spoofing: HTTPS + HSTS, segmentation. Subdomain discovery: remove old subdomains. Interviewers ask “How would yo
Read card text
What this card says
What it is
A short list matching each recon/attack tool in this part to its defence.
Examples
Fuzzing (FFUF): clean deployments, no hidden backups; rate limit and alert.
ARP spoofing: HTTPS + HSTS, segmentation.
Subdomain discovery: remove old subdomains.
Why it matters for security
Interviewers ask “How would you detect FFUF?”, not just name it.
Learn attack and defence together, in your own words.
| Threat from this chapter | Defence |
|---|---|
| FFUF / directory fuzz | Rate-limit, WAF, no backup files public, auth on admin paths |
| Amass / subdomain enum | CT monitoring, kill dead subdomains, inventory |
| WhatWeb fingerprint | Strip version headers, harden banners, patch stack |
| Netcat shells | Egress filter, host firewall, watch ss/netstat, EDR |
| Bettercap MITM | HTTPS+HSTS, segmentation, static ARP/DAI, user awareness |
Learn more in the lesson: 36.6 Defence Checklist for These Tools