Ravi Sir's Cyber Security Cards › Revision Cards
Cookie Theft and Insecure Transit
Cookie Theft and Insecure Transit Session cookies carry your login. If they travel without encryption, someone sniffing can copy them. You log in over HTTPS, then open an HTTP page on the same site. The cookie rides in clear text , so a sniffer copies it and logs in as you. In 2010, the Firesheep br
Read card text
What this card says
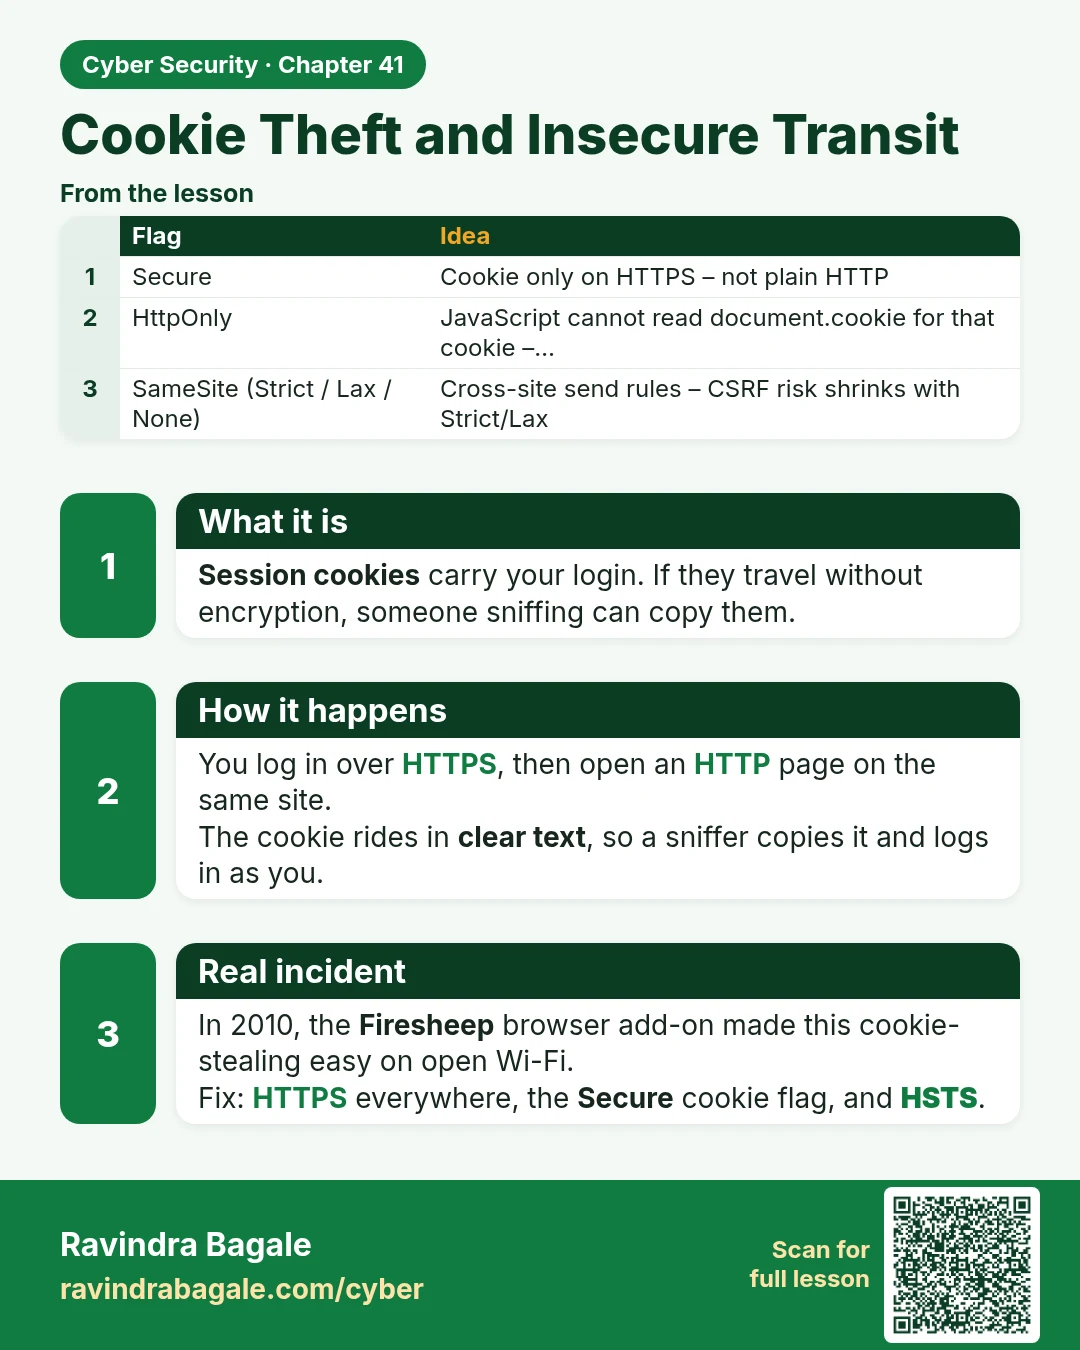
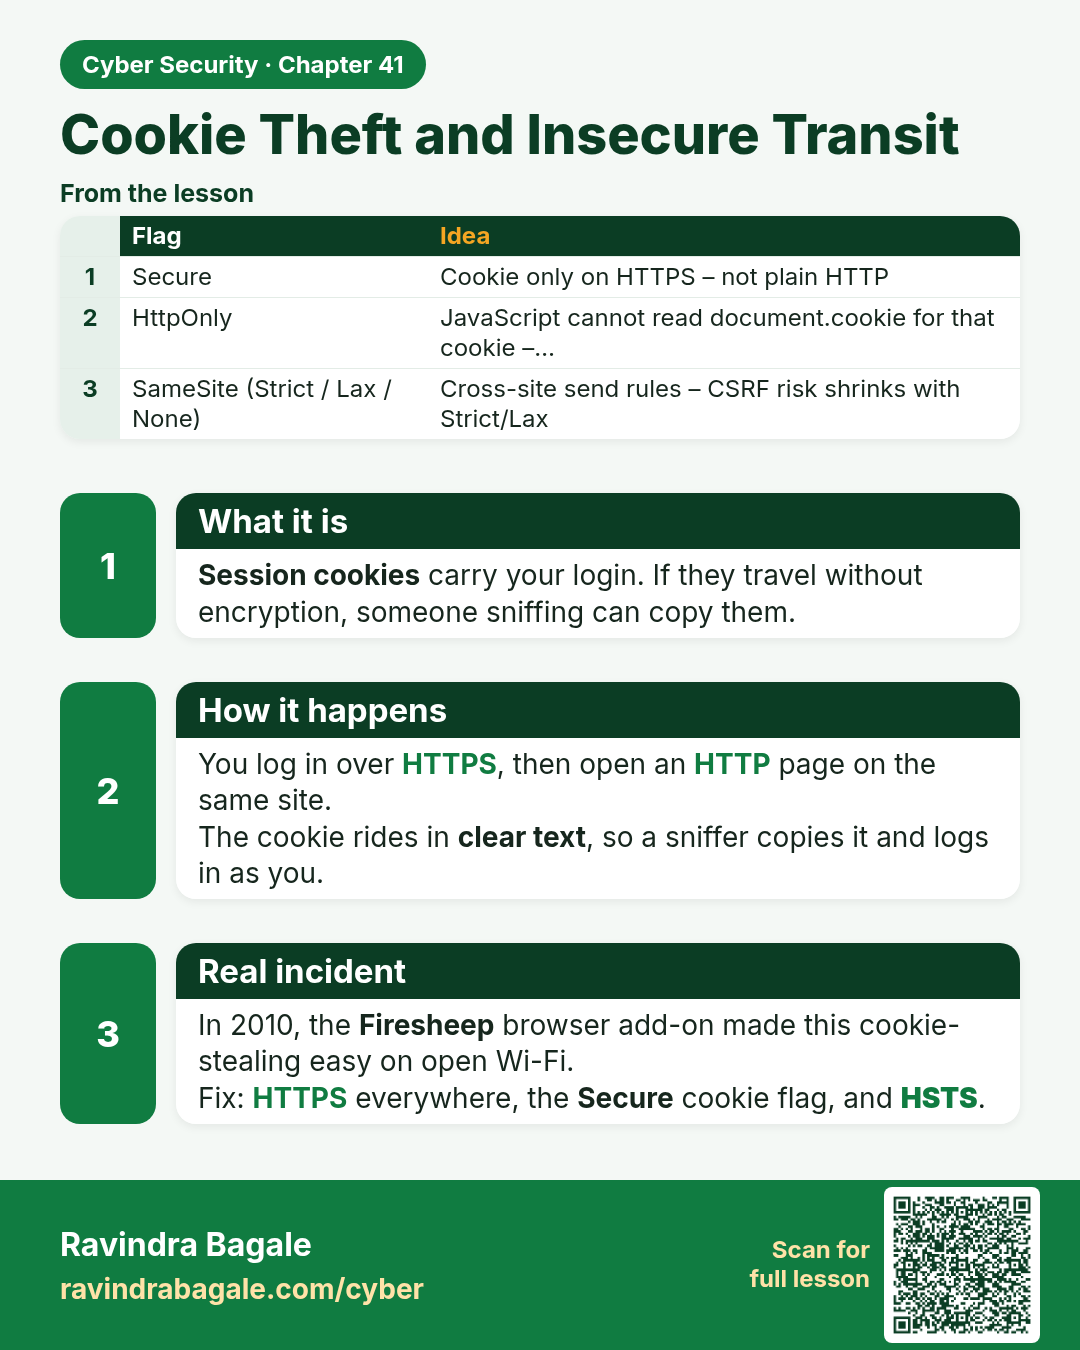
What it is
Session cookies carry your login. If they travel without encryption, someone sniffing can copy them.
How it happens
You log in over HTTPS, then open an HTTP page on the same site.
The cookie rides in clear text, so a sniffer copies it and logs in as you.
Real incident
In 2010, the Firesheep browser add-on made this cookie-stealing easy on open Wi-Fi.
Fix: HTTPS everywhere, the Secure cookie flag, and HSTS.
| Flag | Idea |
|---|---|
| Secure | Cookie only on HTTPS – not plain HTTP |
| HttpOnly | JavaScript cannot read document.cookie for that cookie –… |
| SameSite (Strict / Lax / None) | Cross-site send rules – CSRF risk shrinks with Strict/Lax |
Learn more in the lesson: 41.2 Cookie Theft and Insecure Transit