Ravi Sir's Cyber Security Cards › Revision Cards
Configuration and Shared Code
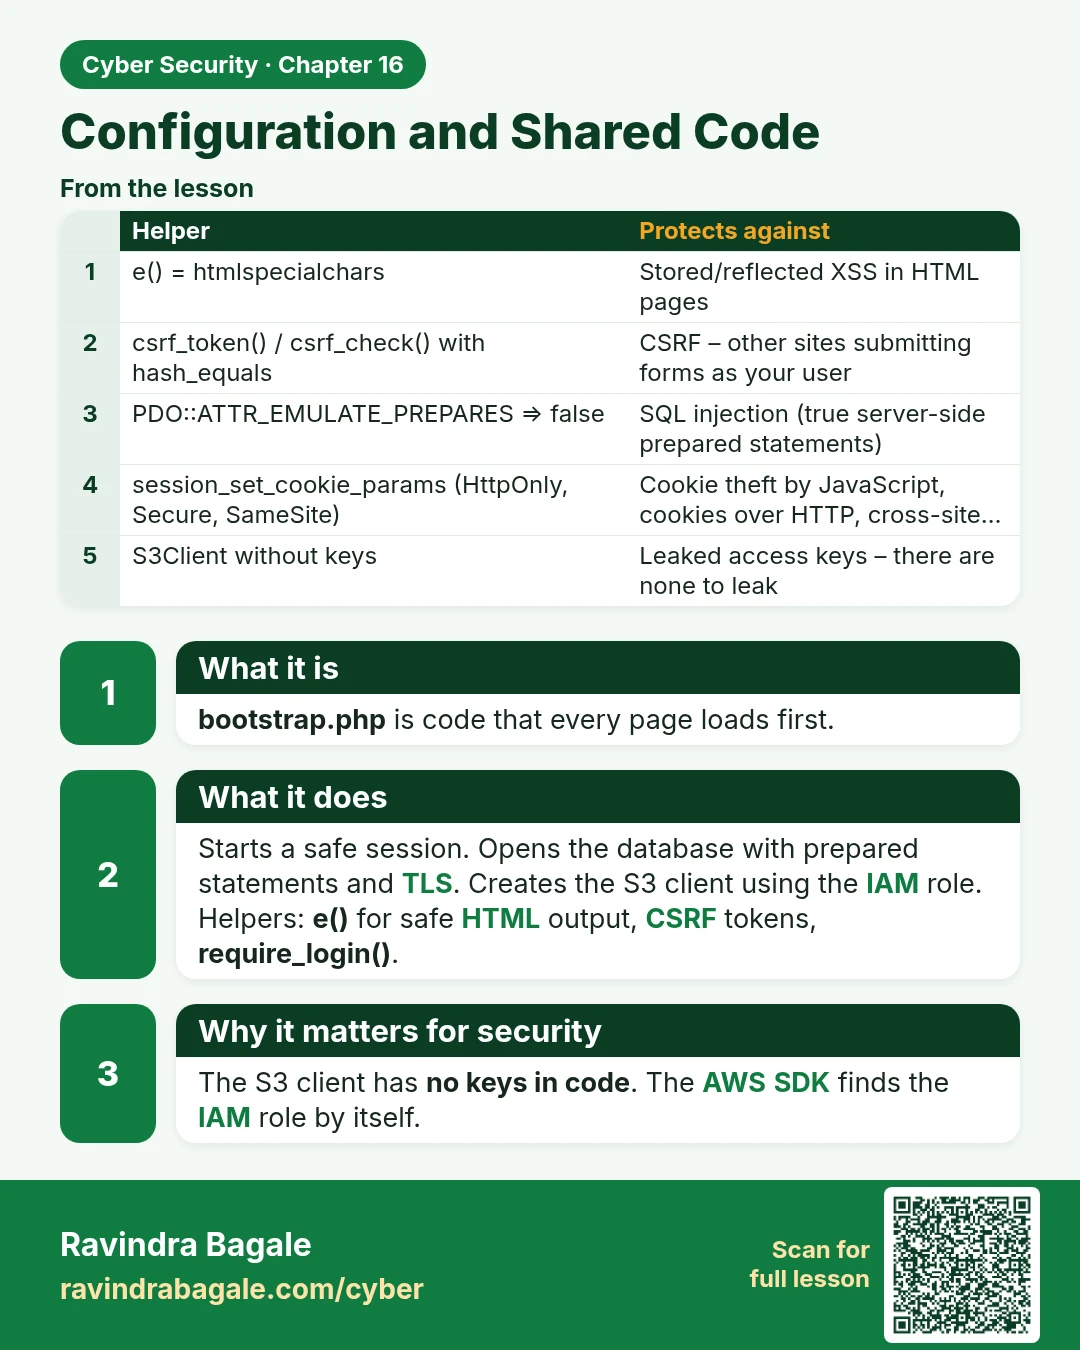
Configuration and Shared Code bootstrap.php is code that every page loads first. Starts a safe session. Opens the database with prepared statements and TLS. Creates the S3 client using the IAM role. Helpers: e() for safe HTML output, CSRF tokens, require_login() . The S3 client has no keys in code .
Read card text
What this card says
What it is
bootstrap.php is code that every page loads first.
What it does
Starts a safe session. Opens the database with prepared statements and TLS. Creates the S3 client using the IAM role.
Helpers: e() for safe HTML output, CSRF tokens, require_login().
Why it matters for security
The S3 client has no keys in code. The AWS SDK finds the IAM role by itself.
| Helper | Protects against |
|---|---|
| e() = htmlspecialchars | Stored/reflected XSS in HTML pages |
| csrf_token() / csrf_check() with hash_equals | CSRF – other sites submitting forms as your user |
| PDO::ATTR_EMULATE_PREPARES => false | SQL injection (true server-side prepared statements) |
| session_set_cookie_params (HttpOnly, Secure, SameSite) | Cookie theft by JavaScript, cookies over HTTP, cross-site… |
| S3Client without keys | Leaked access keys – there are none to leak |
Learn more in the lesson: 16.5 Configuration and Shared Code