Ravi Sir's Cyber Security Cards › Revision Cards
Common Crypto Mistakes and Attacks
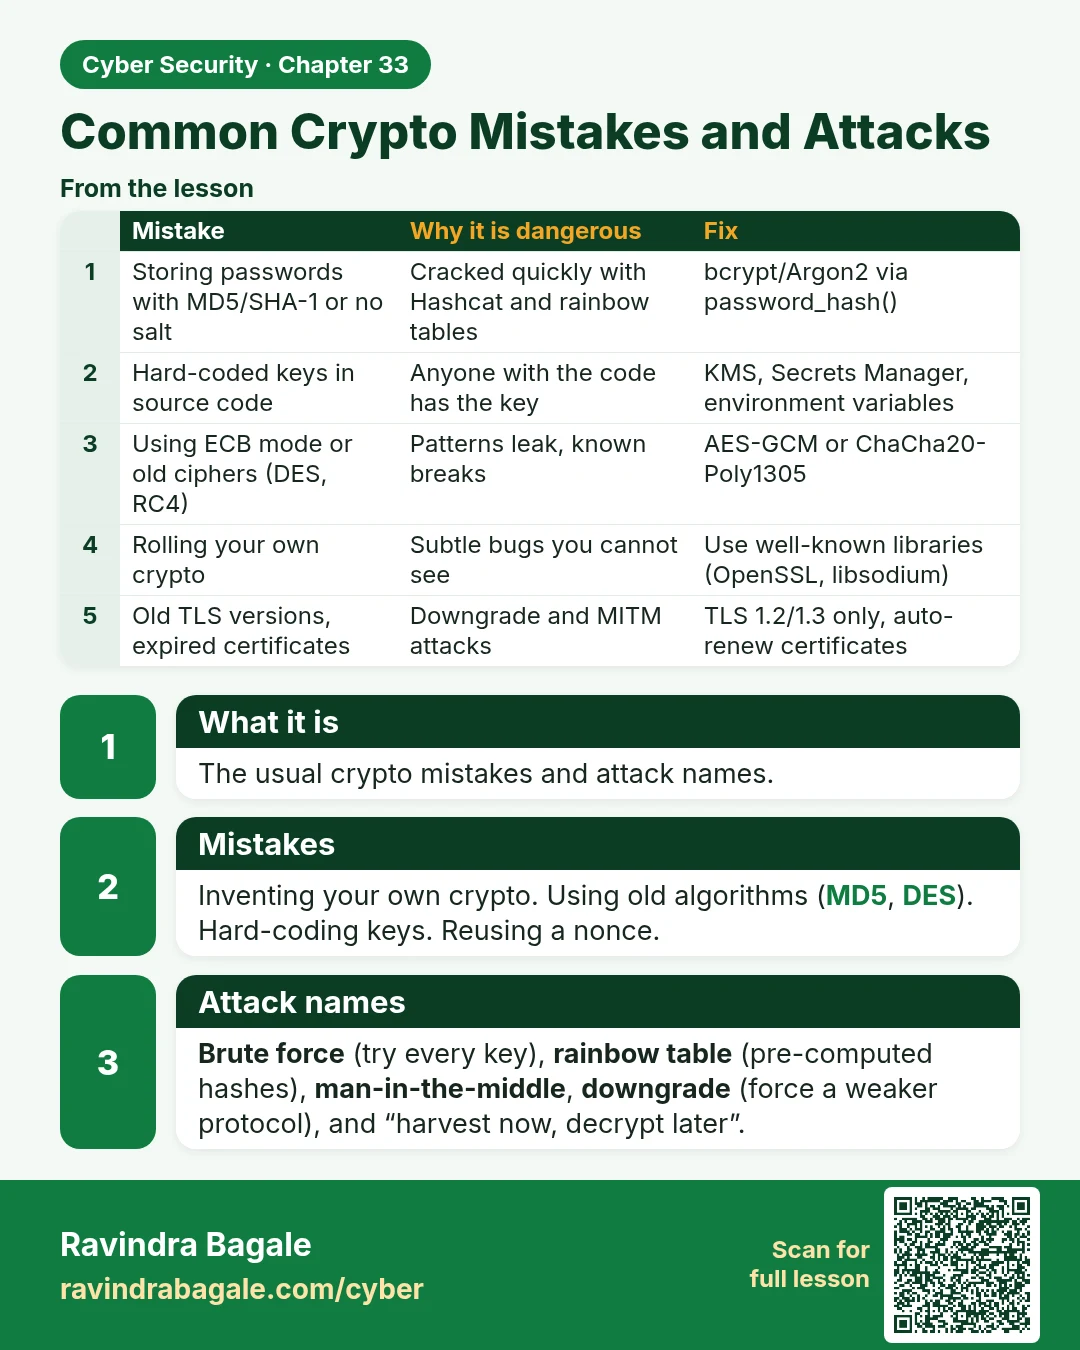
Common Crypto Mistakes and Attacks The usual crypto mistakes and attack names. Inventing your own crypto. Using old algorithms (MD5, DES). Hard-coding keys. Reusing a nonce. Brute force (try every key), rainbow table (pre-computed hashes), man-in-the-middle , downgrade (force a weaker protocol), and
Read card text
What this card says
What it is
The usual crypto mistakes and attack names.
Mistakes
Inventing your own crypto. Using old algorithms (MD5, DES). Hard-coding keys. Reusing a nonce.
Attack names
Brute force (try every key), rainbow table (pre-computed hashes), man-in-the-middle, downgrade (force a weaker protocol), and “harvest now, decrypt later”.
| Mistake | Why it is dangerous | Fix |
|---|---|---|
| Storing passwords with MD5/SHA-1 or no salt | Cracked quickly with Hashcat and rainbow tables | bcrypt/Argon2 via password_hash() |
| Hard-coded keys in source code | Anyone with the code has the key | KMS, Secrets Manager, environment variables |
| Using ECB mode or old ciphers (DES, RC4) | Patterns leak, known breaks | AES-GCM or ChaCha20-Poly1305 |
| Rolling your own crypto | Subtle bugs you cannot see | Use well-known libraries (OpenSSL, libsodium) |
| Old TLS versions, expired certificates | Downgrade and MITM attacks | TLS 1.2/1.3 only, auto-renew certificates |
Learn more in the lesson: 33.6 Common Crypto Mistakes and Attacks