Ravi Sir's Cyber Security Cards › Revision Cards
Cloud, SOC, Hardening and Crypto – Mixed Drill
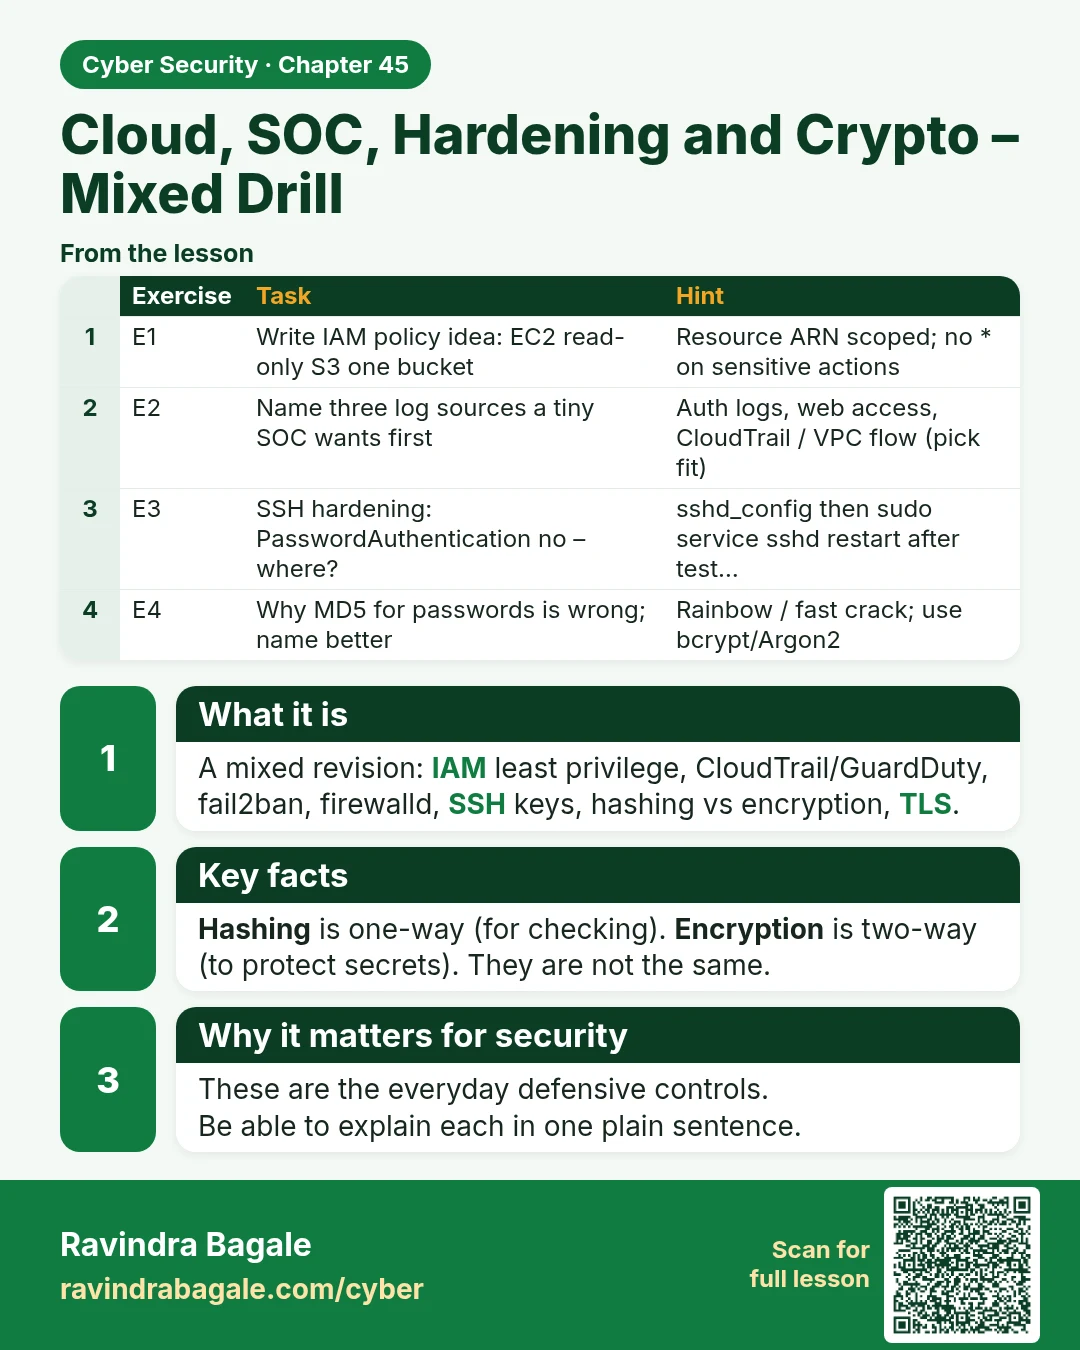
Cloud, SOC, Hardening and Crypto – Mixed Drill A mixed revision: IAM least privilege, CloudTrail/GuardDuty, fail2ban, firewalld, SSH keys, hashing vs encryption, TLS. Hashing is one-way (for checking). Encryption is two-way (to protect secrets). They are not the same. These are the everyday defensiv
Read card text
What this card says
What it is
A mixed revision: IAM least privilege, CloudTrail/GuardDuty, fail2ban, firewalld, SSH keys, hashing vs encryption, TLS.
Key facts
Hashing is one-way (for checking). Encryption is two-way (to protect secrets). They are not the same.
Why it matters for security
These are the everyday defensive controls.
Be able to explain each in one plain sentence.
| Exercise | Task | Hint |
|---|---|---|
| E1 | Write IAM policy idea: EC2 read-only S3 one bucket | Resource ARN scoped; no * on sensitive actions |
| E2 | Name three log sources a tiny SOC wants first | Auth logs, web access, CloudTrail / VPC flow (pick fit) |
| E3 | SSH hardening: PasswordAuthentication no – where? | sshd_config then sudo service sshd restart after test… |
| E4 | Why MD5 for passwords is wrong; name better | Rainbow / fast crack; use bcrypt/Argon2 |
| E5 | TLS: HTTP→HTTPS redirect checklist for Nginx | Listen 443 ssl; redirect 80; modern ciphers (defaults OK to… |
Learn more in the lesson: 45.8 Cloud, SOC, Hardening and Crypto – Mixed Drill