Ravi Sir's Cyber Security Cards › Revision Cards
CERT-In Directions for Organisations
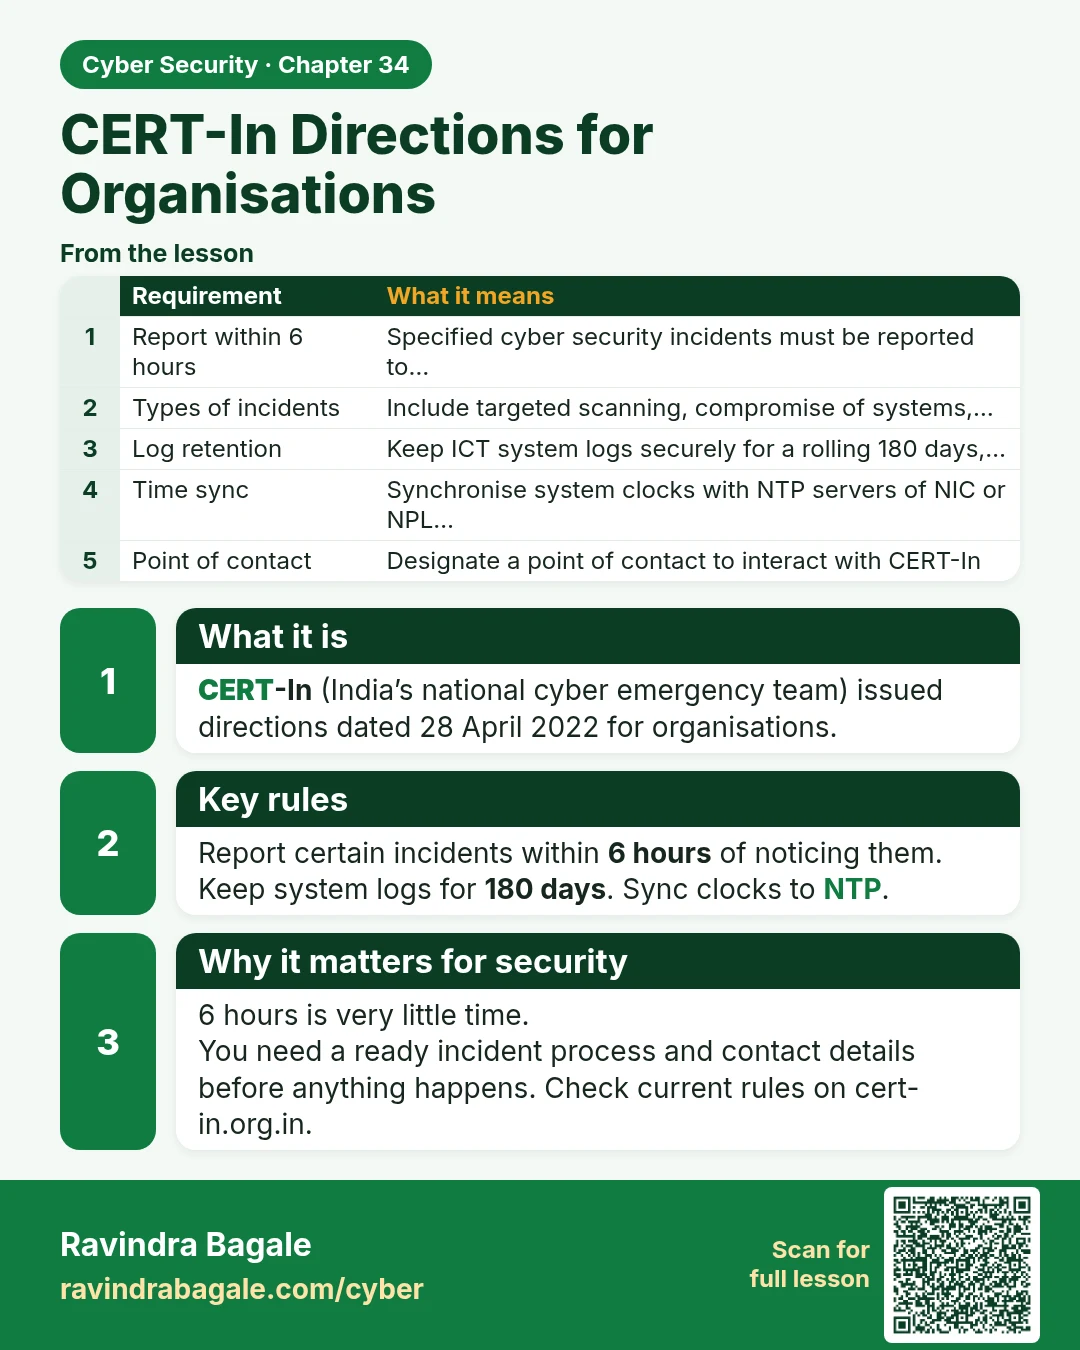
CERT-In Directions for Organisations CERT-In (India’s national cyber emergency team) issued directions dated 28 April 2022 for organisations. Report certain incidents within 6 hours of noticing them. Keep system logs for 180 days . Sync clocks to NTP. 6 hours is very little time. You need a ready in
Read card text
What this card says
What it is
CERT-In (India’s national cyber emergency team) issued directions dated 28 April 2022 for organisations.
Key rules
Report certain incidents within 6 hours of noticing them.
Keep system logs for 180 days. Sync clocks to NTP.
Why it matters for security
6 hours is very little time.
You need a ready incident process and contact details before anything happens. Check current rules on cert-in.org.in.
| Requirement | What it means |
|---|---|
| Report within 6 hours | Specified cyber security incidents must be reported to… |
| Types of incidents | Include targeted scanning, compromise of systems,… |
| Log retention | Keep ICT system logs securely for a rolling 180 days,… |
| Time sync | Synchronise system clocks with NTP servers of NIC or NPL… |
| Point of contact | Designate a point of contact to interact with CERT-In |
Learn more in the lesson: 34.3 CERT-In Directions for Organisations