Ravi Sir's Cyber Security Cards › Revision Cards
Bug Bounty
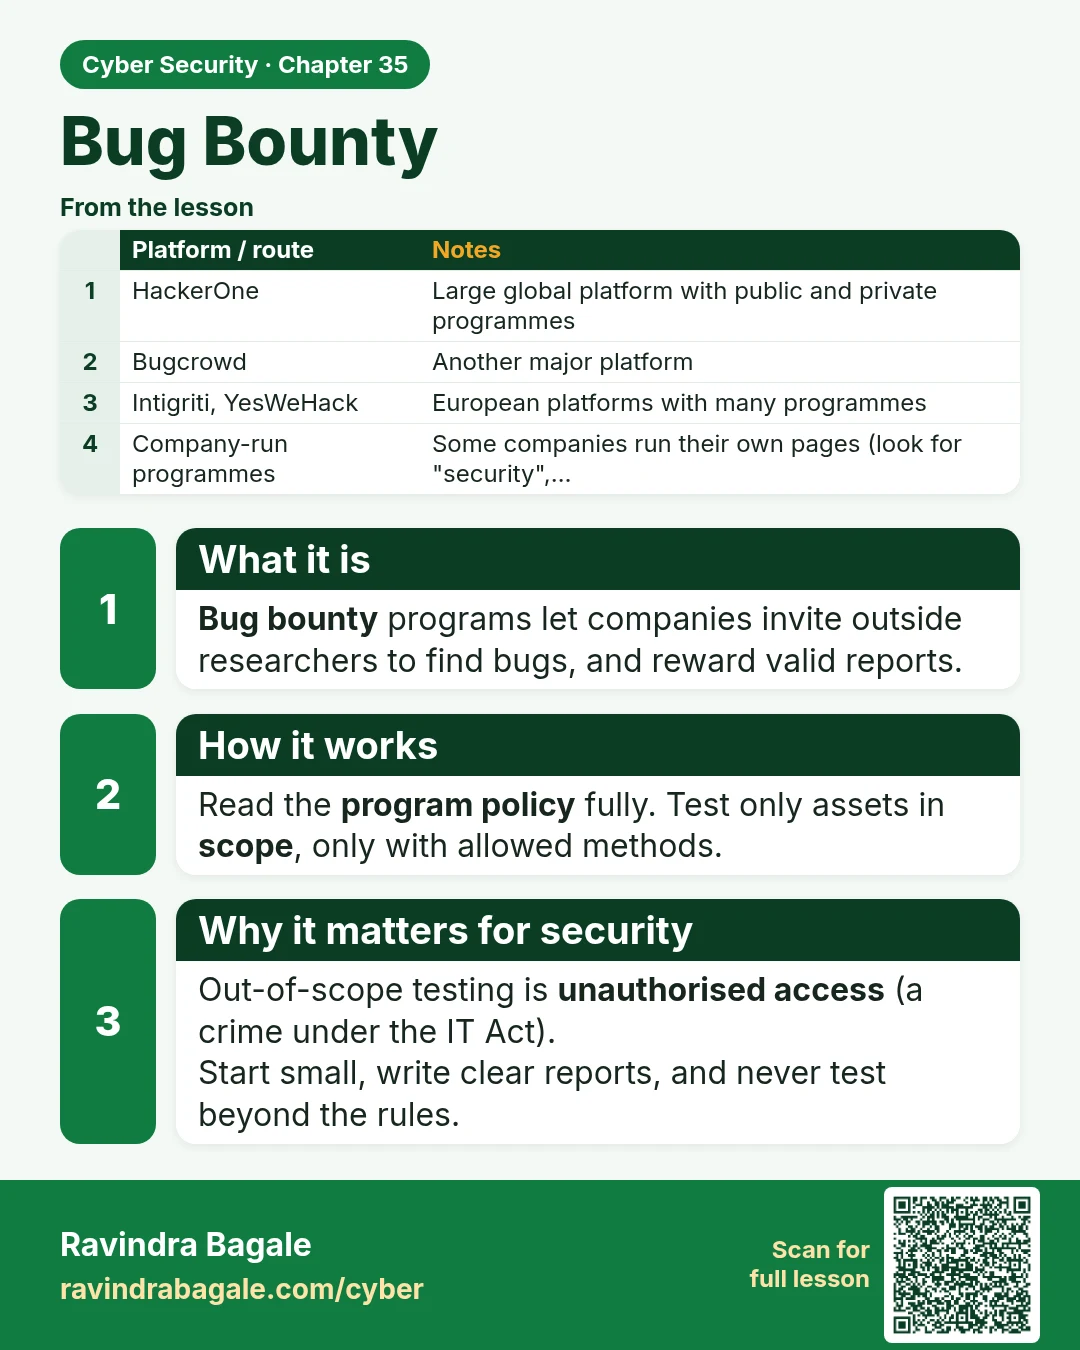
Bug Bounty Bug bounty programs let companies invite outside researchers to find bugs, and reward valid reports. Read the program policy fully. Test only assets in scope , only with allowed methods. Out-of-scope testing is unauthorised access (a crime under the IT Act). Start small, write clear repor
Read card text
What this card says
What it is
Bug bounty programs let companies invite outside researchers to find bugs, and reward valid reports.
How it works
Read the program policy fully. Test only assets in scope, only with allowed methods.
Why it matters for security
Out-of-scope testing is unauthorised access (a crime under the IT Act).
Start small, write clear reports, and never test beyond the rules.
| Platform / route | Notes |
|---|---|
| HackerOne | Large global platform with public and private programmes |
| Bugcrowd | Another major platform |
| Intigriti, YesWeHack | European platforms with many programmes |
| Company-run programmes | Some companies run their own pages (look for "security",… |
Learn more in the lesson: 35.5 Bug Bounty