Ravi Sir's Cyber Security Cards › Revision Cards
Application-Level Hijack – URL Tokens, CSRF, JWT Concepts
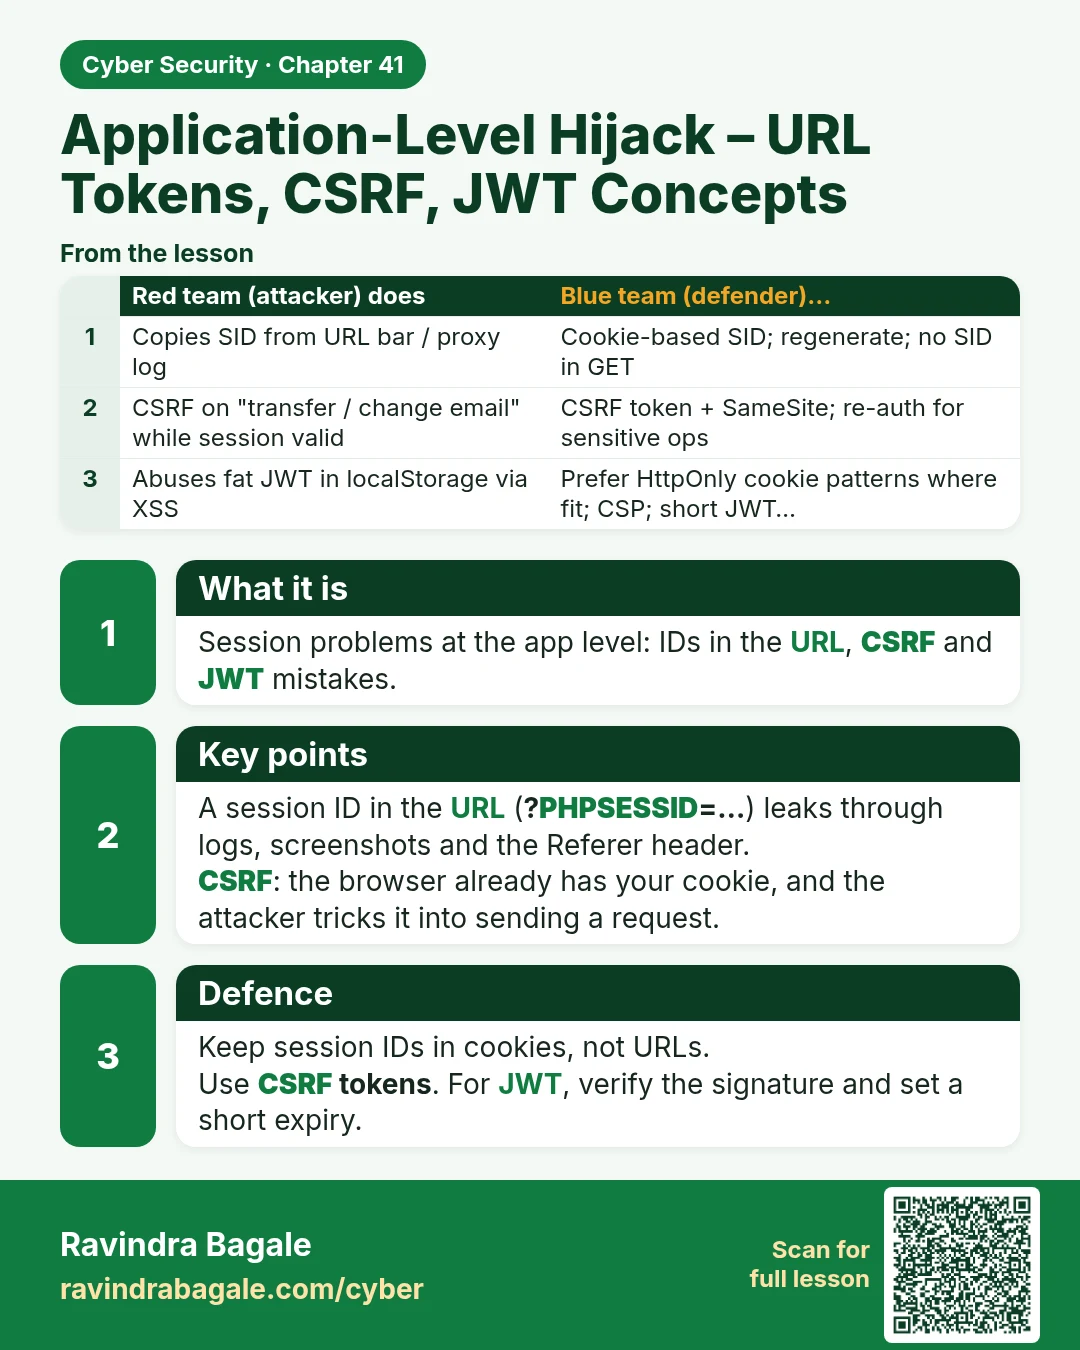
Application-Level Hijack – URL Tokens, CSRF, JWT Concepts Session problems at the app level: IDs in the URL, CSRF and JWT mistakes. A session ID in the URL ( ?PHPSESSID=… ) leaks through logs, screenshots and the Referer header. CSRF : the browser already has your cookie, and the attacker tricks it
Read card text
What this card says
What it is
Session problems at the app level: IDs in the URL, CSRF and JWT mistakes.
Key points
A session ID in the URL (?PHPSESSID=…) leaks through logs, screenshots and the Referer header.
CSRF: the browser already has your cookie, and the attacker tricks it into sending a request.
Defence
Keep session IDs in cookies, not URLs.
Use CSRF tokens. For JWT, verify the signature and set a short expiry.
| Red team (attacker) does | Blue team (defender)… |
|---|---|
| Copies SID from URL bar / proxy log | Cookie-based SID; regenerate; no SID in GET |
| CSRF on "transfer / change email" while session valid | CSRF token + SameSite; re-auth for sensitive ops |
| Abuses fat JWT in localStorage via XSS | Prefer HttpOnly cookie patterns where fit; CSP; short JWT… |
Learn more in the lesson: 41.6 Application-Level Hijack – URL Tokens, CSRF, JWT Concepts