Ravi Sir's Cyber Security Cards › Revision Cards
Application-Layer DoS – Slow and Heavy Requests
Application-Layer DoS – Slow and Heavy Requests An application-layer DoS overwhelms the app itself, not the network. It needs far less traffic. Many requests to expensive pages (search, report export). Slowloris : hold many connections open very slowly, so all worker slots are used up. Rate limits,
Read card text
What this card says
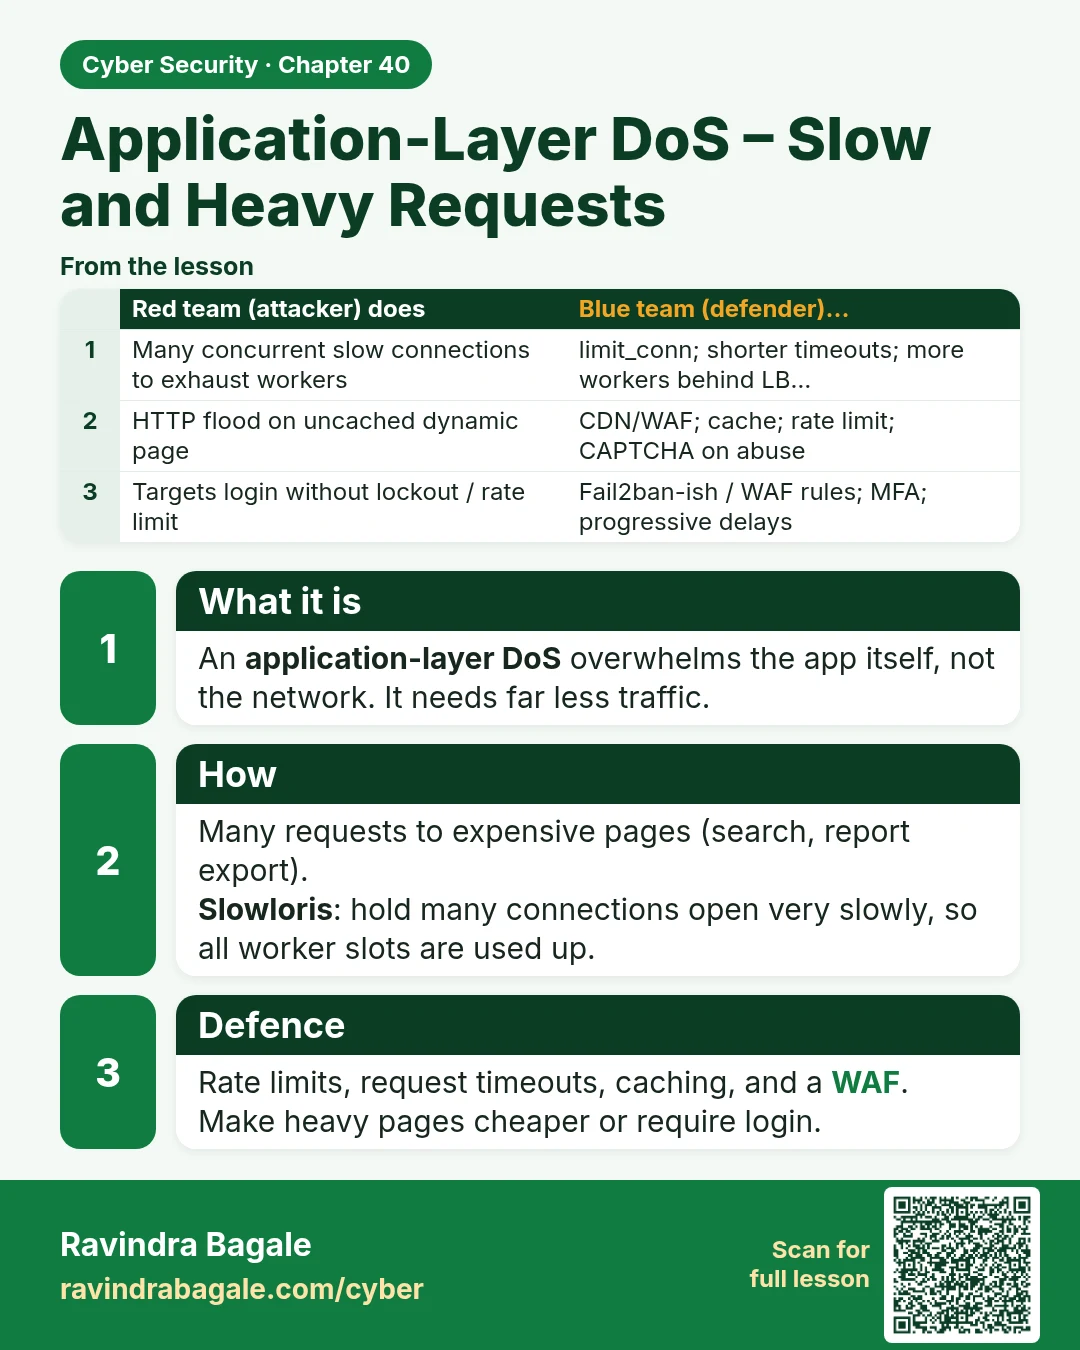
What it is
An application-layer DoS overwhelms the app itself, not the network. It needs far less traffic.
How
Many requests to expensive pages (search, report export).
Slowloris: hold many connections open very slowly, so all worker slots are used up.
Defence
Rate limits, request timeouts, caching, and a WAF.
Make heavy pages cheaper or require login.
| Red team (attacker) does | Blue team (defender)… |
|---|---|
| Many concurrent slow connections to exhaust workers | limit_conn; shorter timeouts; more workers behind LB… |
| HTTP flood on uncached dynamic page | CDN/WAF; cache; rate limit; CAPTCHA on abuse |
| Targets login without lockout / rate limit | Fail2ban-ish / WAF rules; MFA; progressive delays |
Learn more in the lesson: 40.5 Application-Layer DoS – Slow and Heavy Requests