Ravi Sir's Cyber Security Cards › Revision Cards
A03 Injection: Cross-Site Scripting (XSS)
A03 Injection: Cross-Site Scripting (XSS) XSS (Cross-Site Scripting): an attacker gets their script to run in another user’s browser on your site. A comment box saves a script that sends each viewer’s session cookie to the attacker. Then the attacker can log in as them. Encode output so text shows a
Read card text
What this card says
What it is
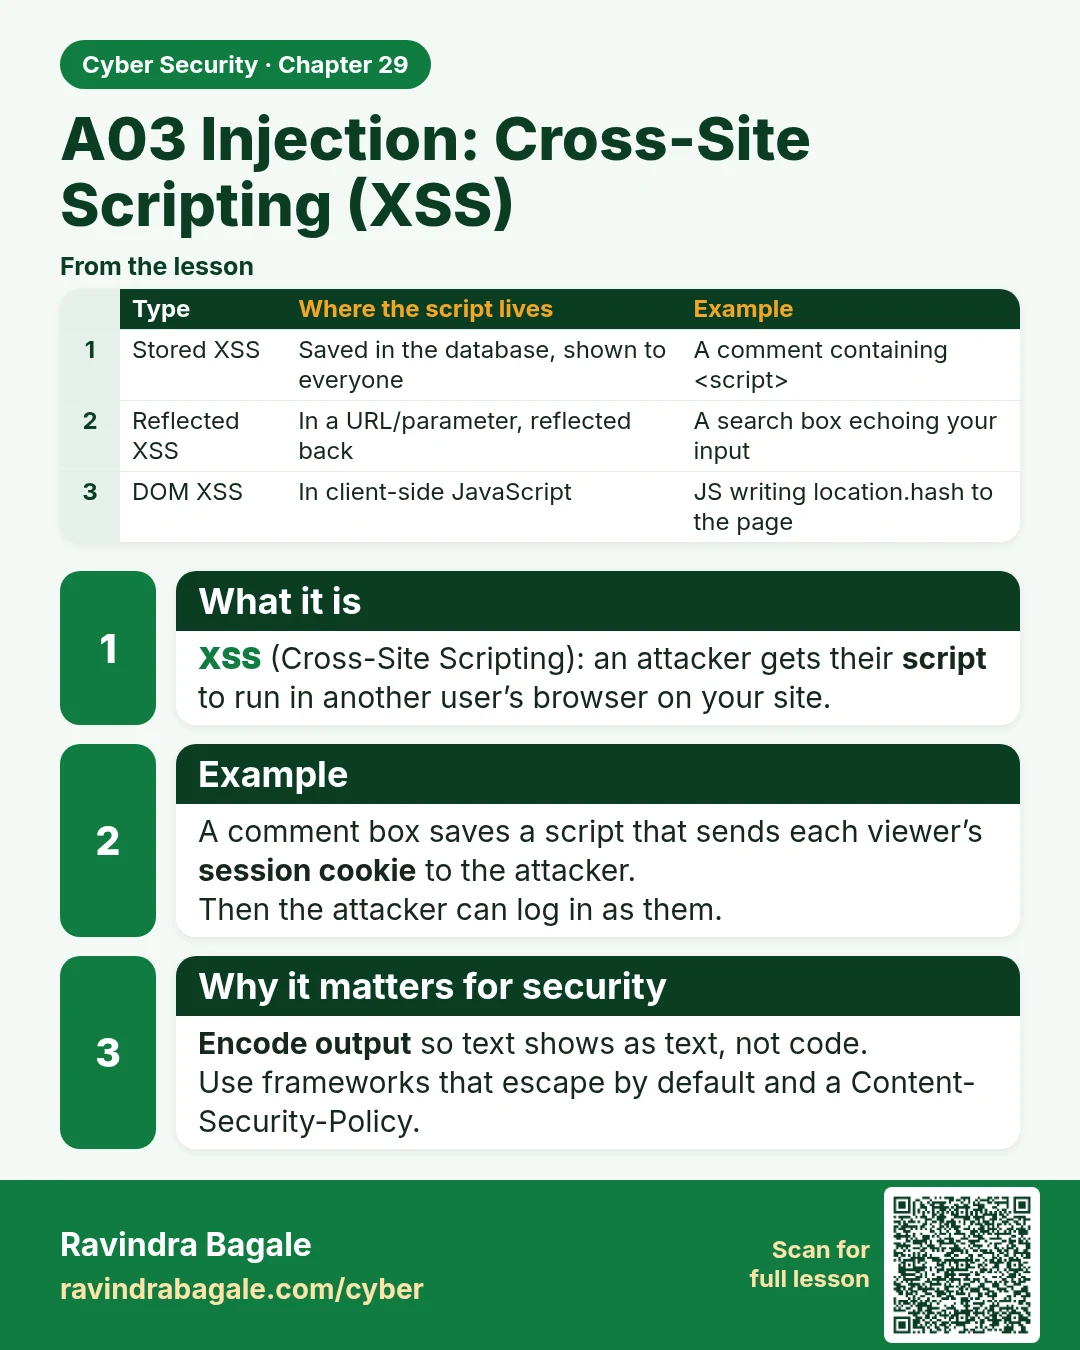
XSS (Cross-Site Scripting): an attacker gets their script to run in another user’s browser on your site.
Example
A comment box saves a script that sends each viewer’s session cookie to the attacker.
Then the attacker can log in as them.
Why it matters for security
Encode output so text shows as text, not code.
Use frameworks that escape by default and a Content-Security-Policy.
| Type | Where the script lives | Example |
|---|---|---|
| Stored XSS | Saved in the database, shown to everyone | A comment containing |