Ravi Sir's Cyber Security Cards › Revision Cards
A03 Injection: Command Injection
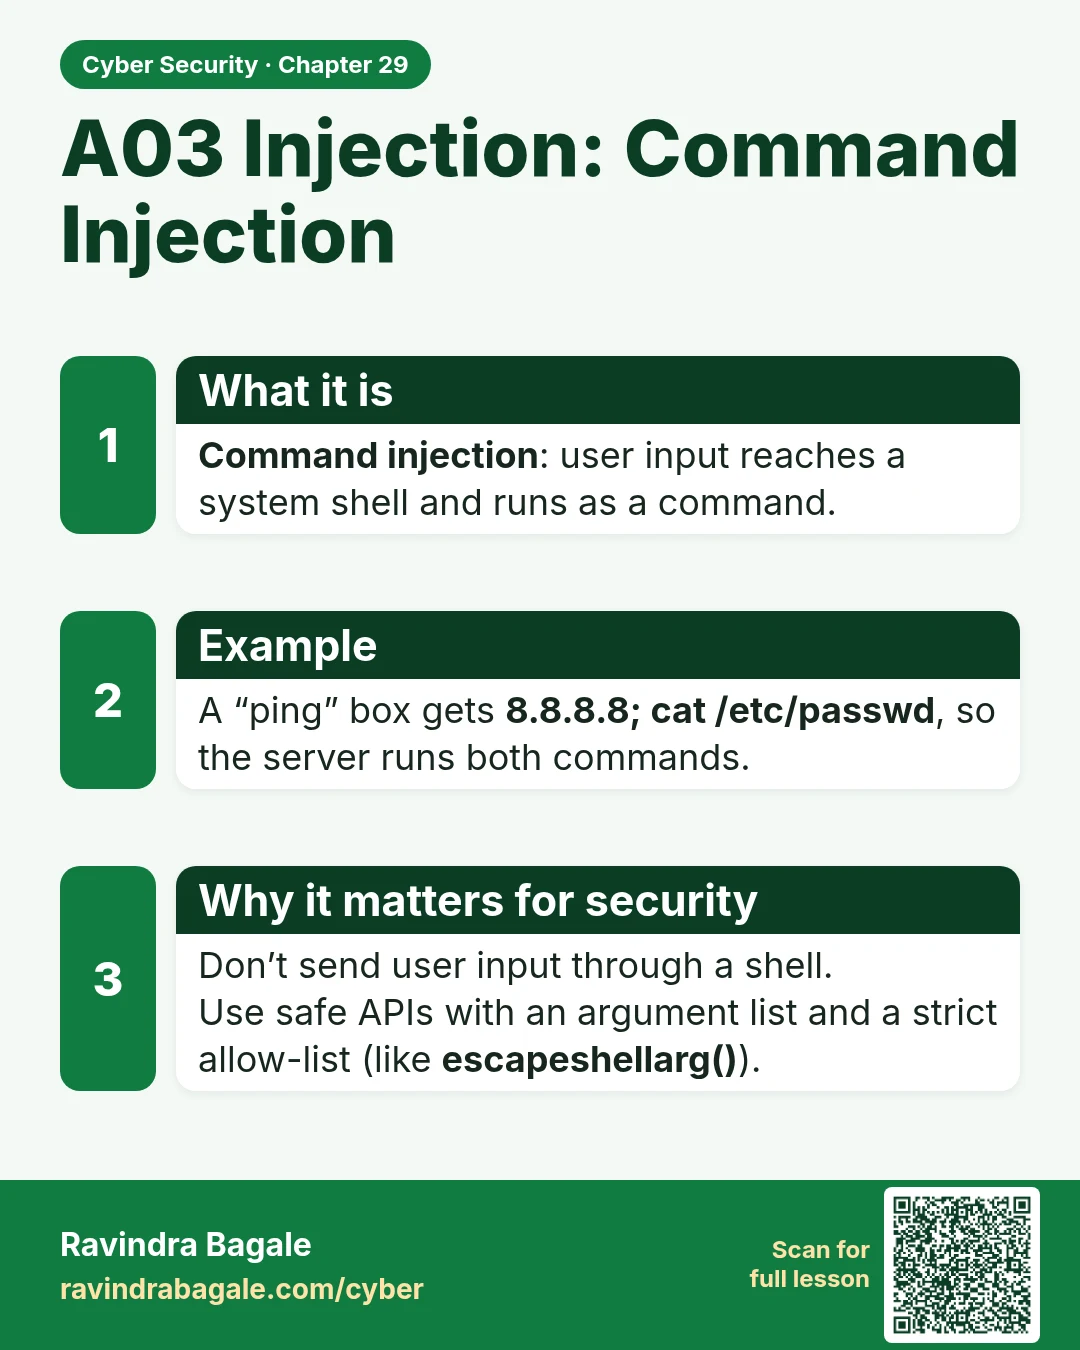
A03 Injection: Command Injection Command injection : user input reaches a system shell and runs as a command. A “ping” box gets 8.8.8.8; cat /etc/passwd , so the server runs both commands. Don’t send user input through a shell. Use safe APIs with an argument list and a strict allow-list (like escape
Read card text
What this card says
What it is
Command injection: user input reaches a system shell and runs as a command.
Example
A “ping” box gets 8.8.8.8; cat /etc/passwd, so the server runs both commands.
Why it matters for security
Don’t send user input through a shell.
Use safe APIs with an argument list and a strict allow-list (like escapeshellarg()).
Learn more in the lesson: 29.4 A03 Injection: Command Injection