Ravi Sir's Cyber Security Cards › Revision Cards
A PHP + MySQL Application with Prepared Statements
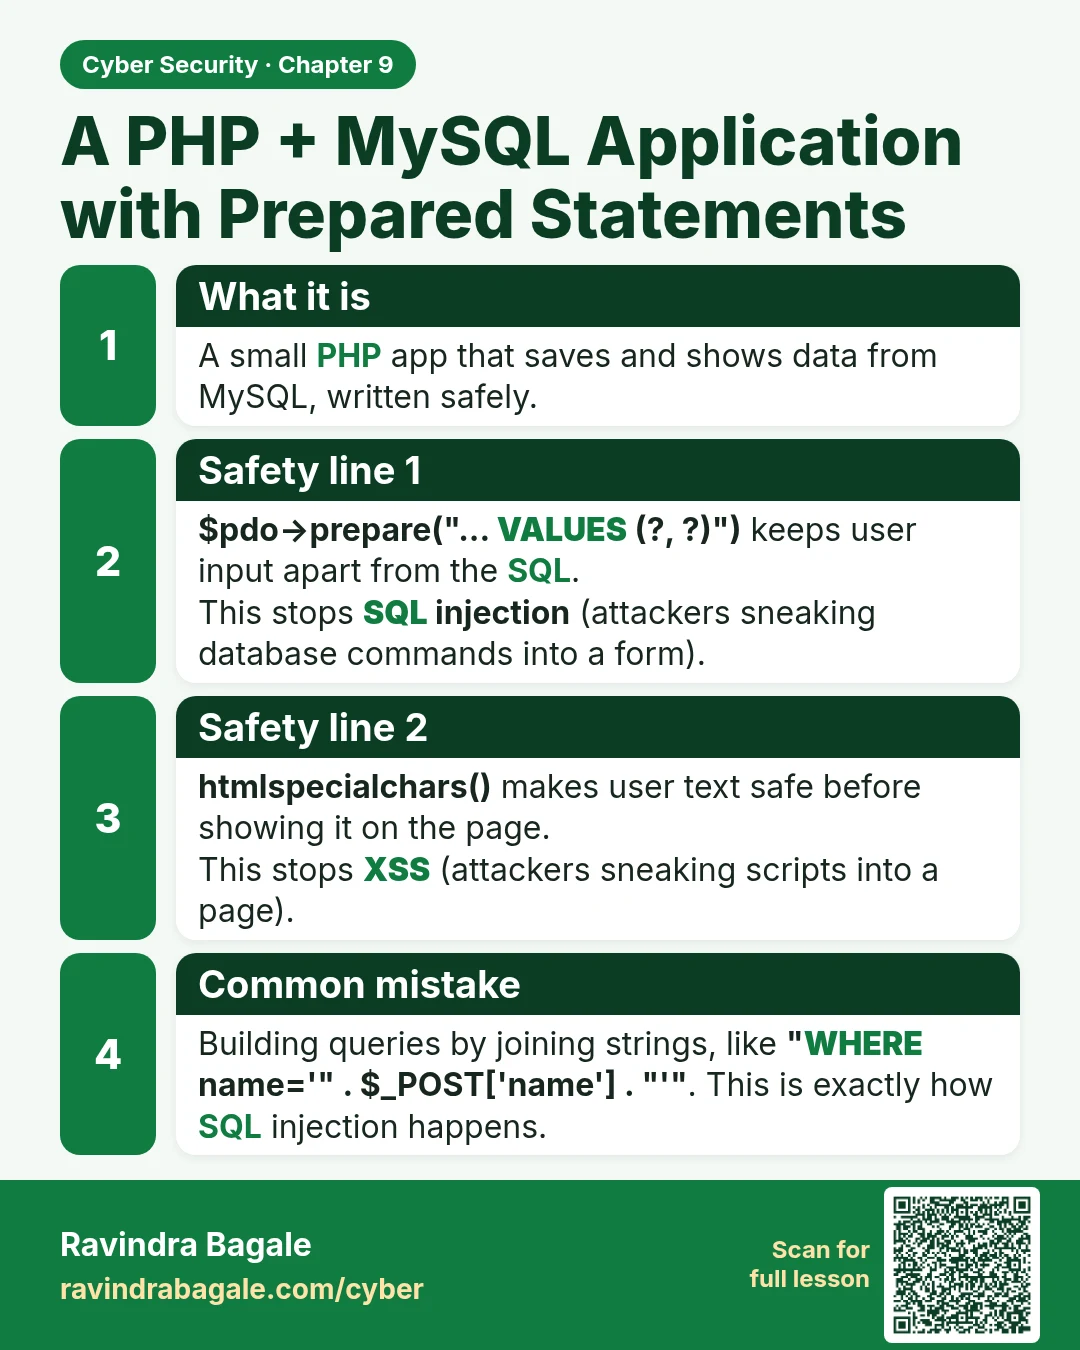
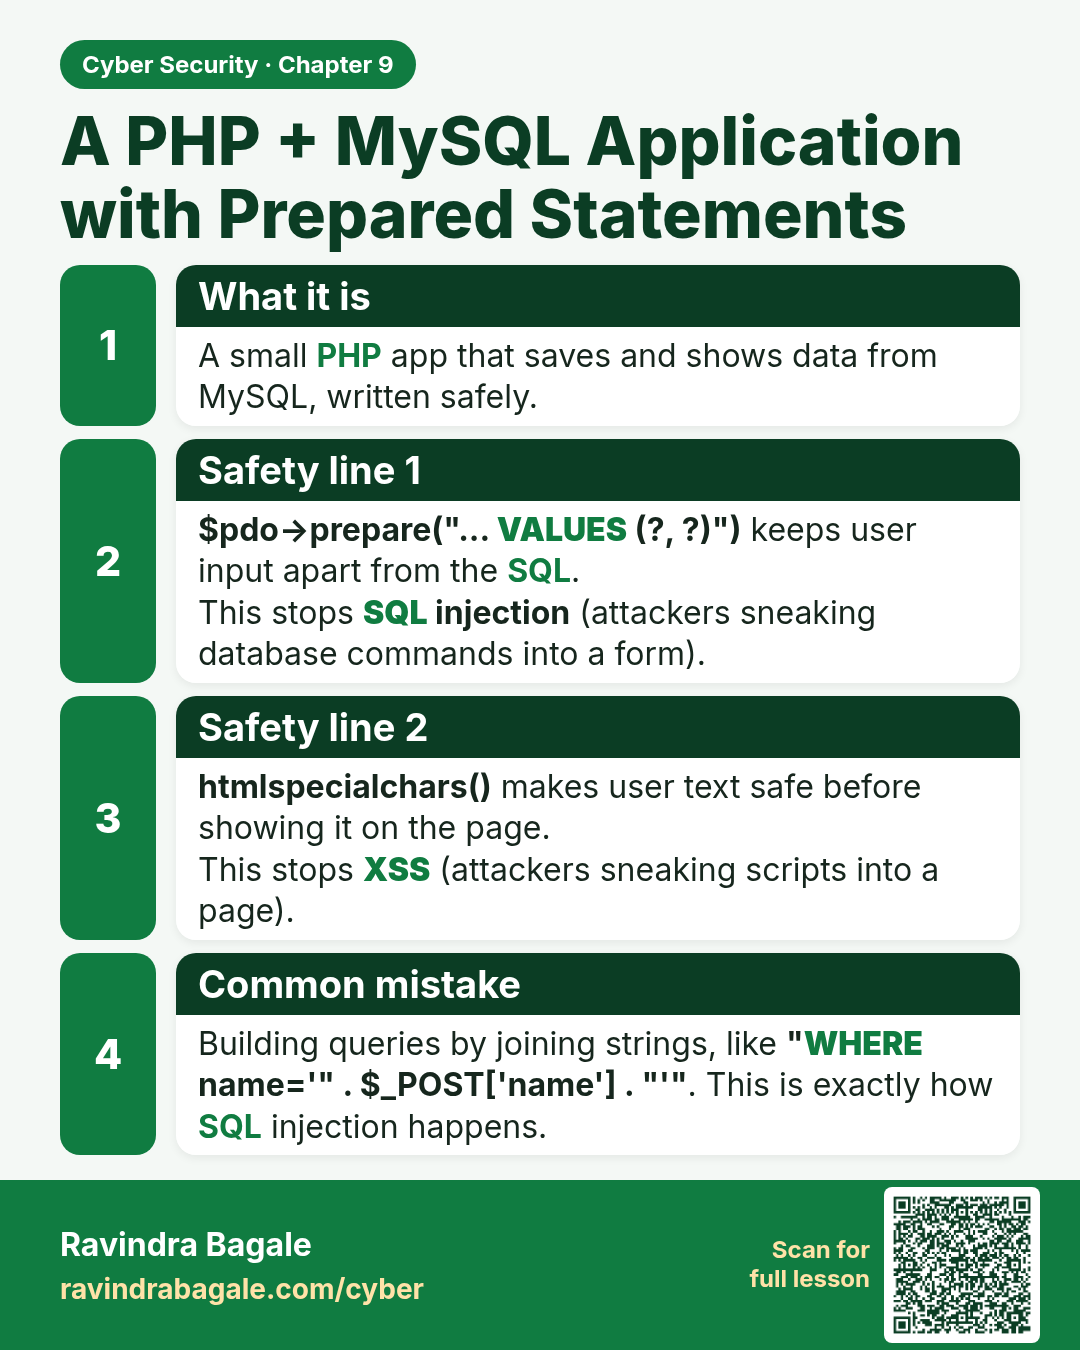
A PHP + MySQL Application with Prepared Statements A small PHP app that saves and shows data from MySQL, written safely. $pdo->prepare("... VALUES (?, ?)") keeps user input apart from the SQL. This stops SQL injection (attackers sneaking database commands into a form). htmlspecialchars() makes user
Read card text
What this card says
What it is
A small PHP app that saves and shows data from MySQL, written safely.
Safety line 1
$pdo->prepare("... VALUES (?, ?)") keeps user input apart from the SQL.
This stops SQL injection (attackers sneaking database commands into a form).
Safety line 2
htmlspecialchars() makes user text safe before showing it on the page.
This stops XSS (attackers sneaking scripts into a page).
Common mistake
Building queries by joining strings, like "WHERE name='" . $_POST['name'] . "'". This is exactly how SQL injection happens.
Learn more in the lesson: 9.7 A PHP + MySQL Application with Prepared Statements