Ravi Sir's Cyber Security Cards › Interview Cards
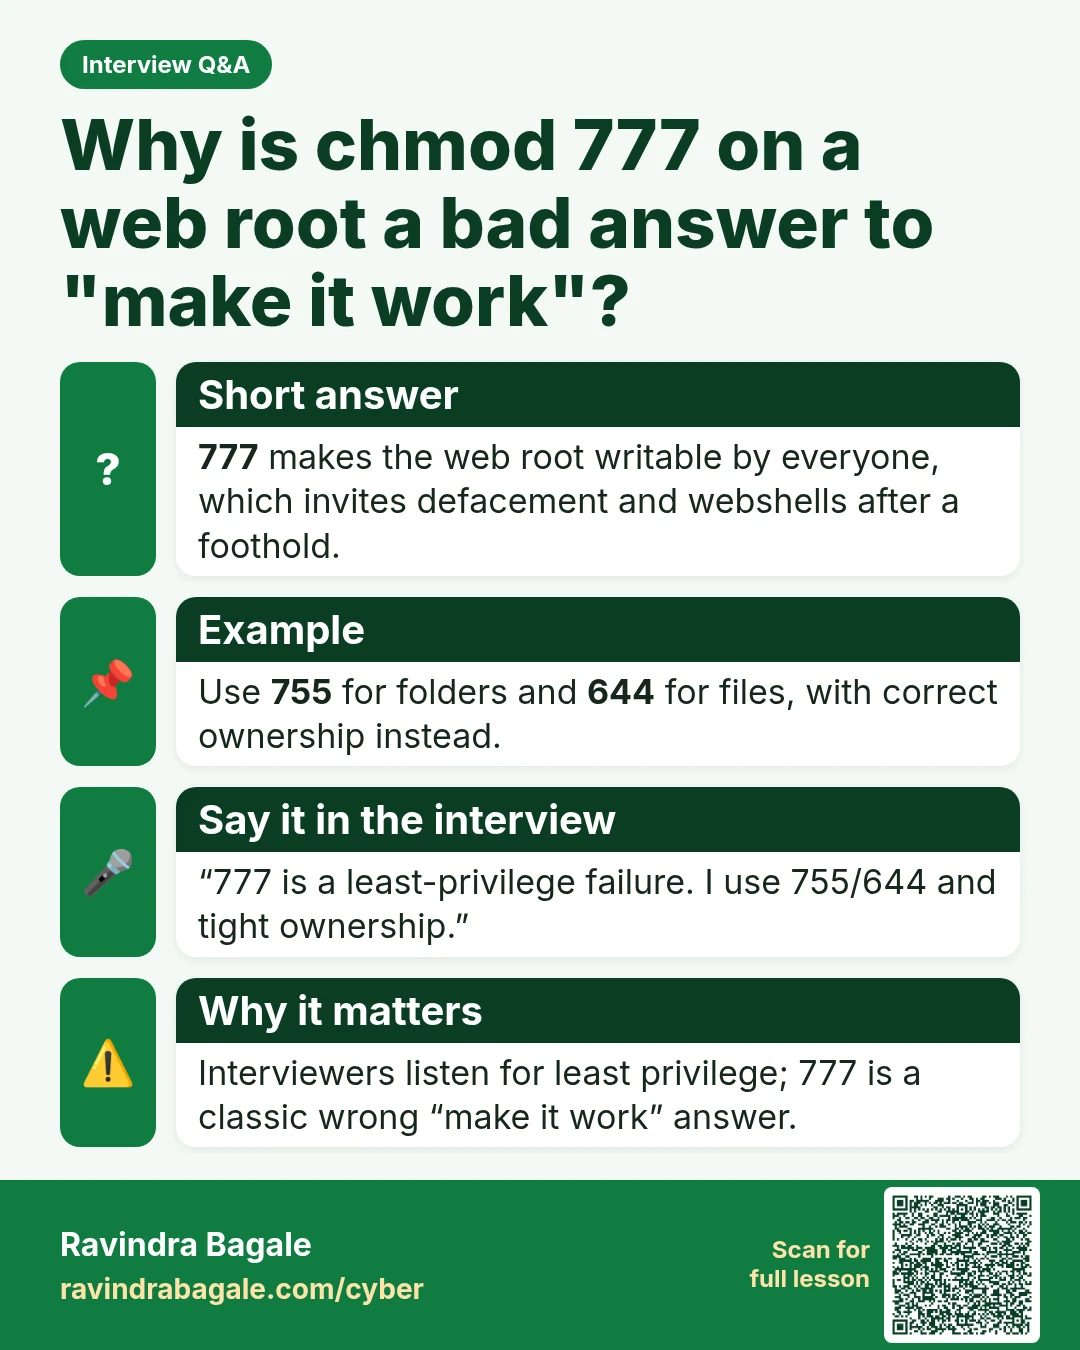
Why is chmod 777 on a web root a bad answer to "make it work"?
Why is chmod 777 on a web root a bad answer to "make it work"? 777 makes the web root writable by everyone, which invites defacement and webshells after a foothold. Use 755 for folders and 644 for files, with correct ownership instead. “777 is a least-privilege failure. I use 755/644 and tight owner
Read card text
What this card says
Short answer
777 makes the web root writable by everyone, which invites defacement and webshells after a foothold.
Example
Use 755 for folders and 644 for files, with correct ownership instead.
Say it in the interview
“777 is a least-privilege failure. I use 755/644 and tight ownership.”
Why it matters
Interviewers listen for least privilege; 777 is a classic wrong “make it work” answer.
Learn more in the lesson: 47.3 Linux, Logs and Windows Event IDs