Ravi Sir's Cyber Security Cards › Interview Cards
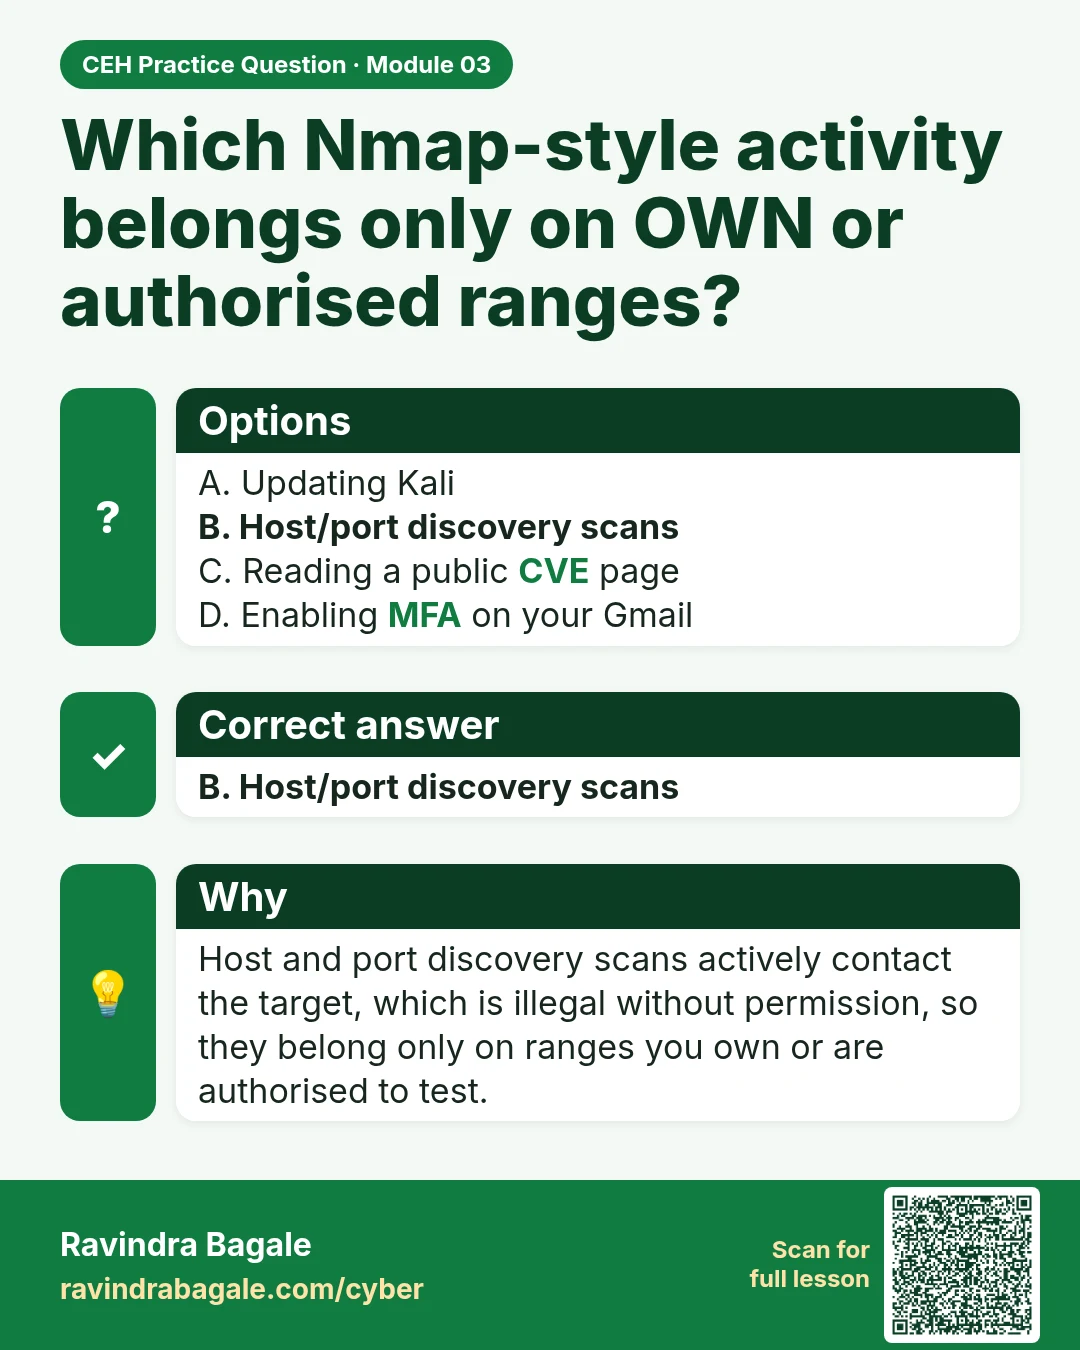
Which Nmap-style activity belongs only on OWN or authorised ranges?
Which Nmap-style activity belongs only on OWN or authorised ranges? A. Updating Kali B. Host/port discovery scans C. Reading a public CVE page D. Enabling MFA on your Gmail B. Host/port discovery scans Host and port discovery scans actively contact the target, which is illegal without permission, so
Read card text
What this card says
Options
A. Updating Kali
B. Host/port discovery scans
C. Reading a public CVE page
D. Enabling MFA on your Gmail
Correct answer
B. Host/port discovery scans
Why
Host and port discovery scans actively contact the target, which is illegal without permission, so they belong only on ranges you own or are authorised to test.
Learn more in the lesson: 48.6 CEH-Style Practice Questions – Set A (Modules 01–10)