Ravi Sir's Cyber Security Cards › Interview Cards
What is IDOR?
What is IDOR? IDOR = Insecure Direct Object Reference. A user changes an ID number in a link and sees another user’s data , because the server does not check who owns it. Ravi opens shop.example/order?id= 1001 (his order). He changes it to id= 1002 and sees Priya’s name and address. That is IDOR. “T
Read card text
What this card says
Short answer
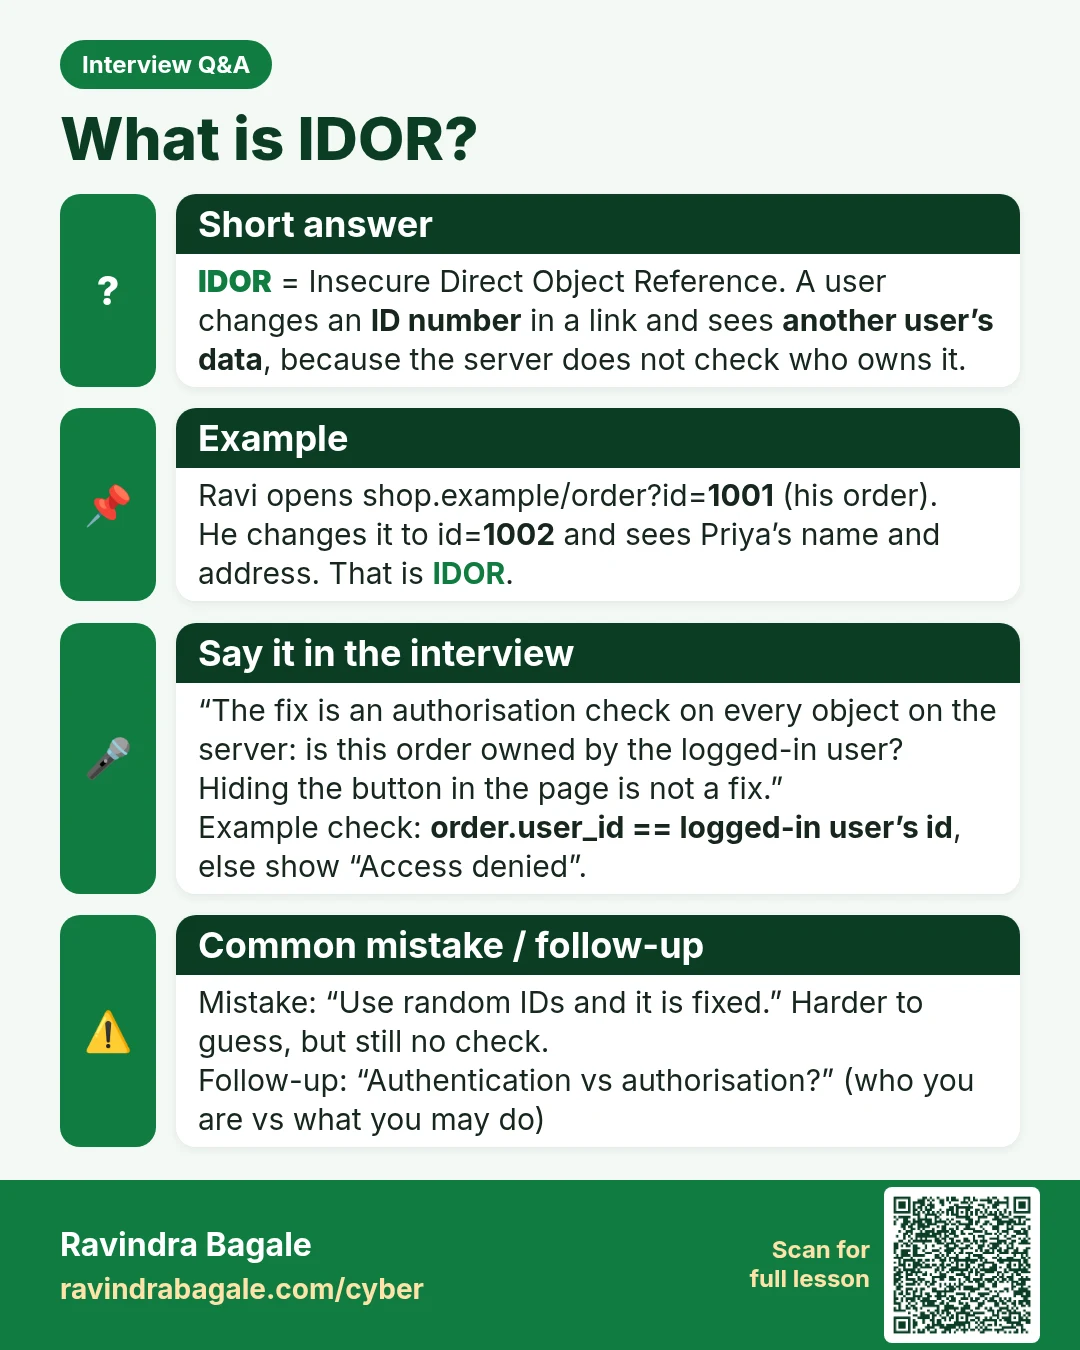
IDOR = Insecure Direct Object Reference. A user changes an ID number in a link and sees another user’s data, because the server does not check who owns it.
Example
Ravi opens shop.example/order?id=1001 (his order).
He changes it to id=1002 and sees Priya’s name and address. That is IDOR.
Say it in the interview
“The fix is an authorisation check on every object on the server: is this order owned by the logged-in user? Hiding the button in the page is not a fix.”
Example check: order.user_id == logged-in user’s id, else show “Access denied”.
Common mistake / follow-up
Mistake: “Use random IDs and it is fixed.” Harder to guess, but still no check.
Follow-up: “Authentication vs authorisation?” (who you are vs what you may do)
Learn more in the lesson: 46.7 Ethical Hacking, OWASP and Kali Lab Questions