Ravi Sir's Cyber Security Cards › Interview Cards
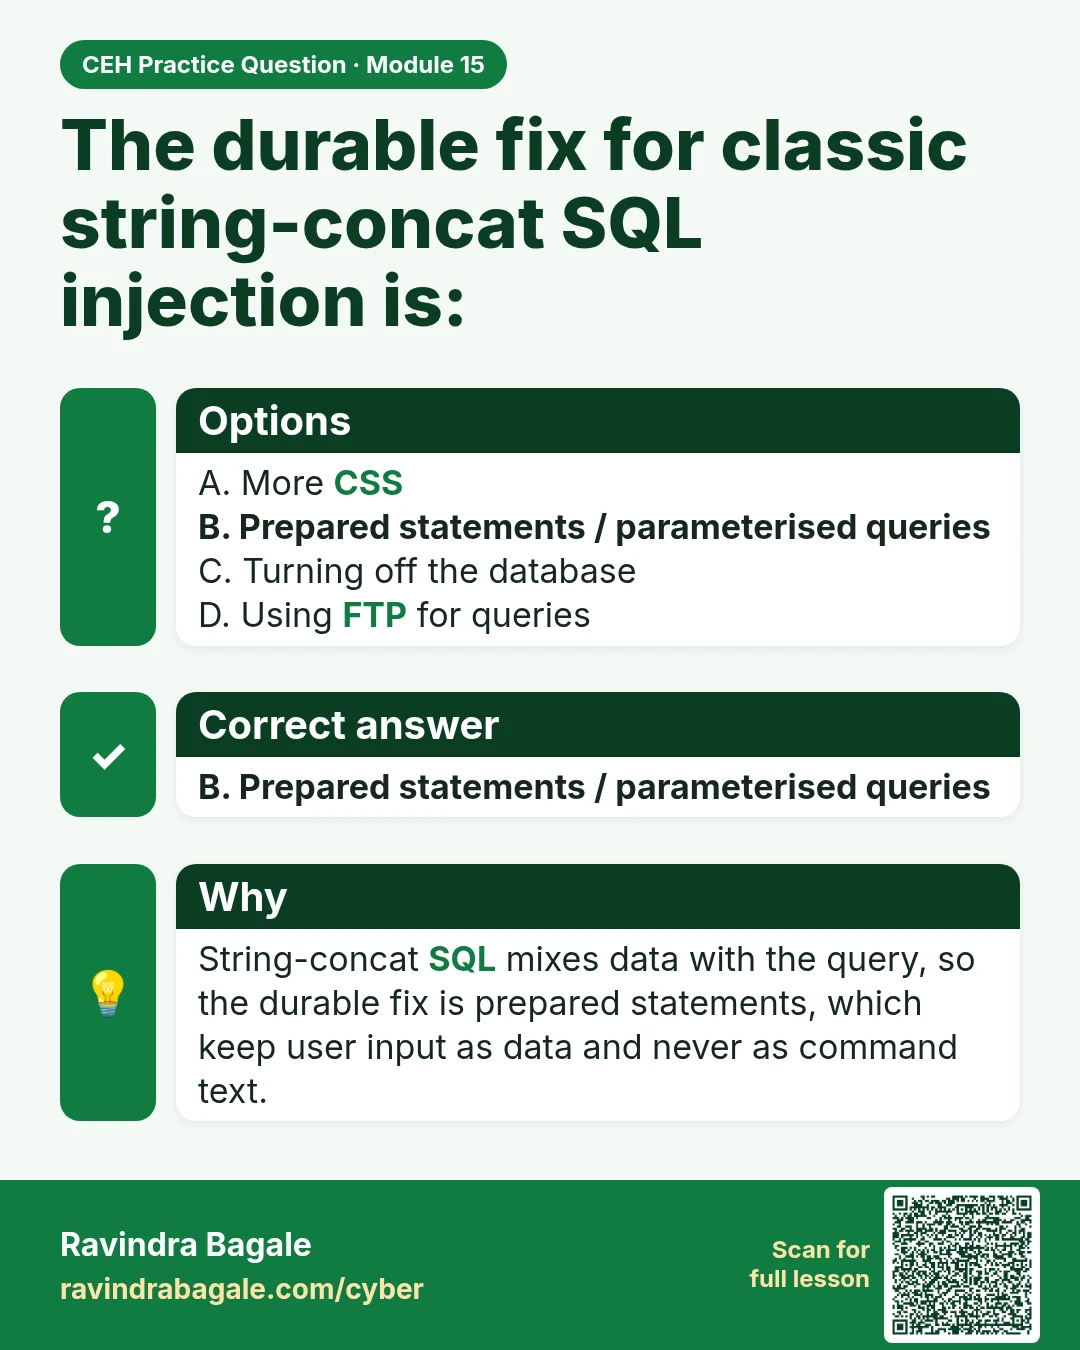
The durable fix for classic string-concat SQL injection is:
The durable fix for classic string-concat SQL injection is: A. More CSS B. Prepared statements / parameterised queries C. Turning off the database D. Using FTP for queries B. Prepared statements / parameterised queries String-concat SQL mixes data with the query, so the durable fix is prepared state
Read card text
What this card says
Options
A. More CSS
B. Prepared statements / parameterised queries
C. Turning off the database
D. Using FTP for queries
Correct answer
B. Prepared statements / parameterised queries
Why
String-concat SQL mixes data with the query, so the durable fix is prepared statements, which keep user input as data and never as command text.
Learn more in the lesson: 48.7 CEH-Style Practice Questions – Set B (Modules 11–20)