Ravi Sir's Cyber Security Cards › Comparison Cards
Static vs Dynamic Analysis Mindset
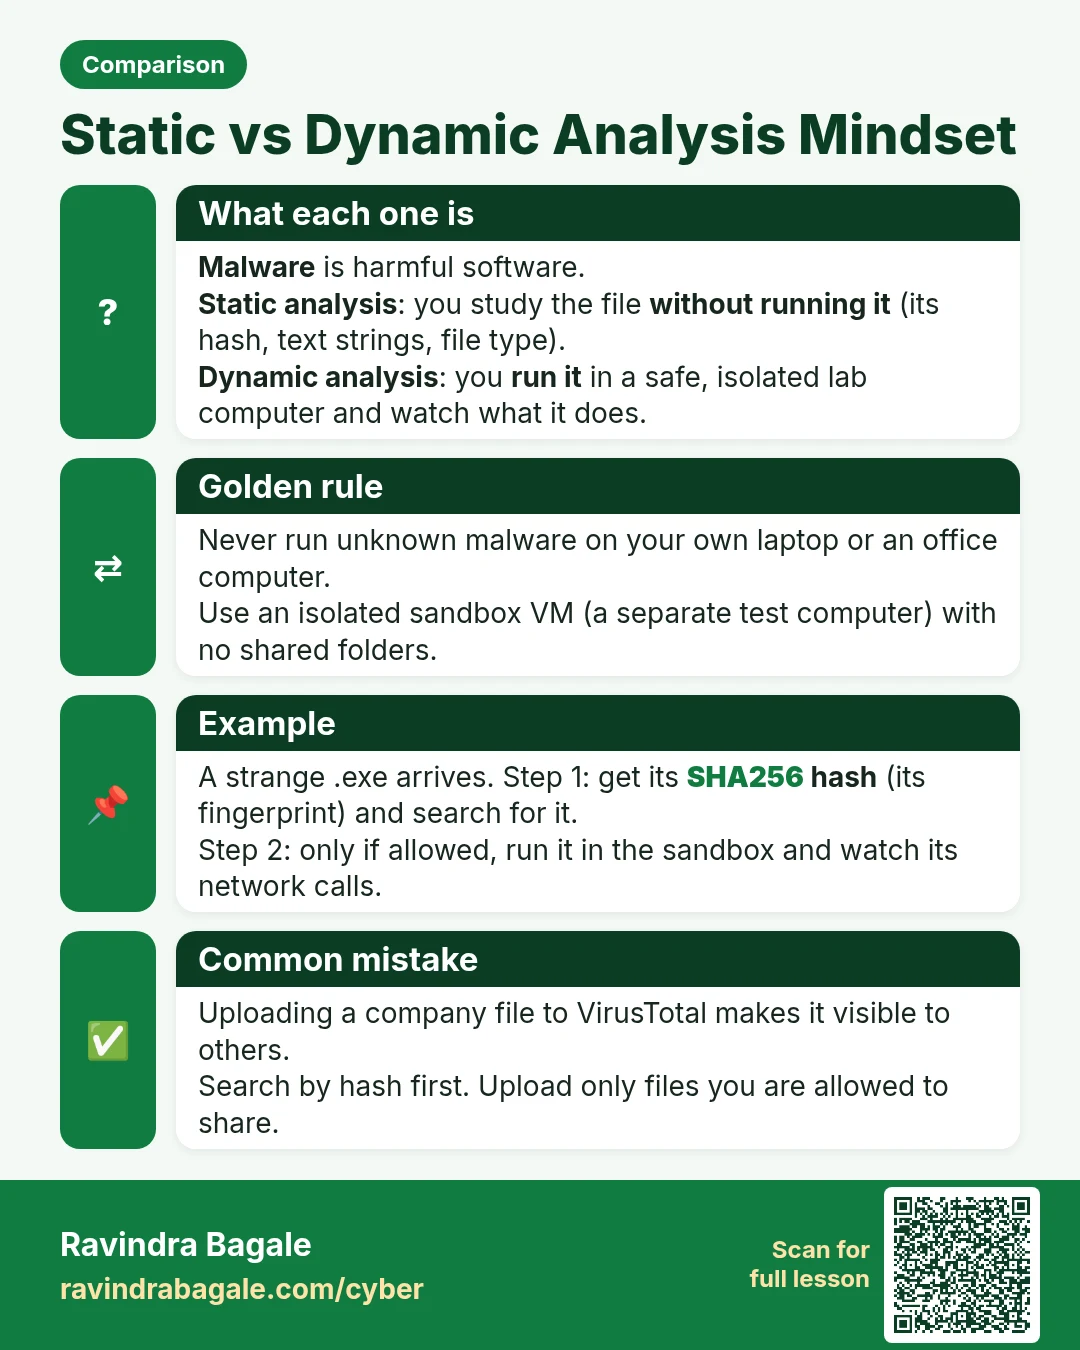
Static vs Dynamic Analysis Mindset Malware is harmful software. Static analysis : you study the file without running it (its hash, text strings, file type). Dynamic analysis : you run it in a safe, isolated lab computer and watch what it does. Never run unknown malware on your own laptop or an offic
Read card text
What this card says
What each one is
Malware is harmful software.
Static analysis: you study the file without running it (its hash, text strings, file type).
Dynamic analysis: you run it in a safe, isolated lab computer and watch what it does.
Golden rule
Never run unknown malware on your own laptop or an office computer.
Use an isolated sandbox VM (a separate test computer) with no shared folders.
Example
A strange .exe arrives. Step 1: get its SHA256 hash (its fingerprint) and search for it.
Step 2: only if allowed, run it in the sandbox and watch its network calls.
Common mistake
Uploading a company file to VirusTotal makes it visible to others.
Search by hash first. Upload only files you are allowed to share.
| Red team (attacker) does | Blue team (defender)… |
|---|---|
| Packs / obfuscates to change hash daily | Behaviour EDR + sandbox detonation, not hash-only AV |
| Checks sandbox artifacts (short uptime, known VM MAC) | Multiple analysis layers; don't rely on one public sandbox… |
| Hopes analyst uploads secret docs to public VT | Policy: no confidential uploads; private instance /… |
Learn more in the lesson: 39.4 Static vs Dynamic Analysis Mindset