Ravi Sir's Cyber Security Cards › Comparison Cards
Slow Scans, Timing, Port Knocking – Nmap vs Blue Rate Alerts
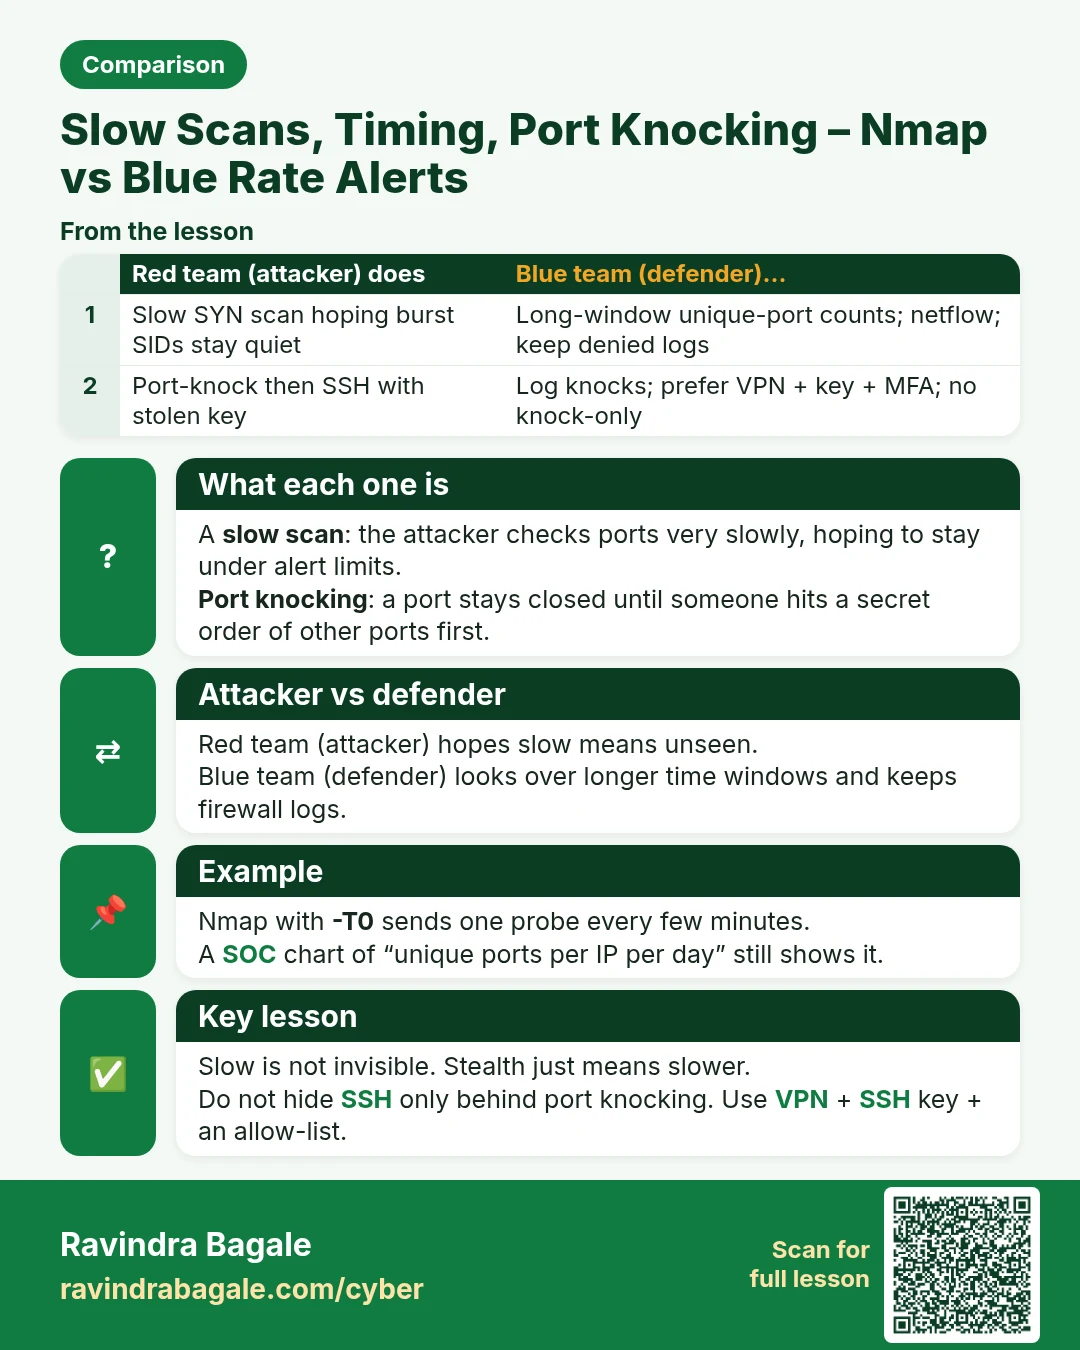
Slow Scans, Timing, Port Knocking – Nmap vs Blue Rate Alerts A slow scan : the attacker checks ports very slowly, hoping to stay under alert limits. Port knocking : a port stays closed until someone hits a secret order of other ports first. Red team (attacker) hopes slow means unseen. Blue team (def
Read card text
What this card says
What each one is
A slow scan: the attacker checks ports very slowly, hoping to stay under alert limits.
Port knocking: a port stays closed until someone hits a secret order of other ports first.
Attacker vs defender
Red team (attacker) hopes slow means unseen.
Blue team (defender) looks over longer time windows and keeps firewall logs.
Example
Nmap with -T0 sends one probe every few minutes.
A SOC chart of “unique ports per IP per day” still shows it.
Key lesson
Slow is not invisible. Stealth just means slower.
Do not hide SSH only behind port knocking. Use VPN + SSH key + an allow-list.
| Red team (attacker) does | Blue team (defender)… |
|---|---|
| Slow SYN scan hoping burst SIDs stay quiet | Long-window unique-port counts; netflow; keep denied logs |
| Port-knock then SSH with stolen key | Log knocks; prefer VPN + key + MFA; no knock-only |
| Scans from many IPs (lab: don't) | Correlate in SIEM; block lists with care (false drop risk) |
Learn more in the lesson: 42.4 Slow Scans, Timing, Port Knocking – Nmap vs Blue Rate Alerts