Ravi Sir's Cyber Security Cards › Comparison Cards
Security group versus NACLs – interview short form?
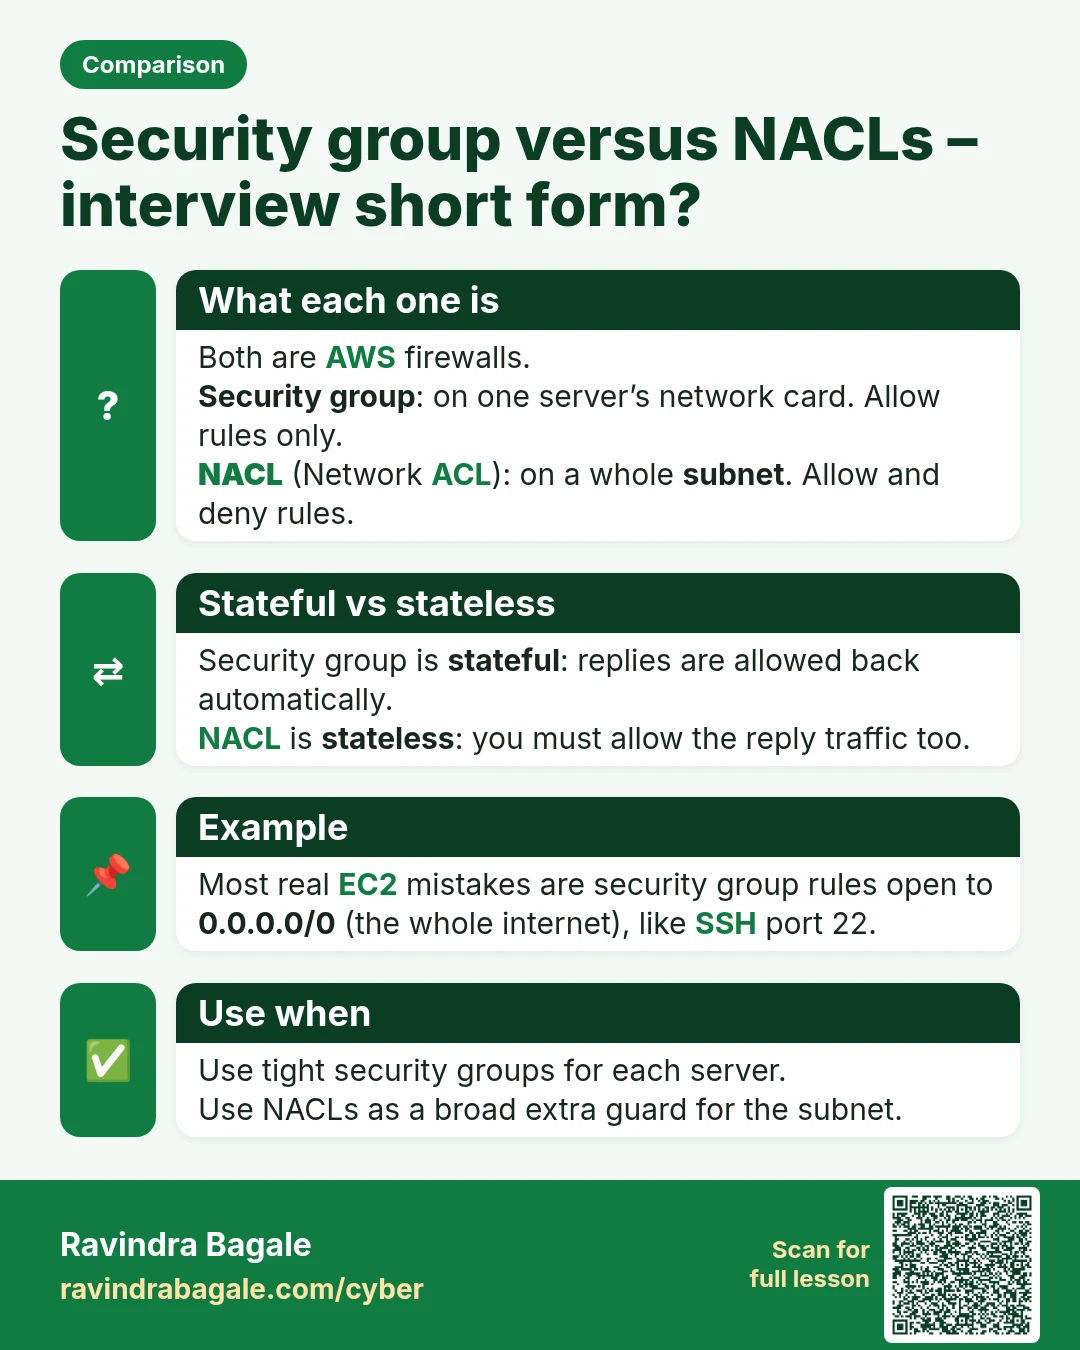
Security group versus NACLs – interview short form? Both are AWS firewalls. Security group : on one server’s network card. Allow rules only. NACL (Network ACL): on a whole subnet . Allow and deny rules. Security group is stateful : replies are allowed back automatically. NACL is stateless : you must
Read card text
What this card says
What each one is
Both are AWS firewalls.
Security group: on one server’s network card. Allow rules only.
NACL (Network ACL): on a whole subnet. Allow and deny rules.
Stateful vs stateless
Security group is stateful: replies are allowed back automatically.
NACL is stateless: you must allow the reply traffic too.
Example
Most real EC2 mistakes are security group rules open to 0.0.0.0/0 (the whole internet), like SSH port 22.
Use when
Use tight security groups for each server.
Use NACLs as a broad extra guard for the subnet.
Learn more in the lesson: 47.6 Cloud and AWS Security MNC Themes