Ravi Sir's Cyber Security Cards › Comparison Cards
Prepared statements versus escaping – which do you prefer?
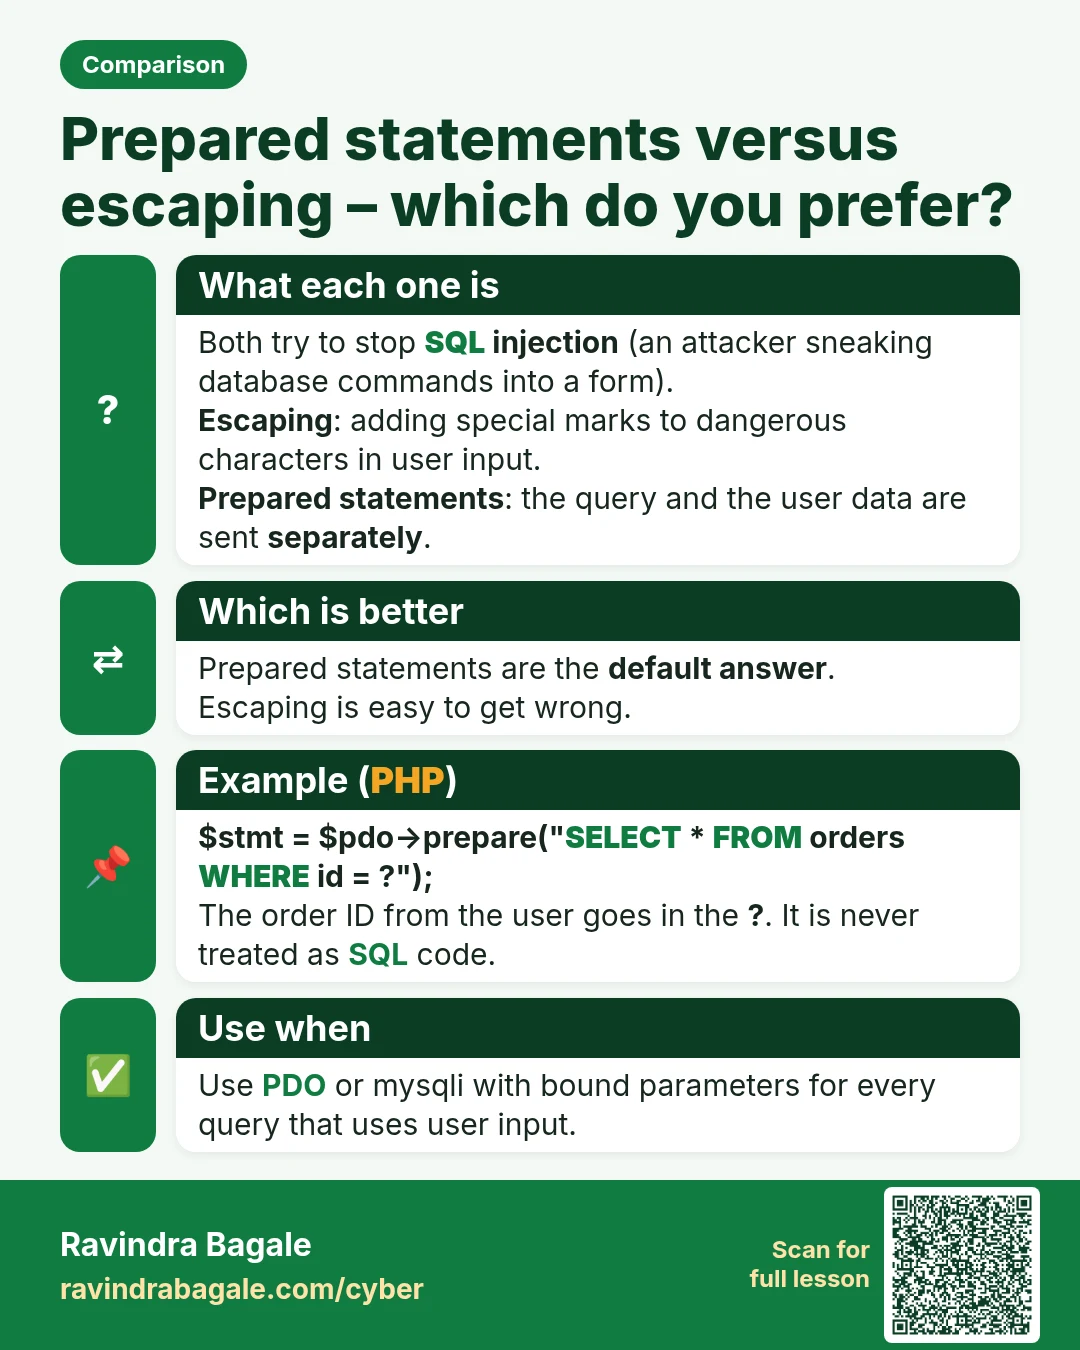
Prepared statements versus escaping – which do you prefer? Both try to stop SQL injection (an attacker sneaking database commands into a form). Escaping : adding special marks to dangerous characters in user input. Prepared statements : the query and the user data are sent separately . Prepared stat
Read card text
What this card says
What each one is
Both try to stop SQL injection (an attacker sneaking database commands into a form).
Escaping: adding special marks to dangerous characters in user input.
Prepared statements: the query and the user data are sent separately.
Which is better
Prepared statements are the default answer.
Escaping is easy to get wrong.
Example (PHP)
$stmt = $pdo->prepare("SELECT * FROM orders WHERE id = ?");
The order ID from the user goes in the ?. It is never treated as SQL code.
Use when
Use PDO or mysqli with bound parameters for every query that uses user input.
Learn more in the lesson: 46.4 Web Servers and MySQL Interview Questions