Ravi Sir's Cyber Security Cards › Comparison Cards
Alerting vs Threat Hunting
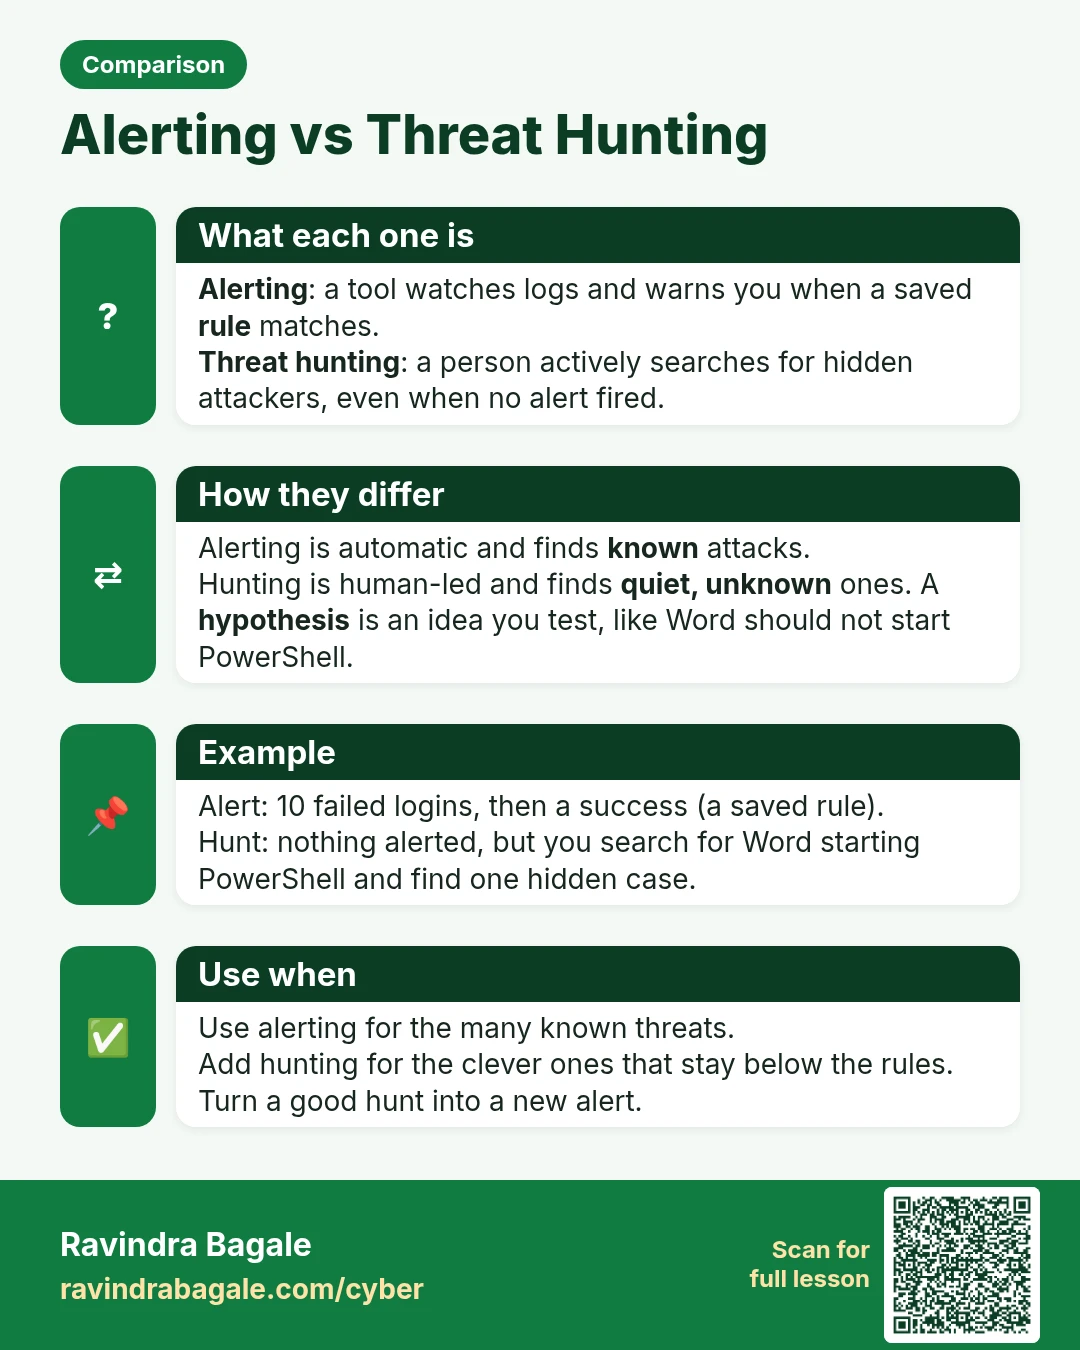
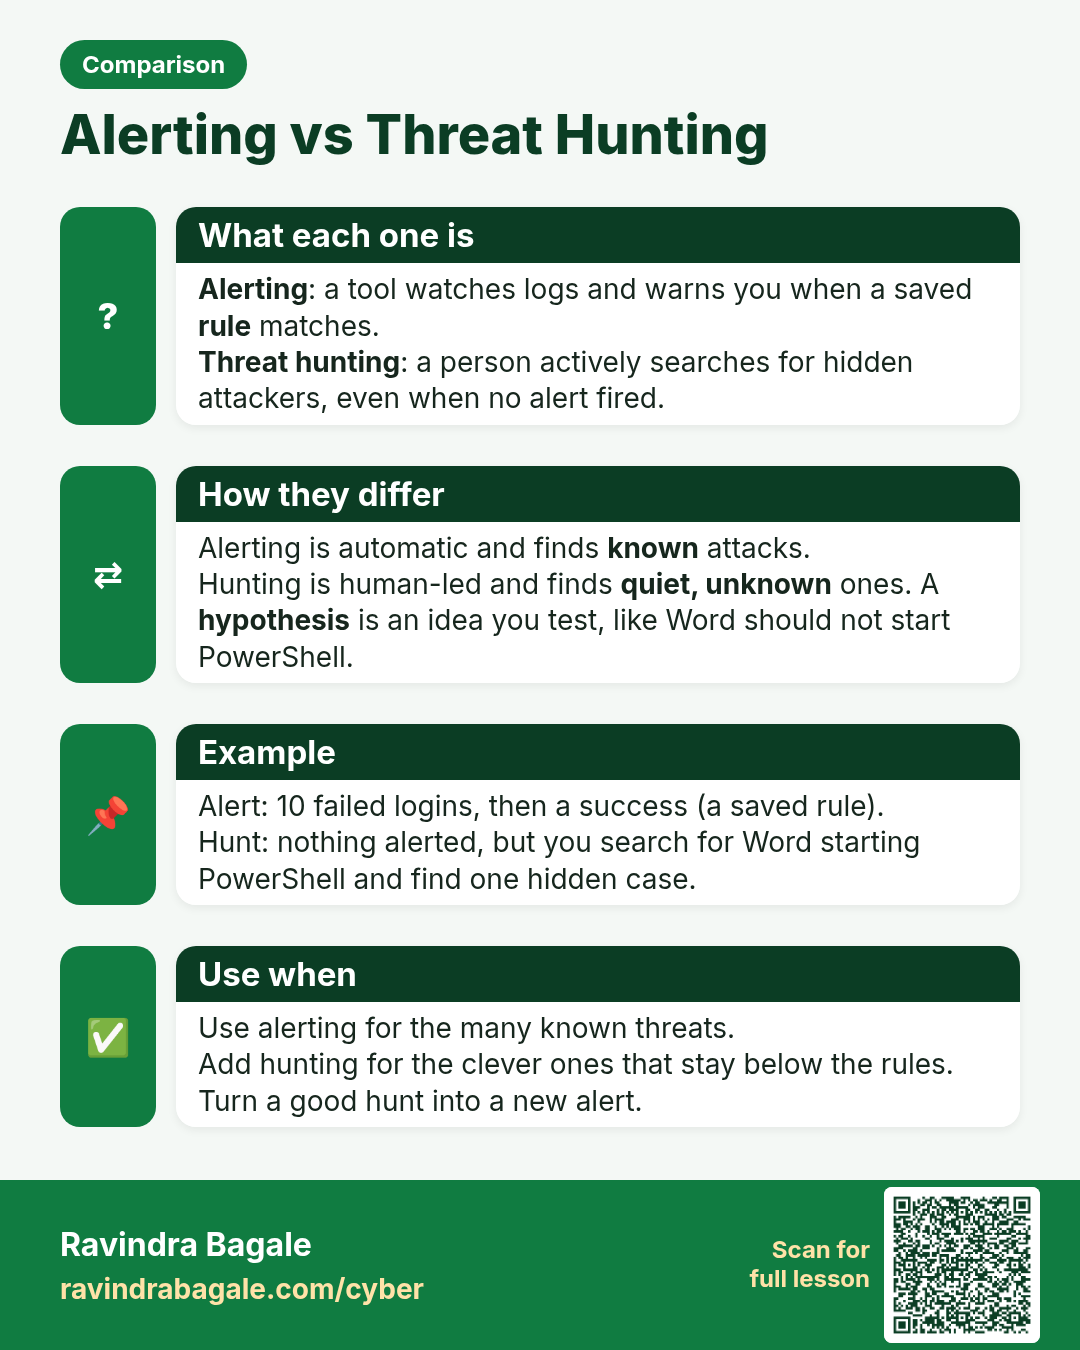
Comparison card: Alerting vs Threat Hunting. Easy English, with a real example. Scan the QR for the full lesson.
Read card text
What this card says
What each one is
Alerting: a tool watches logs and warns you when a saved rule matches.
Threat hunting: a person actively searches for hidden attackers, even when no alert fired.
How they differ
Alerting is automatic and finds known attacks.
Hunting is human-led and finds quiet, unknown ones. A hypothesis is an idea you test, like Word should not start PowerShell.
Example
Alert: 10 failed logins, then a success (a saved rule).
Hunt: nothing alerted, but you search for Word starting PowerShell and find one hidden case.
Use when
Use alerting for the many known threats.
Add hunting for the clever ones that stay below the rules. Turn a good hunt into a new alert.
Learn more in the lesson: 31.10 Threat Hunting