Cyber Security Interview Questions and Answers › Cyber Security
How should passwords be stored? What is a salt?
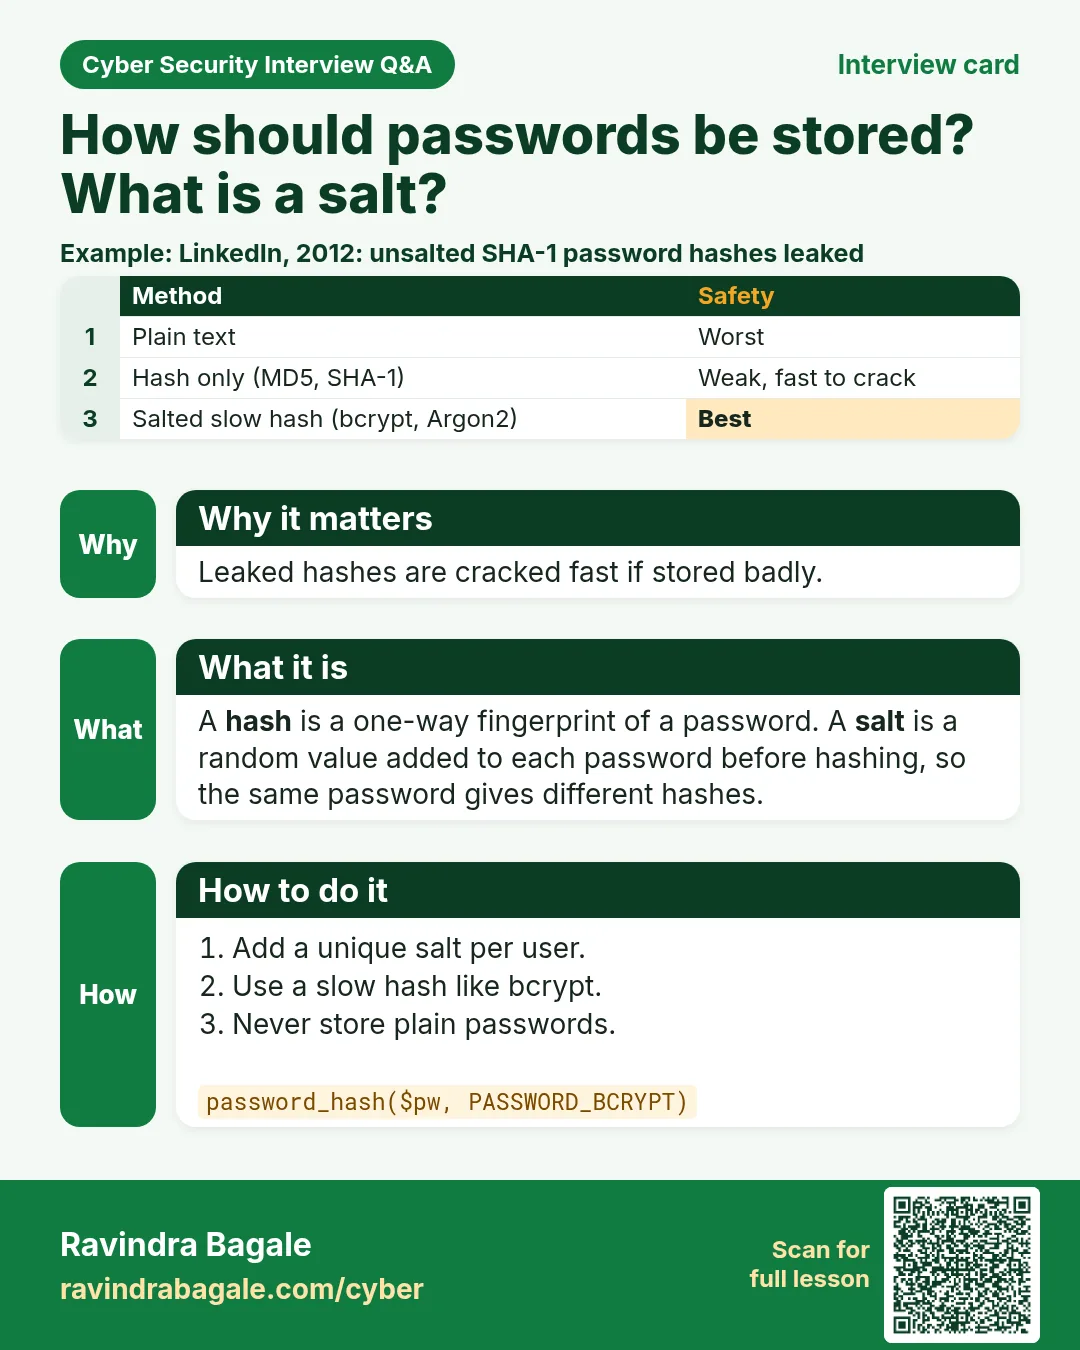
A hash is a one-way fingerprint of a password. A salt is a random value added to each password before hashing, so the same password gives different hashes. Leaked hashes are cracked fast if stored badly.
Read card text
What this card says
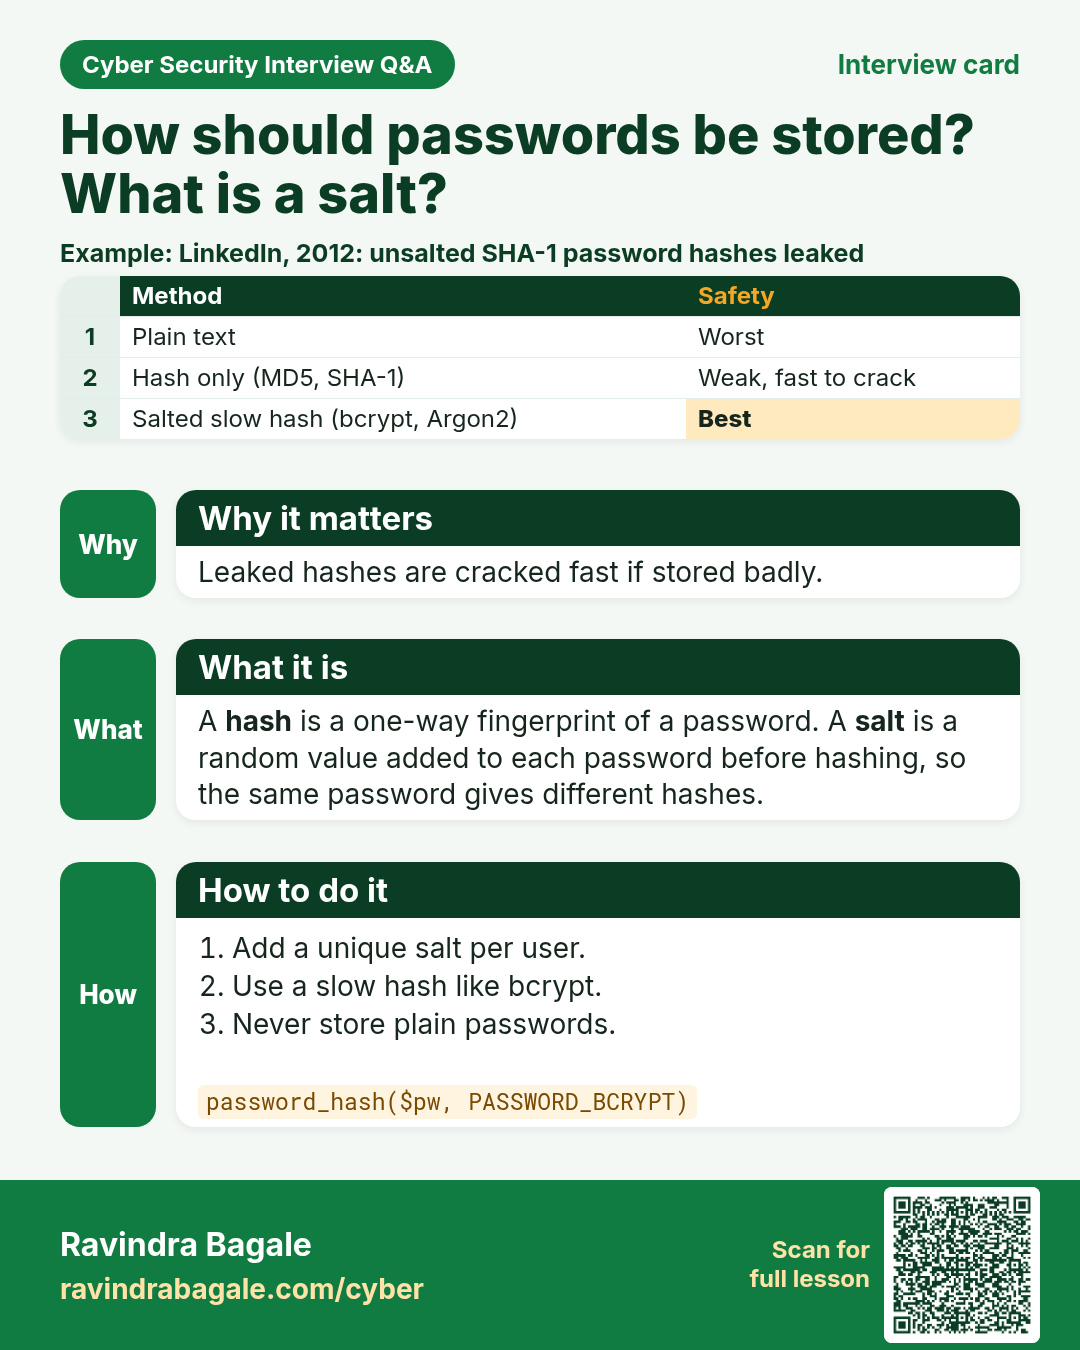
A hash is a one-way fingerprint of a password. A salt is a random value added to each password before hashing, so the same password gives different hashes. Leaked hashes are cracked fast if stored badly.
Learn more in the lesson: 22.1 How Passwords Are Stored